 www.mynewsdesk.com
Ukraine and NATO Conduct Major Military Exercises in Baltic Sea Region
Article Content
Browse articles 
- •Aurora 26 involves 18,000 troops from 12 nations, including Ukraine.
- •Ukrainian drone teams are sharing expertise in modern defense tactics.
- •The exercise is a response to Russia's aggression, enhancing NATO's collective defense.
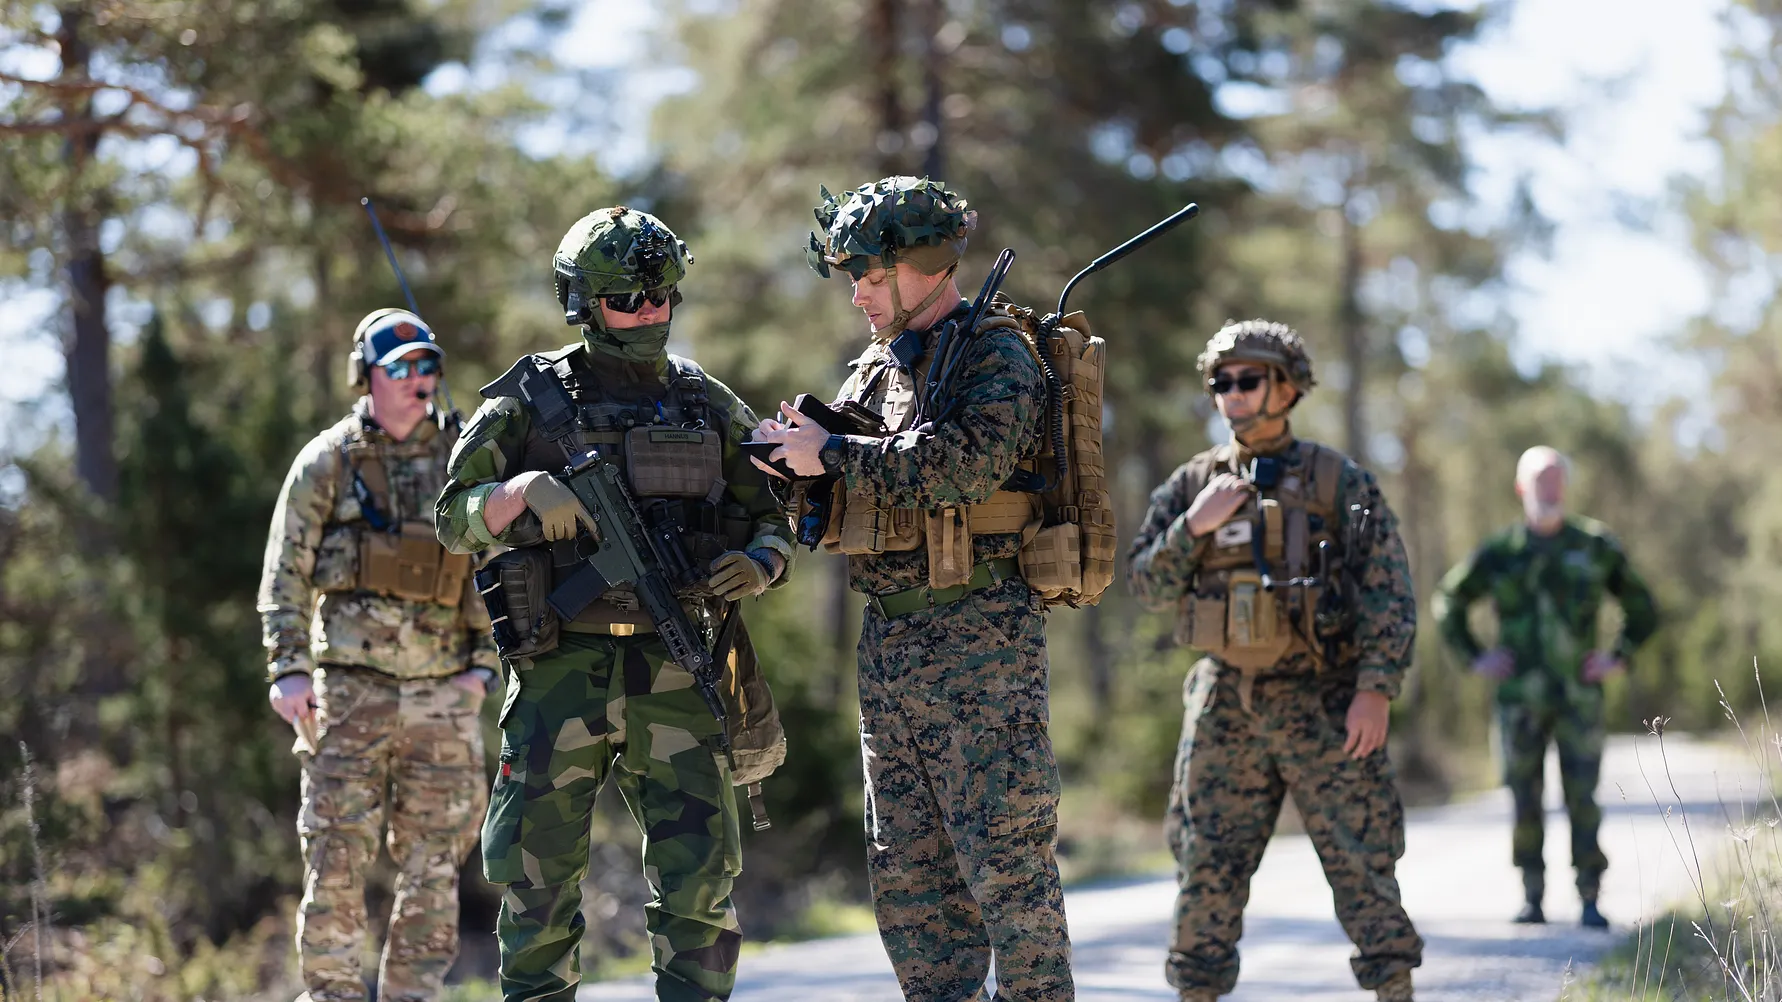
Sweden is hosting the Aurora 26 military exercises from April 27 to May 13, 2026, involving over 18,000 troops from 12 allied nations, including Ukraine. The exercises focus on the defense of Gotland Island and the Baltic Sea, emphasizing rapid deployment and coordination among NATO allies. Ukrainian drone teams are participating, sharing expertise in counter-drone tactics and drone warfare. The drills are a response to heightened security concerns due to Russia's ongoing aggression against Ukraine, marking Sweden's first exercise as a fully integrated NATO ally. The exercises validate Sweden's operational plans and its ability to support NATO forces in crisis scenarios.
Ask AI about this cluster
Answers cite the sources they use
Updated 133d ago How this analysis works
Timeline
2026-04-27
Aurora 26 military exercises begin
Sweden initiates large-scale military drills with 18,000 troops from 12 nations, focusing on Baltic Sea defense.
United24Media2026-05-10
Ukrainian drone teams participate
Ukrainian forces lead unmanned systems training, enhancing NATO's counter-drone capabilities during Aurora 26.
www.mynewsdesk.com2026-05-13
Aurora 26 exercises conclude
The military exercises are scheduled to end, having validated Sweden's operational readiness and NATO cooperation.
United24MediaMore articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…