 Pajhwok
Ukraine Proposes Halt to Attacks on Critical Infrastructure Amidst Ongoing Conflict
Article Content

- •Ukraine is willing to halt attacks on critical infrastructure if Russia does the same.
- •Zelenskyy demands credible guarantees from partners regarding Russia's compliance.
- •Recent Ukrainian drone strikes have targeted Russian oil refineries, affecting fuel supplies.
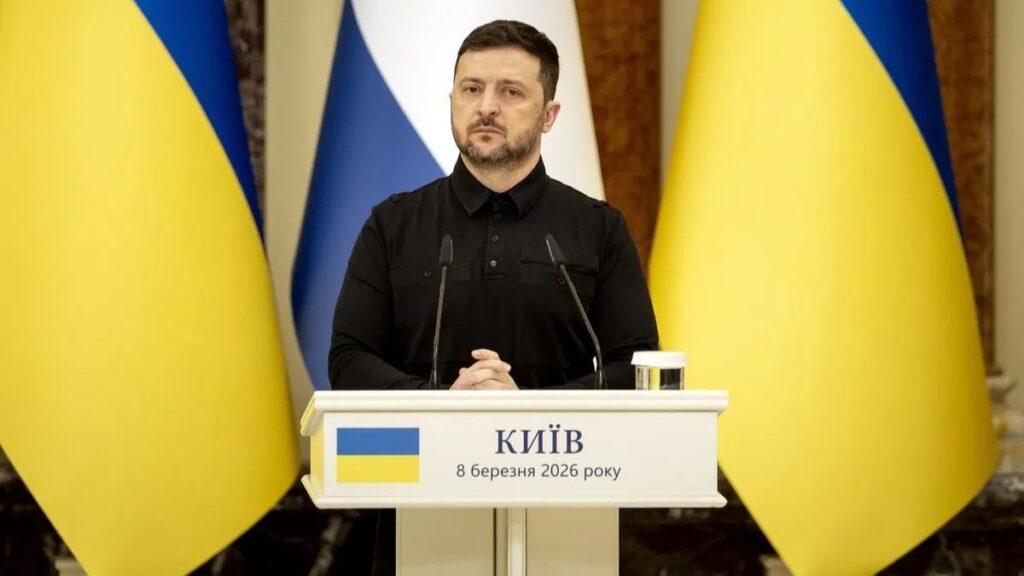
Ukrainian President Volodymyr Zelenskyy announced Ukraine's readiness to agree to a mutual cessation of attacks on critical infrastructure, contingent upon guarantees from partners that Russia will reciprocate. This proposal includes halting strikes on energy facilities, logistics, and food supply routes. Zelenskyy emphasized the need for a credible and long-term agreement rather than a temporary pause. The proposal follows claims by U.S. President Donald Trump that both nations had reached an understanding regarding energy facility attacks. However, Zelenskyy expressed skepticism about Russia's commitment to such an agreement. The ongoing conflict has seen Ukraine targeting Russian oil refineries, impacting fuel production and causing shortages in certain areas. The situation remains fluid, with both sides assessing the potential for de-escalation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Truth Social in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…