 mod.gov.ua
Ukraine Secures Meteor Missiles for Gripen Fighters
Article Content

- •Ukraine will receive Meteor missiles to enhance air combat capabilities.
- •The delivery is synchronized with the arrival of Gripen fighter aircraft in early 2027.
- •Meteor missiles are expected to counter Russian glide bomb threats effectively.
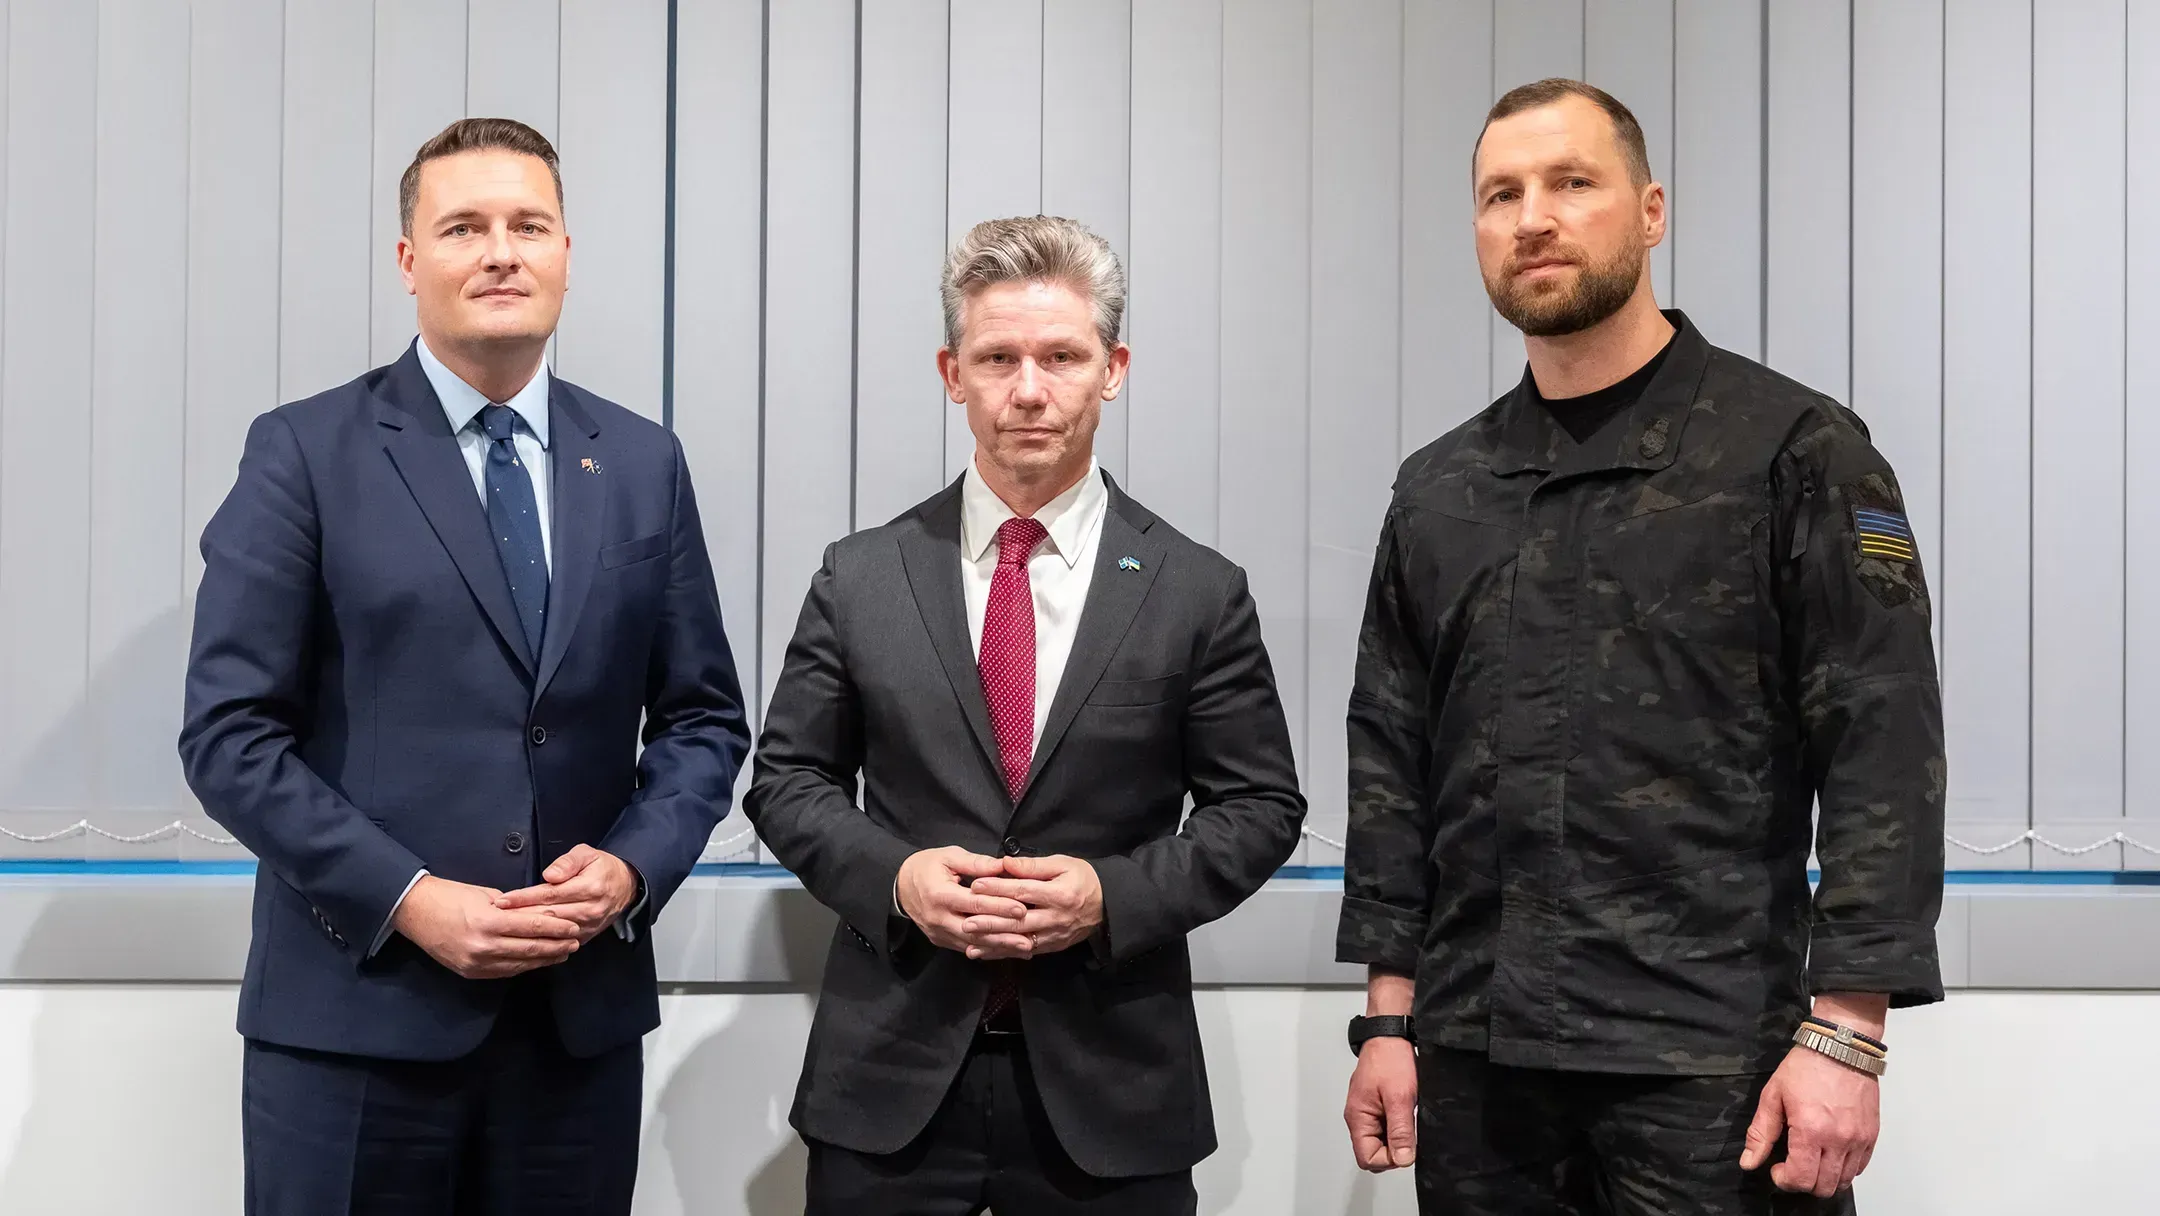
On November 18, 2026, Ukraine's Defense Minister Evgeniy Khmara, alongside officials from Sweden and the UK, signed a letter of intent in Brussels to enhance Ukraine's air defense capabilities. This agreement includes the delivery of Meteor air-to-air missiles, which are expected to arrive with the Saab Gripen fighter aircraft in early 2027. The Meteor missiles are designed to counter Russian aircraft, particularly those deploying glide bombs, significantly improving Ukraine's air combat effectiveness. The Meteor missile features advanced technology, including a ramjet engine, allowing it to maintain speed and track targets more effectively than conventional missiles. This initiative is part of ongoing international support for Ukraine amid the ongoing conflict with Russia, which has seen a significant imbalance in air power since the invasion began in February 2022. The Gripen aircraft and associated missiles aim to provide Ukraine with an edge in air defense operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Common questions
When are the Meteor missiles expected to arrive?
What advantages do Meteor missiles provide?
Who is involved in the agreement?
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…
 Critical CVE-2026 Flaws in Control Web Panel Lead to Account Takeover Risks Control Web Panel (CWP) versions prior to 1.30.6 are affected by two critical vulnerabilities, CVE-2026-124020 and CVE-2026-124021, both disclosed on 2026-11-13. CVE-2026-124020 allows attackers to exploit a host header injection in the password recovery process, potentially leading to account takeover via a poisoned…