 Kyivindependent
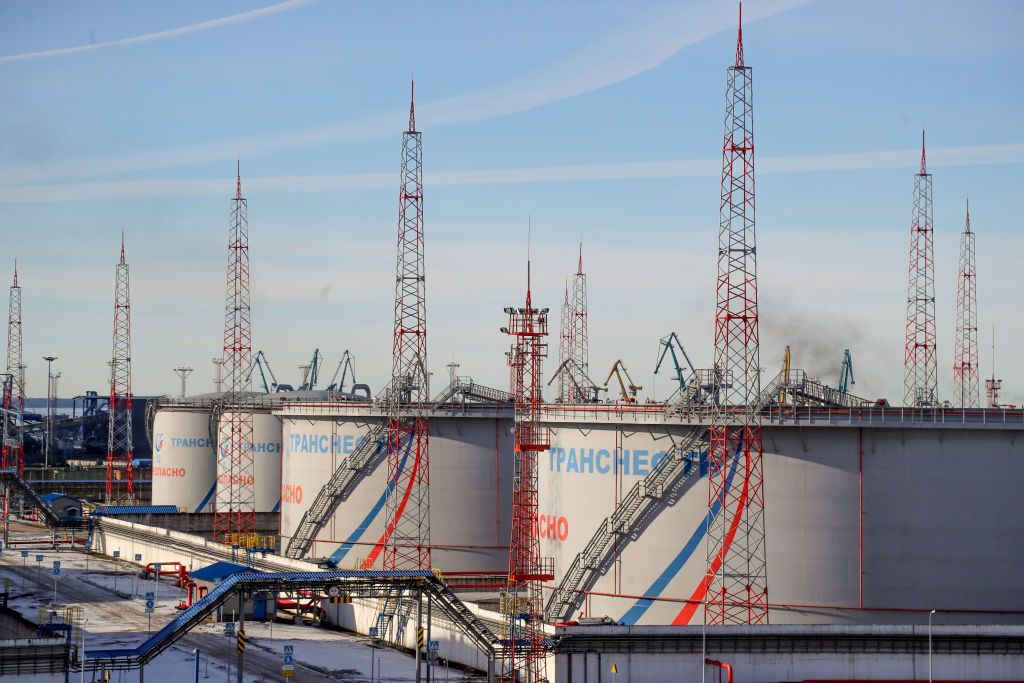
Ukraine Strikes Key Russian Fuel Hub with Drones
Article Content

- •Ukrainian drones targeted the Vtorovo oil pumping station, crucial for Moscow's fuel supply.
- •The attack caused a large fire and aimed to disrupt military logistics amid Russian missile strikes.
- •SBU plans to escalate operations against Russian infrastructure to weaken military capabilities.
On May 24, 2026, Ukrainian special operations forces successfully executed a drone strike on the Vtorovo oil pumping station in Russia's Vladimir region. This facility is crucial for supplying fuel to Moscow and its airports, including Sheremetyevo, Domodedovo, and Vnukovo. The attack, carried out by the SBU's Alpha unit, resulted in a significant fire covering approximately 800 square meters. The operation aimed to disrupt Russian military logistics amid a concurrent Russian missile barrage targeting civilian areas in Ukraine. SBU Head Yevhenii Khmara stated that the strike is part of Ukraine's strategy to weaken Russian military capabilities. The attack highlights the ongoing conflict's intensity and Ukraine's focus on targeting critical infrastructure. The SBU has indicated that further operations are planned to continue disrupting Russian fuel supplies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Transneft in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…