 Atlanticcouncil
Ukraine's Energy Infrastructure Under Cyber and Physical Attack
Article Content

- •Ukraine's energy infrastructure has been systematically attacked by Russia for four winters.
- •All thermal power plants in Ukraine have been damaged or destroyed, affecting heating for thousands.
- •Cyber vulnerabilities exist in heating systems, with past malware attacks indicating significant risks.
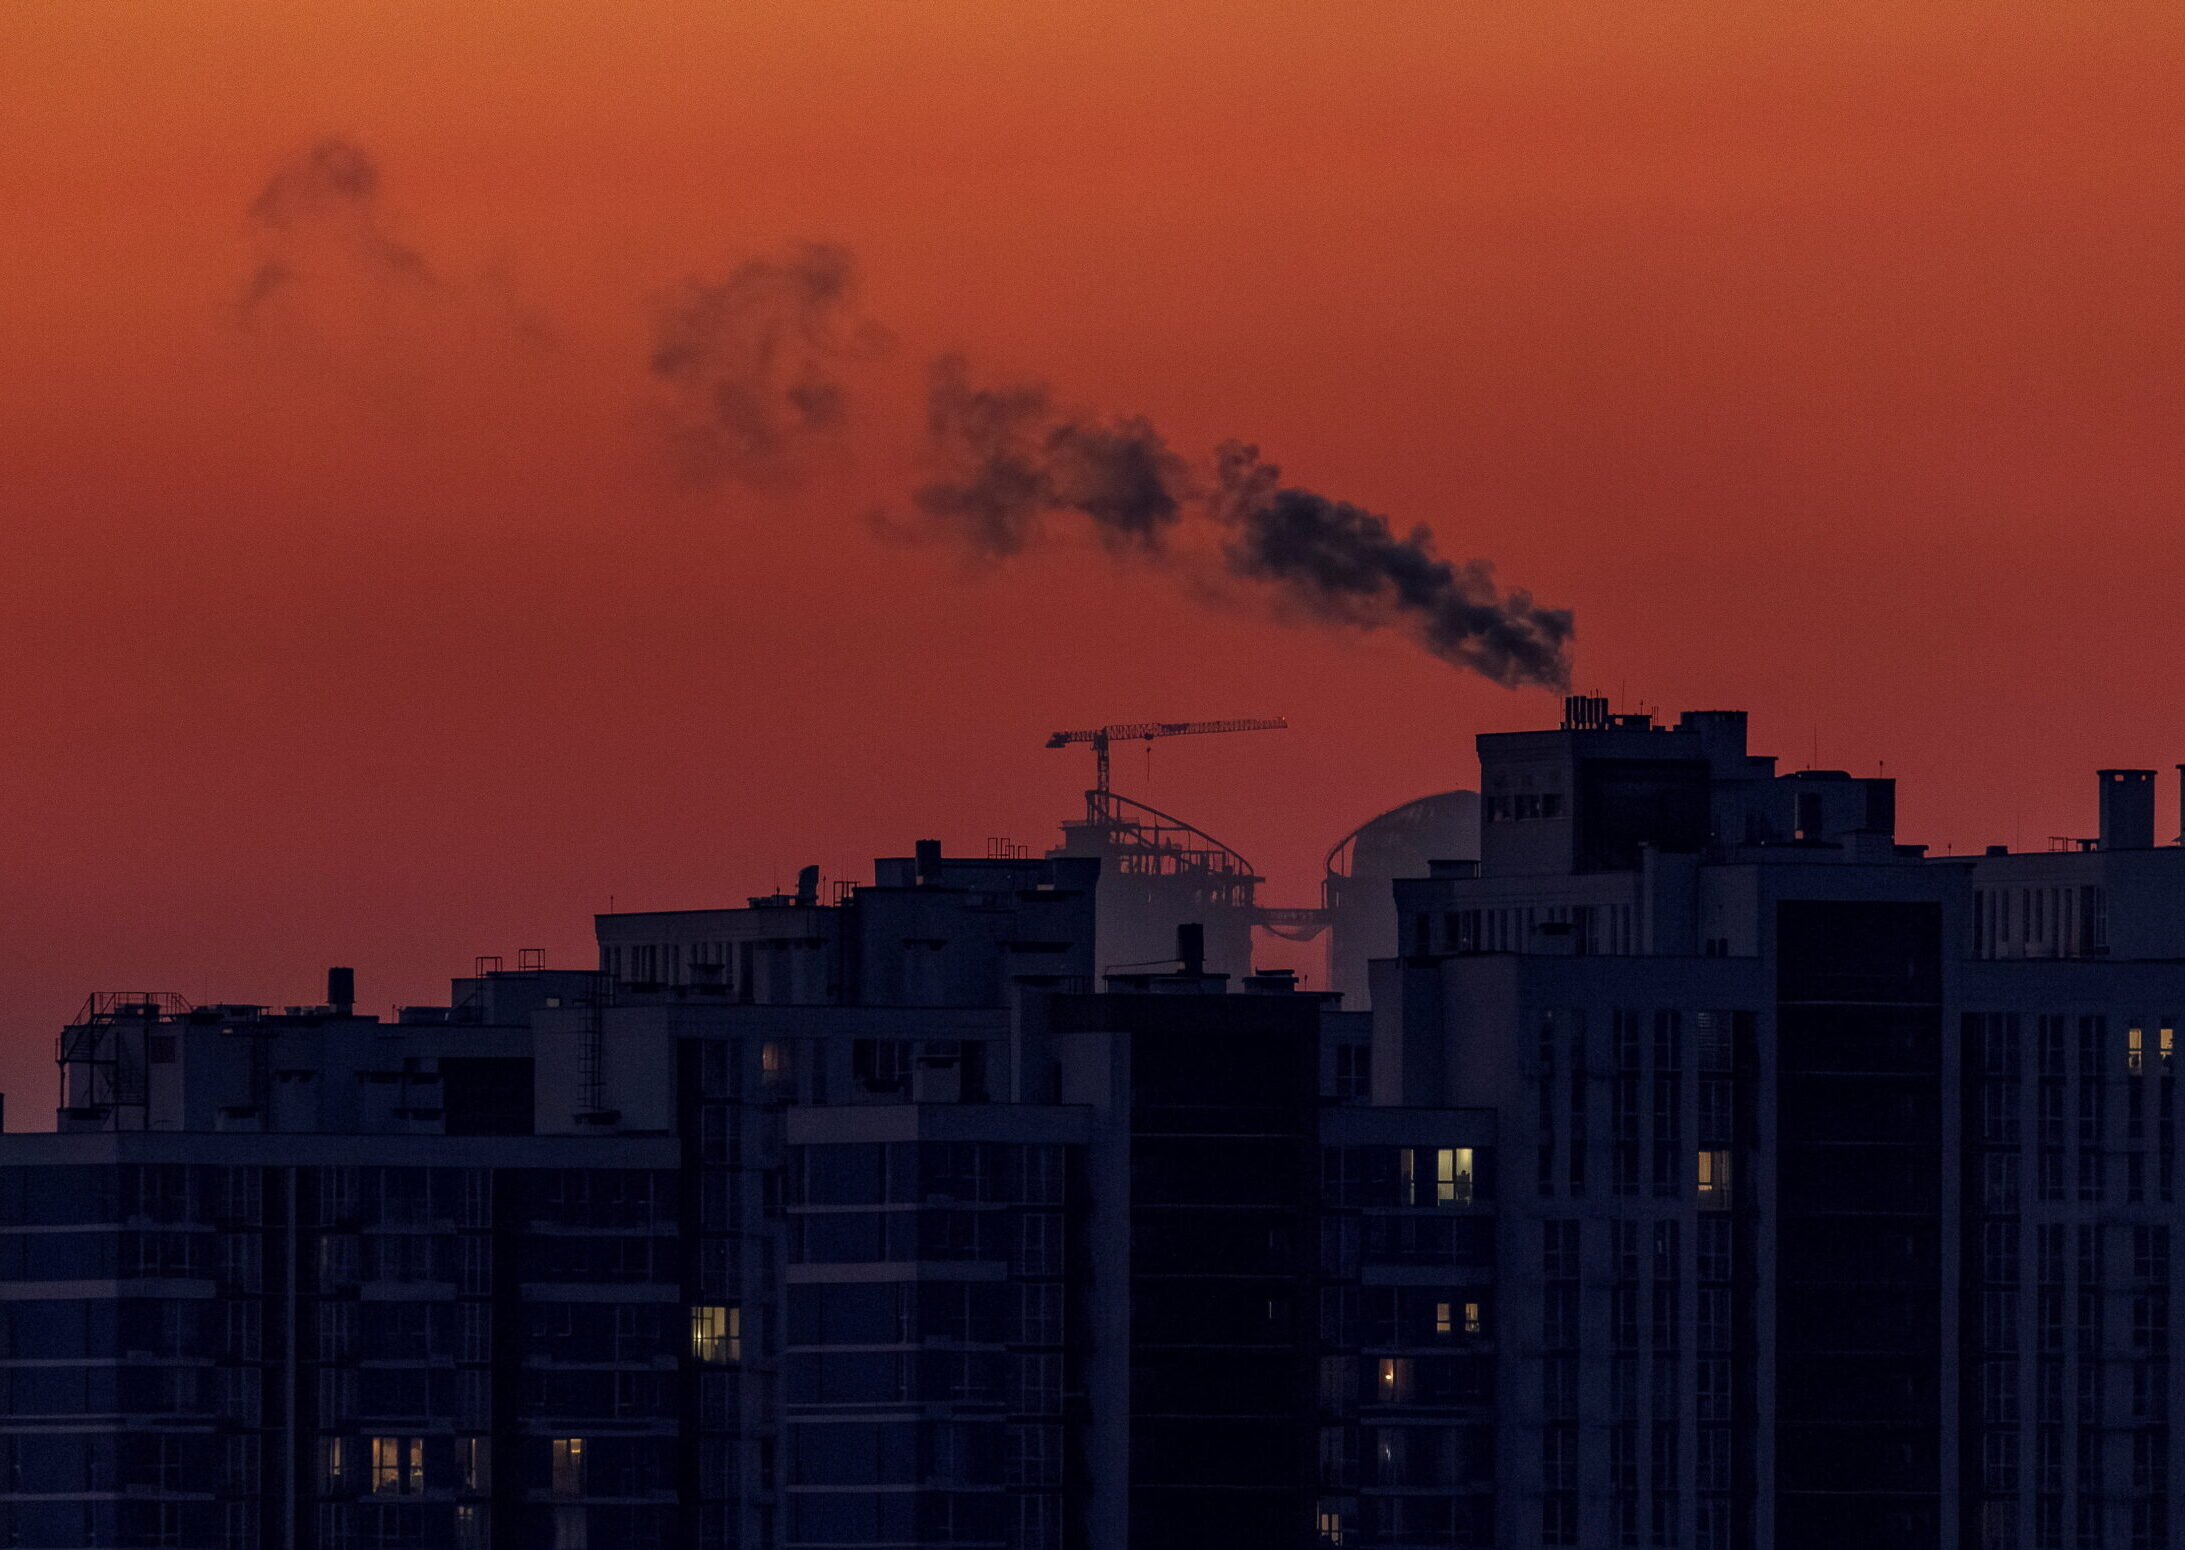
Ukraine has faced systematic Russian strikes on its energy infrastructure for four consecutive winters, with the most recent winter seeing near-daily attacks across 17 regions. All of Ukraine's thermal power plants have been damaged or destroyed, severely impacting central heating for thousands of residential buildings. Ukrainian operators have adapted by pivoting to mobile cogeneration units, allowing for independent generation of heat and electricity. The International Energy Agency (IEA) has noted that Ukraine's emergency response capabilities could serve as a model for other European nations, which rely on outdated centralized heating systems. The threat extends beyond physical attacks to potential cyber vulnerabilities, as demonstrated by previous malware targeting heating systems. In January 2024, a malware called FrostyGoop disrupted heating in Lviv, and a coordinated cyberattack in December 2025 targeted a Polish power plant, highlighting the risk to critical infrastructure across the region. The situation remains precarious as European countries remain unprepared for similar attacks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track FrostyGoop in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…