 United24Media
Ukraine's Starlink Access Throttled, Disrupting Military Drone Operations
Article Content

- •Starlink speed restrictions limit military drone operations in Ukraine.
- •Connectivity issues reported at speeds as low as 45 mph complicate missions.
- •Elon Musk claims U.S. military controls Starshield speed limits.
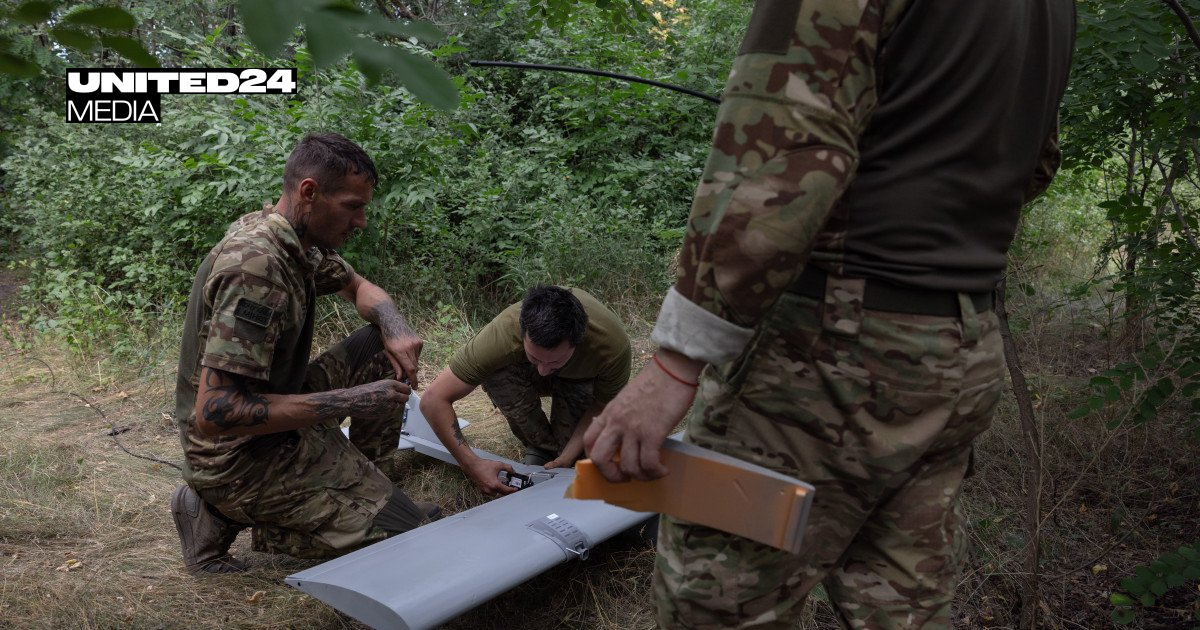
Ukraine's access to SpaceX's Starlink service was unexpectedly restricted, limiting speeds for military operations to 100 mph (160 km/h). This disruption, confirmed by Ukrainian officials, has complicated critical drone missions, including reconnaissance and strike operations. Reports indicate that some drones experienced connectivity losses at speeds as low as 45 mph. The Ukrainian Defense Ministry is investigating the cause of these restrictions, which have already led to the cancellation of several missions. SpaceX's Elon Musk stated that the U.S. government controls the Starshield system, implying that speed limits are determined by military directives. The situation follows recent political tensions, including U.S. President Donald Trump's controversial remarks regarding Ukraine's military actions. The impact of these restrictions is significant, as Ukraine heavily relies on Starlink for battlefield communications.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track SpaceX in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific operations are affected?
Who is responsible for the speed limits?
What is Ukraine doing in response?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…