 Pravda.Ua
Ukrainian Drone Attack Targets St. Petersburg Infrastructure
Article Content

- •A Ukrainian drone attack on St. Petersburg resulted in one death and multiple injuries.
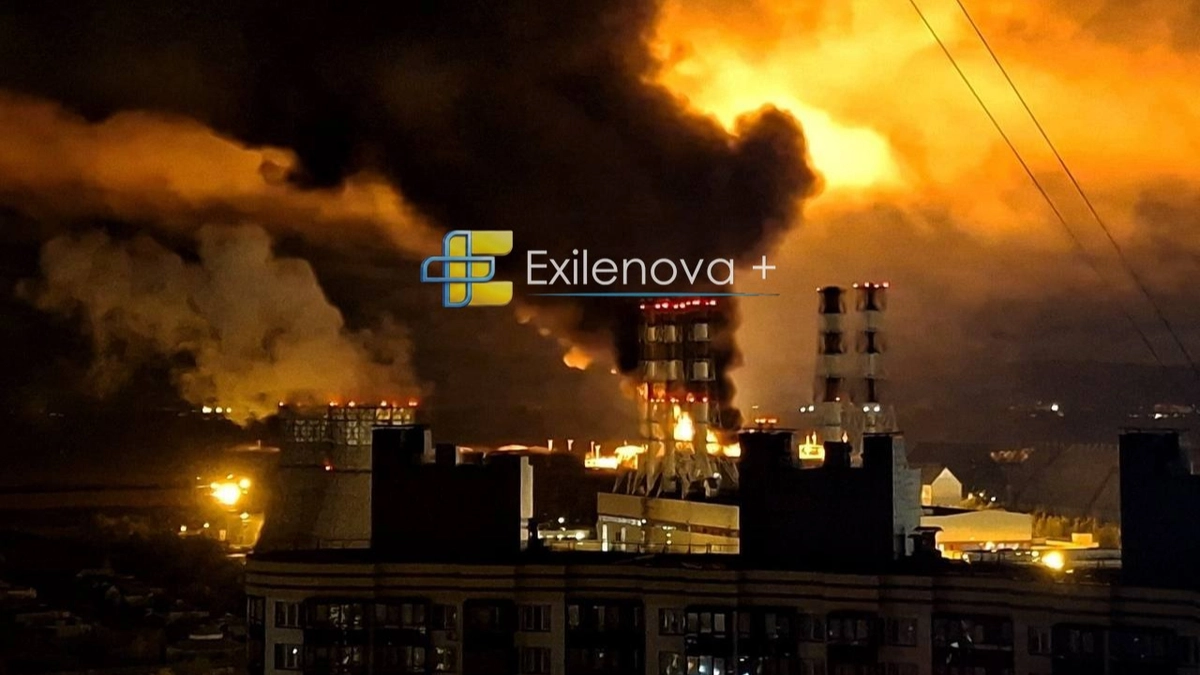
- •Key infrastructure, including an oil terminal and a data center, was targeted, causing significant fires.
- •Approximately 20,000 residents experienced power outages due to damage to electrical facilities.
On October 18, 2026, a significant Ukrainian drone attack struck multiple sites in St. Petersburg, including the St. Petersburg Oil Terminal and a VK data center, resulting in at least one death and five injuries. The attack caused widespread fires and power outages affecting approximately 20,000 residents. Governor Alexander Beglov reported that several residential buildings were damaged, and operations at the city's main airport were disrupted. The attack involved a large number of drones, with reports indicating that Russian air defenses shot down over 140 drones. The VK data center reported connectivity issues despite claims of normal operations. The incident marks one of the largest drone assaults on the region in recent years, with ongoing firefighting efforts and emergency responses in place.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Ozon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What areas were affected by the drone attack?
How many drones were involved in the attack?
What is the current status of emergency services?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…