 Kyivindependent
Ukrainian Drones Target Russian Data Center Amid Ongoing Conflict
Article Content

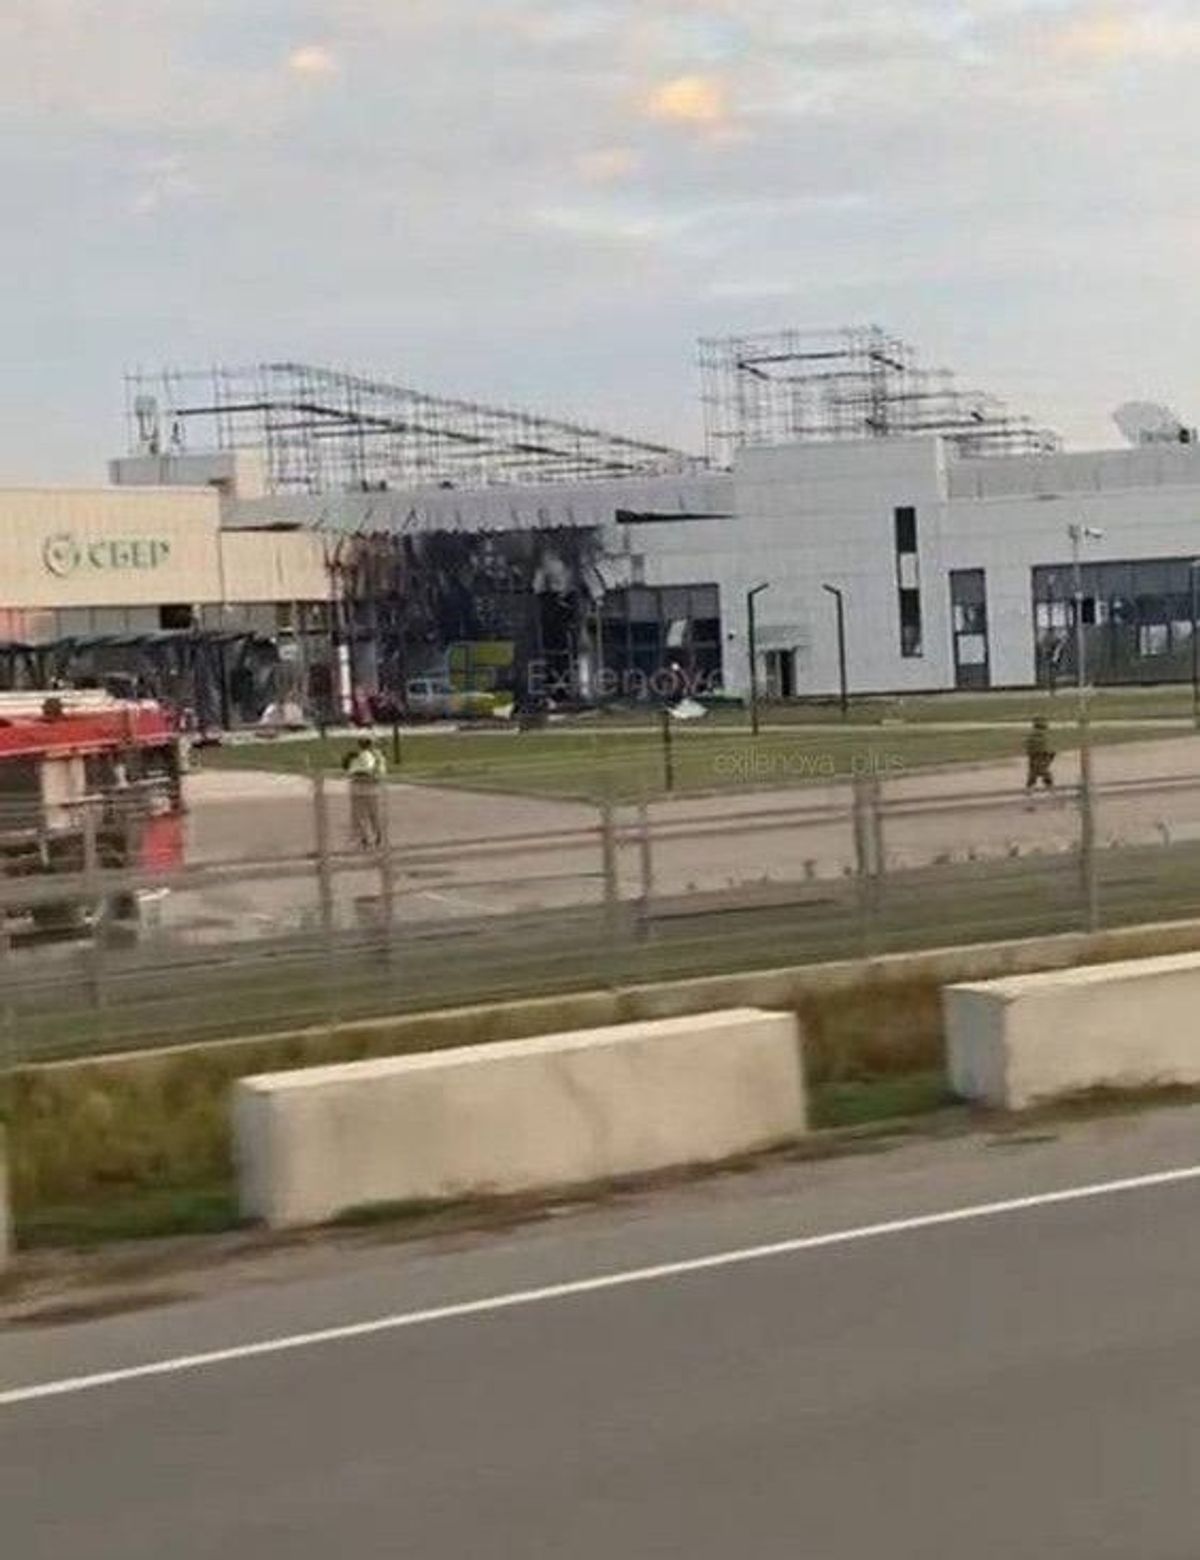
- •Ukrainian drones hit a Sberbank data center in Russia on October 14, 2026.
- •The attack is part of a broader strategy against Russian infrastructure amid ongoing conflict.
- •Debris from Russian drones also damaged artwork in Ukraine, highlighting the conflict's collateral impact.
On October 14, 2026, Ukrainian drones reportedly struck a Sberbank data center in Russia, marking a significant escalation in the ongoing conflict. The attack was characterized as deliberate and demonstrative by Ukrainian President Volodymyr Zelensky. In a related incident, debris from Russian drones caused damage to a contemporary artwork at a museum in northwestern Ukraine. The Ukrainian defense company Fire Point hinted at the attack's broader implications by referencing previous strikes on Russian targets. The conflict has intensified, with Russia launching a large-scale missile attack on Kyiv, resulting in civilian casualties and infrastructure damage. Ukraine continues to rely on advanced drone technology, including Starlink for operational support. The situation remains fluid, with ongoing military engagements reported across various fronts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Sberbank in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the target of the drone strike?
What damage occurred from the drone debris?
What is the current status of the conflict?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…