 En.Interfax.Ua
Ukrainian Flamingo Missile Strikes Russian Explosives Plant in Samara Oblast
Article Content

- •A Ukrainian FP-5 Flamingo missile struck the Promsintez explosives plant in Russia.
- •The plant is crucial for producing military-grade explosives, with an annual output of over 30,000 tonnes.
- •The Ukrainian Armed Forces confirmed the strike, indicating a strategic escalation in the conflict.
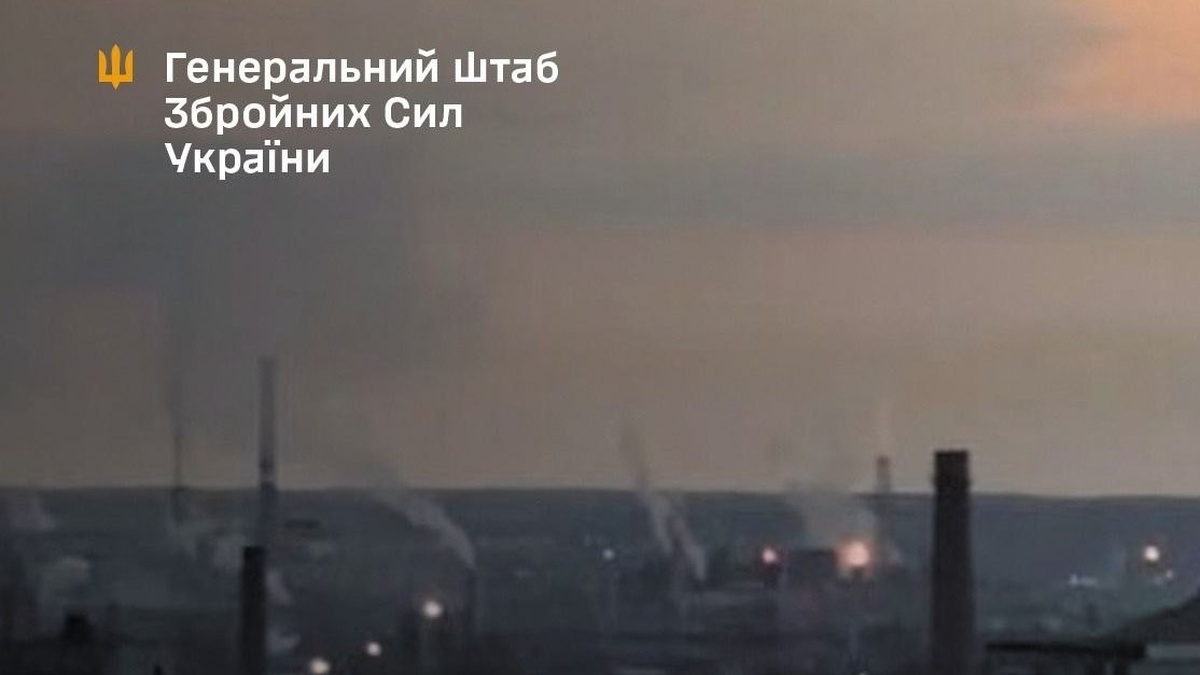
On March 28, 2026, a Ukrainian FP-5 Flamingo missile struck the JSC Promsintez explosives production plant in Chapaevsk, Samara Oblast, Russia. The attack was reported by Russian Telegram media channels, which shared images of a large fireball at the site. The Ukrainian Armed Forces confirmed the strike, stating that the facility specializes in manufacturing components for military-grade explosives. The plant produces over 30,000 tonnes of explosives annually, making it a significant target in the context of the ongoing conflict. The extent of the damage is currently being assessed. This incident marks a continued use of the Flamingo missile, which has been increasingly deployed by Ukraine since late 2025. The missile has a 1,000-kilogram warhead and a range of 3,000 kilometers. The attack is part of Ukraine's strategy to disrupt Russian military capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track JSC Promsintez in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…