 Pravda.Ua
Espionage Suspicions Against Ukrainian Journalists in Vienna Unsubstantiated
Article Content

- •Mykhailo Tkach was detained for 12 hours on espionage charges, which were later unsubstantiated.
- •Cameraman Yaroslav Bondarenko remains in custody and was injured during the detention.
- •The Ukrainian Embassy is demanding explanations from Austrian authorities regarding the detentions.
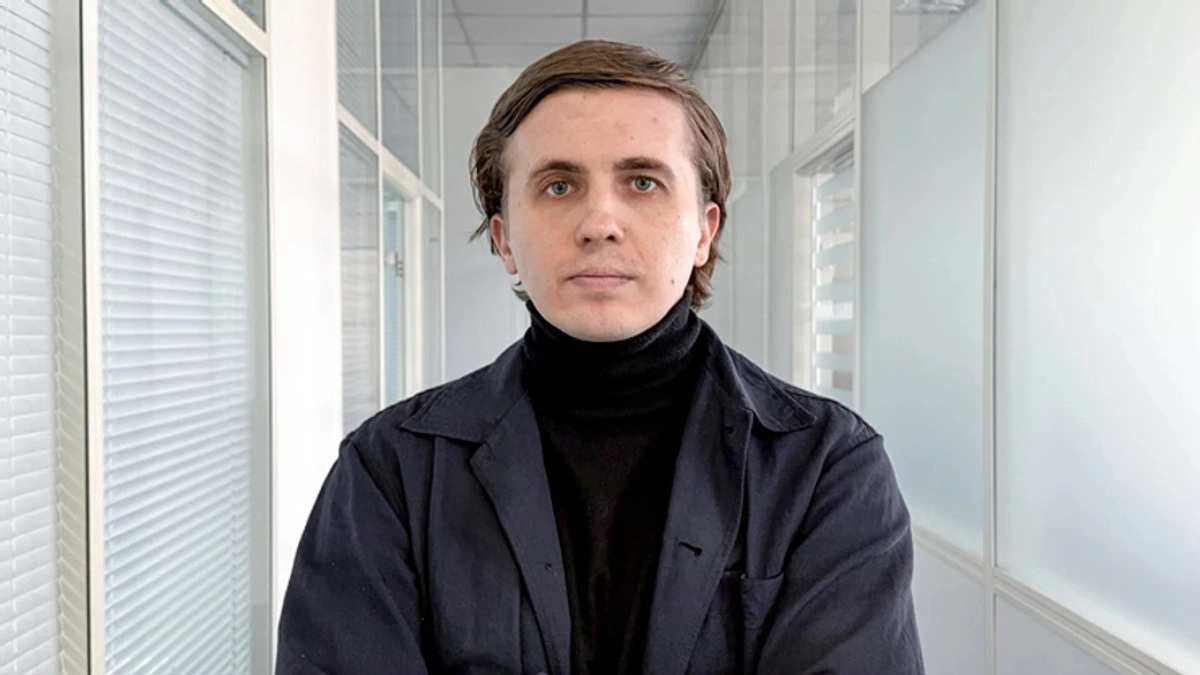
Mykhailo Tkach, head of the investigative department at Ukrainska Pravda, was detained in Vienna on October 8, 2026, along with cameraman Yaroslav Bondarenko, on suspicion of espionage. Tkach was released after 12 hours, while Bondarenko remains in custody and was reported injured during the detention. Austrian authorities confirmed that the suspicions against Tkach and Bondarenko were not substantiated. The journalists were in Vienna investigating former Ukrainian Prosecutor General Ruslan Kravchenko, who is believed to have fled to Austria. The Ukrainian Embassy in Austria is seeking clarification on the circumstances of the detentions and the legal grounds for the arrests. Four Ukrainian citizens were detained in total, with two others arrested earlier in the week on separate espionage charges. The situation has raised significant concerns regarding press freedom and the treatment of journalists in Austria.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (19)
Following this threat?
Track Ukrainska Pravda in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What were the charges against Tkach and Bondarenko?
What is the current status of Yaroslav Bondarenko?
What actions are being taken by the Ukrainian Embassy?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…