 News.Un
UN Security Council Renews Sanctions Against Haiti to Combat Gang Violence
Article Content

- •UN Security Council renewed sanctions on Haiti to combat gang violence.
- •Armed gangs control large areas, causing significant civilian casualties and displacements.
- •Sanctions include an arms embargo, travel bans, and asset freezes targeting gang leaders.
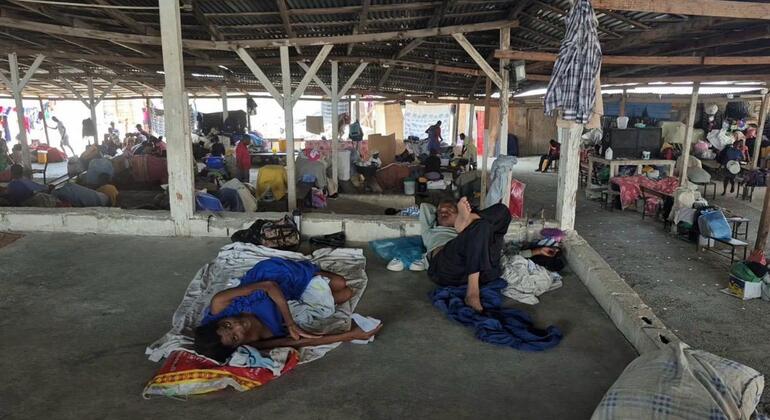
On 14 October 2026, the UN Security Council voted to renew sanctions on Haiti for one year, targeting individuals and entities involved in activities threatening the country's peace and security. Armed gangs control significant areas of Port-au-Prince, leading to widespread violence, including killings, sexual assaults, and kidnappings. The sanctions include an arms embargo, travel bans, and asset freezes aimed at disrupting the supply of weapons to these gangs. Despite efforts by Haitian authorities and international partners, the flow of illegal arms remains an issue, with estimates of up to 500,000 illegal weapons in circulation. The sanctions are intended to address the alarming rise in gang-related violence and the recruitment of children by these groups. The UN's Panel of Experts reported that the arms embargo is frequently violated, and only a few sanctioned individuals have had their assets frozen. The situation remains dire, with over 1.5 million people displaced due to gang violence.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What do the renewed sanctions entail?
How many people are affected by gang violence in Haiti?
What measures are being taken to enforce the sanctions?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…