 Theweek.In
Underwater Drone Threats Target Critical Maritime Infrastructure
Article Content

- •Ukraine's underwater drone attack on a Russian submarine signifies a new threat level.
- •Autonomous underwater drones can target critical maritime infrastructure with minimal detection.
- •Telecom companies are deploying drone swarms to safeguard undersea data cables from sabotage.
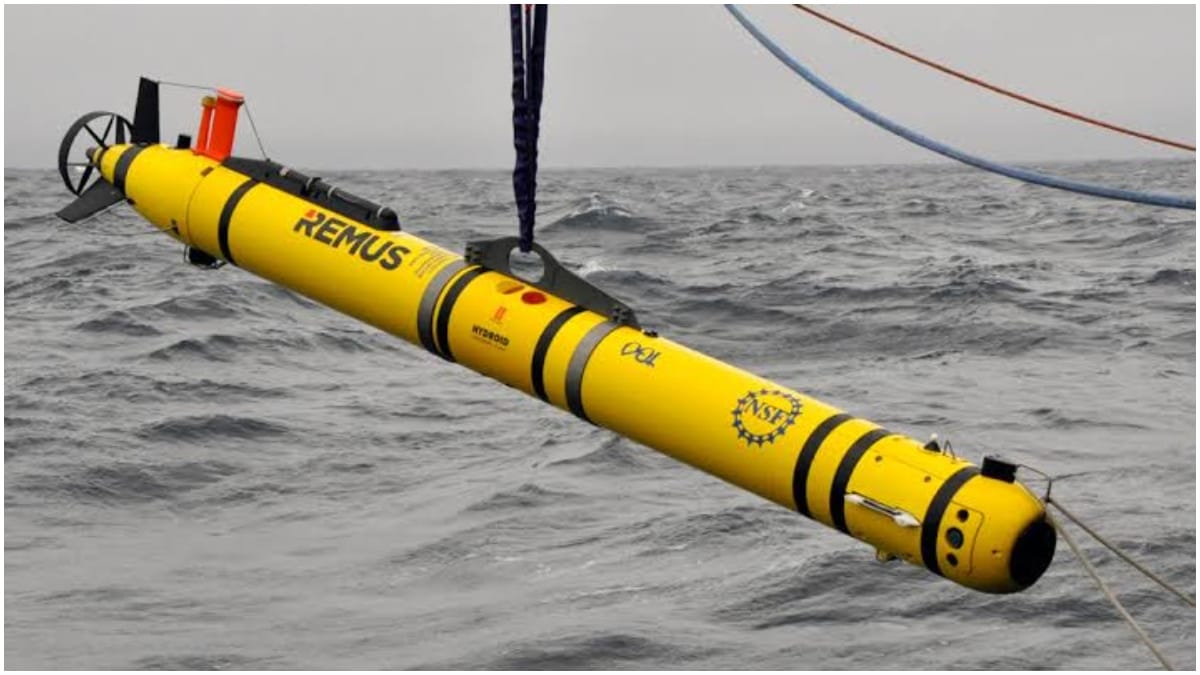
In December 2025, Ukraine reportedly used an underwater drone to attack a Russian Kilo-class submarine at Novorossiysk Naval Base, marking a significant escalation in maritime warfare capabilities. This incident highlights the vulnerability of naval assets to low-cost, autonomous underwater systems, which can bypass traditional defenses. The attack raises concerns about potential future threats from hostile states or terrorist groups using similar methods against critical infrastructure, such as oil platforms and shipping routes. The proliferation of affordable underwater drone technology, coupled with open-source autonomy software, makes these systems increasingly accessible to non-state actors. As a response, telecom companies are deploying autonomous underwater drone swarms to protect vital undersea fiber-optic cables from sabotage. This shift in maritime security strategy underscores the urgent need for enhanced defenses against emerging threats in the underwater domain.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the nature of the underwater drone attack?
How are telecom companies responding to underwater threats?
What are the implications of these drone technologies?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…