 Ktvu
United Airlines Flight Reports Possible Drone Strike During Landing Approach
Article Content

- •United Flight 1980 reported a possible drone strike at 3,000 feet during landing.
- •The FAA is investigating the incident, with no additional drone sightings reported.
- •The flight landed safely with no damage found on the aircraft.
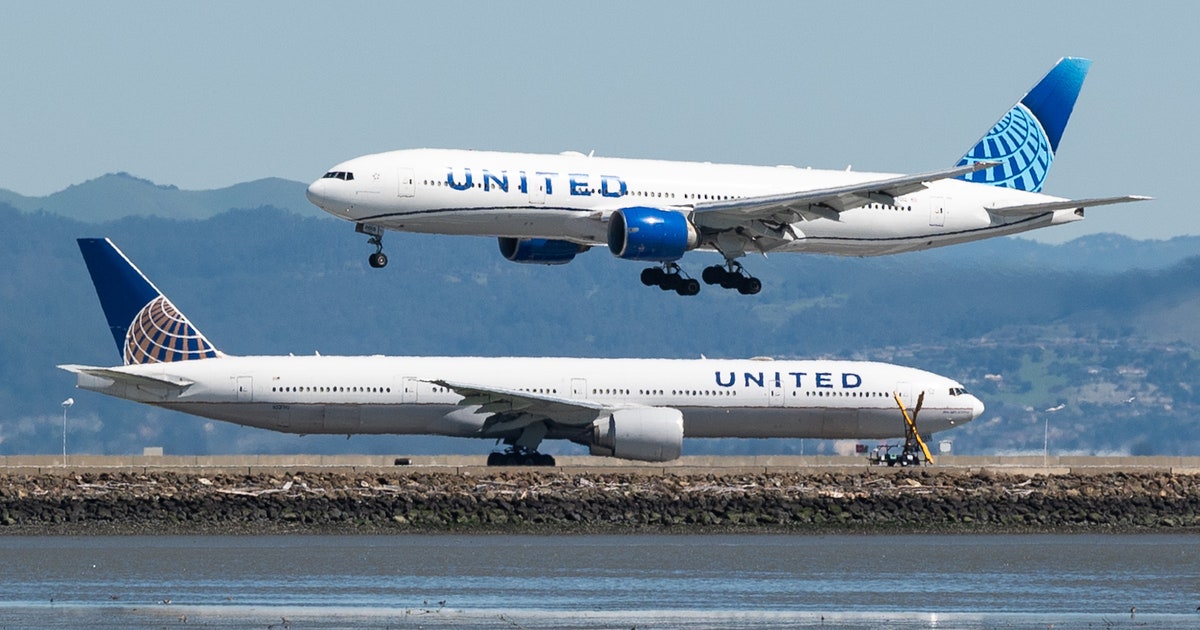
On April 29, 2026, United Airlines Flight 1980, a Boeing 737 from San Francisco, reported a potential drone strike while approaching San Diego International Airport. The pilot indicated that the aircraft, carrying 48 passengers and six crew members, may have collided with a small, shiny red drone at an altitude of approximately 3,000 feet. The Federal Aviation Administration (FAA) confirmed the incident and stated that it is under investigation. Air traffic control did not receive any additional reports of drone sightings in the area. Fortunately, the flight landed safely, and maintenance crews found no damage to the aircraft after inspection. Drone operations near airports are heavily regulated, with strict altitude limits and prohibitions against flying in restricted airspace. The FAA is reminding drone operators of these regulations to prevent similar incidents in the future.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Following this threat?
Track United Airlines in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…