 gigazine.net
Unprecedented Spike in Spyware Alerts for Apple Users Worldwide
Article Content

- •Apple users in 110 countries received unprecedented spyware alerts in August 2026.
- •Access Now reported a 30-40% increase in requests for assistance following the notifications.
- •Ukrainian soldiers were among those targeted, confirming the alerts' legitimacy with Apple.
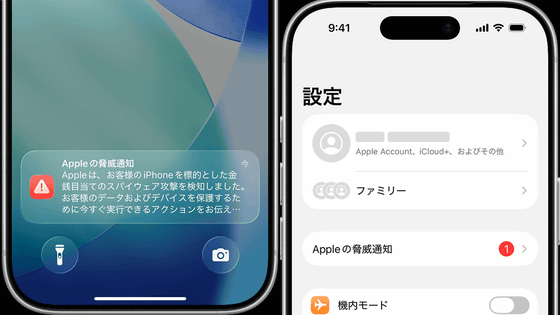
In August 2026, Apple reported an unprecedented number of users receiving 'threat notifications' regarding potential spyware attacks. Investigators revealed that alerts were sent to users in 110 countries, marking a significant increase in reported cases. The notifications, which Apple has issued since 2021, are designed to inform users targeted by spyware capable of compromising their devices. Access Now, an international nonprofit, noted a record number of individuals seeking assistance following these alerts, with a 30-40% rise compared to previous notifications. Among those affected are Ukrainian soldiers, who initially doubted the legitimacy of the alerts but later confirmed their authenticity with Apple. Experts suggest that the increase in notifications may be attributed to Apple adopting new methods for alerting users. The situation indicates a broader trend of spyware targeting individuals across various sectors, raising concerns about user safety and privacy.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Apple in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…