 Cyberscoop
Urgent Need for Post-Quantum Cryptography Transition Amid Quantum Threats
Article Content

- •Federal push for post-quantum cryptography initiated by executive orders.
- •Quantum computers may soon threaten existing encryption methods.
- •Transition to quantum-resistant encryption is urgent to protect sensitive data.
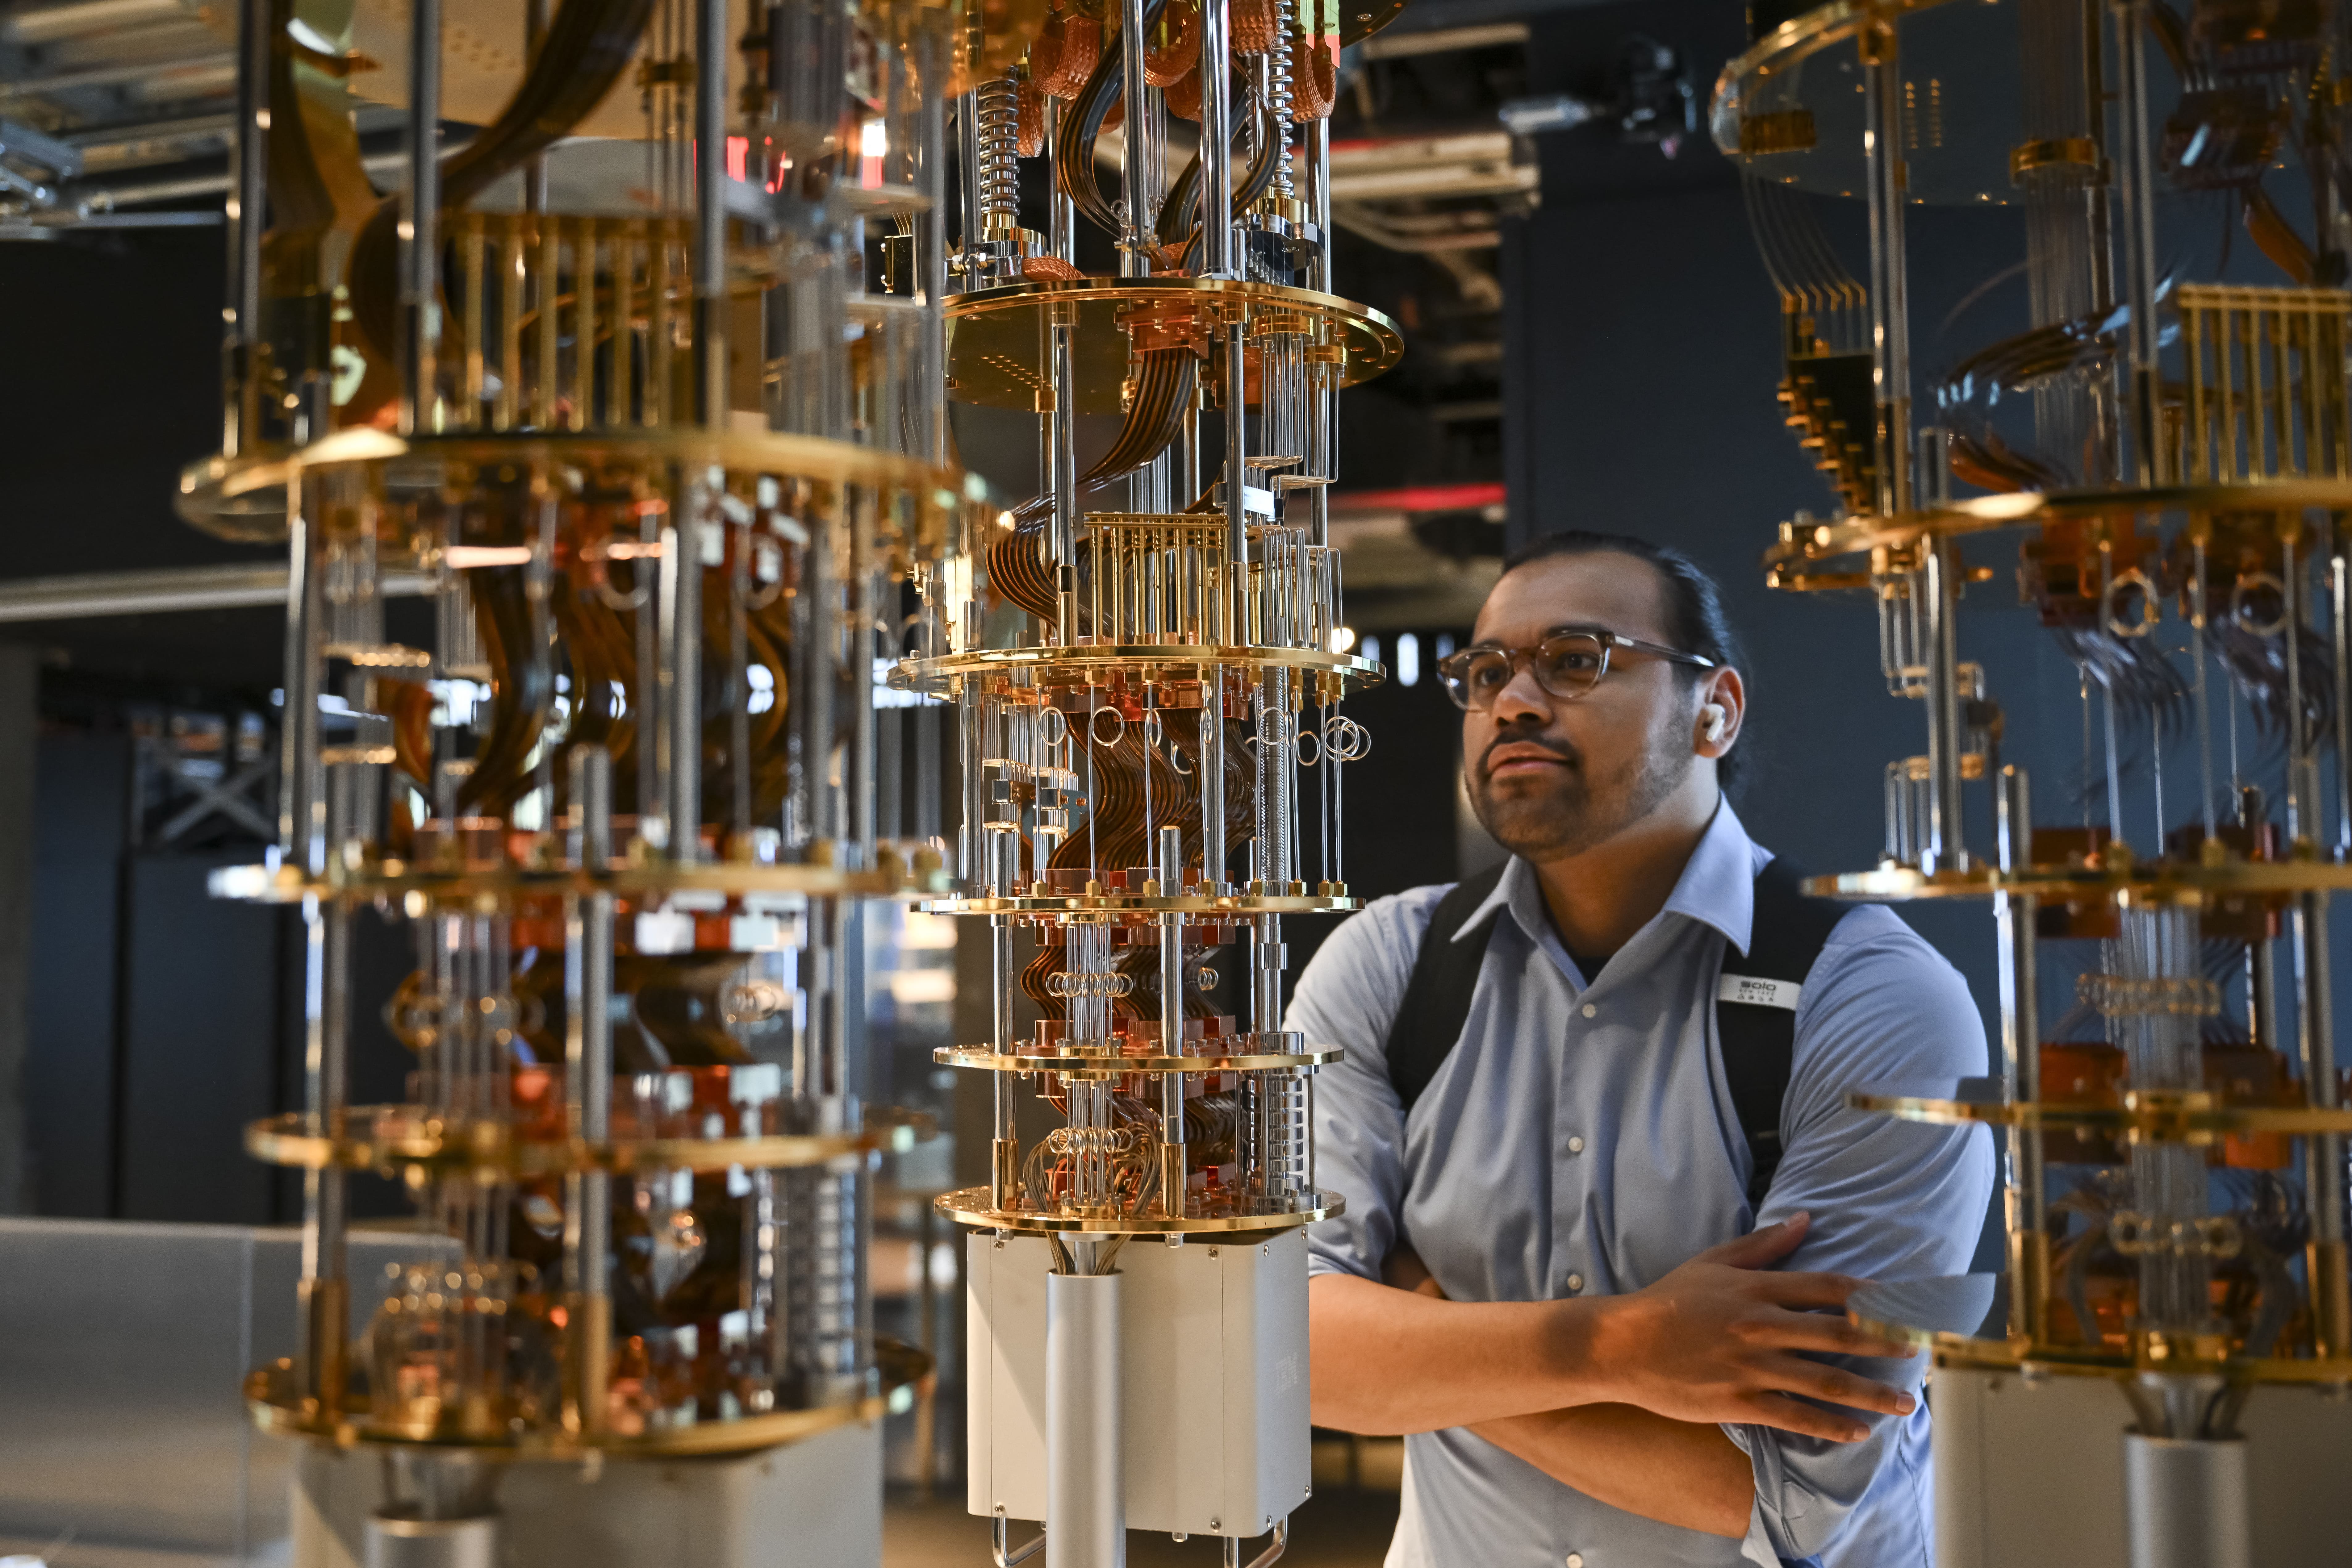
UCI researchers are adapting to a federal push for quantum research and post-quantum cryptography, following two executive orders signed by President Trump on June 22, 2026. These orders aim to accelerate the transition to quantum-resistant encryption due to the potential threat posed by quantum computers capable of breaking current encryption methods. The urgency is underscored by a 2035 target for completing the transition, which has been moved up for sensitive federal systems. Researchers warn that the transition must occur before quantum computers become operational, as the overhaul of encryption across government networks will take years. Meanwhile, foreign adversaries could exploit current encryption vulnerabilities, storing encrypted data for future decryption when quantum capabilities are available. The National Security Agency has begun selecting quantum-resistant algorithms, with deadlines set for 2030 and 2031 for key establishment and digital signatures, respectively.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What is the timeline for the transition to post-quantum cryptography?
What are the risks of not transitioning to post-quantum cryptography?
How are researchers preparing for this transition?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…