 Csis
U.S. and China Engage in Hybrid Warfare Amidst Geopolitical Tensions
Article Content

- •The U.S. is launching a hybrid warfare campaign to exploit CCP vulnerabilities.
- •China is shifting to a more offensive strategy as outlined by Xi Jinping, referencing Mao's tactics.
- •Both nations are preparing for a prolonged geopolitical struggle with significant military and economic implications.
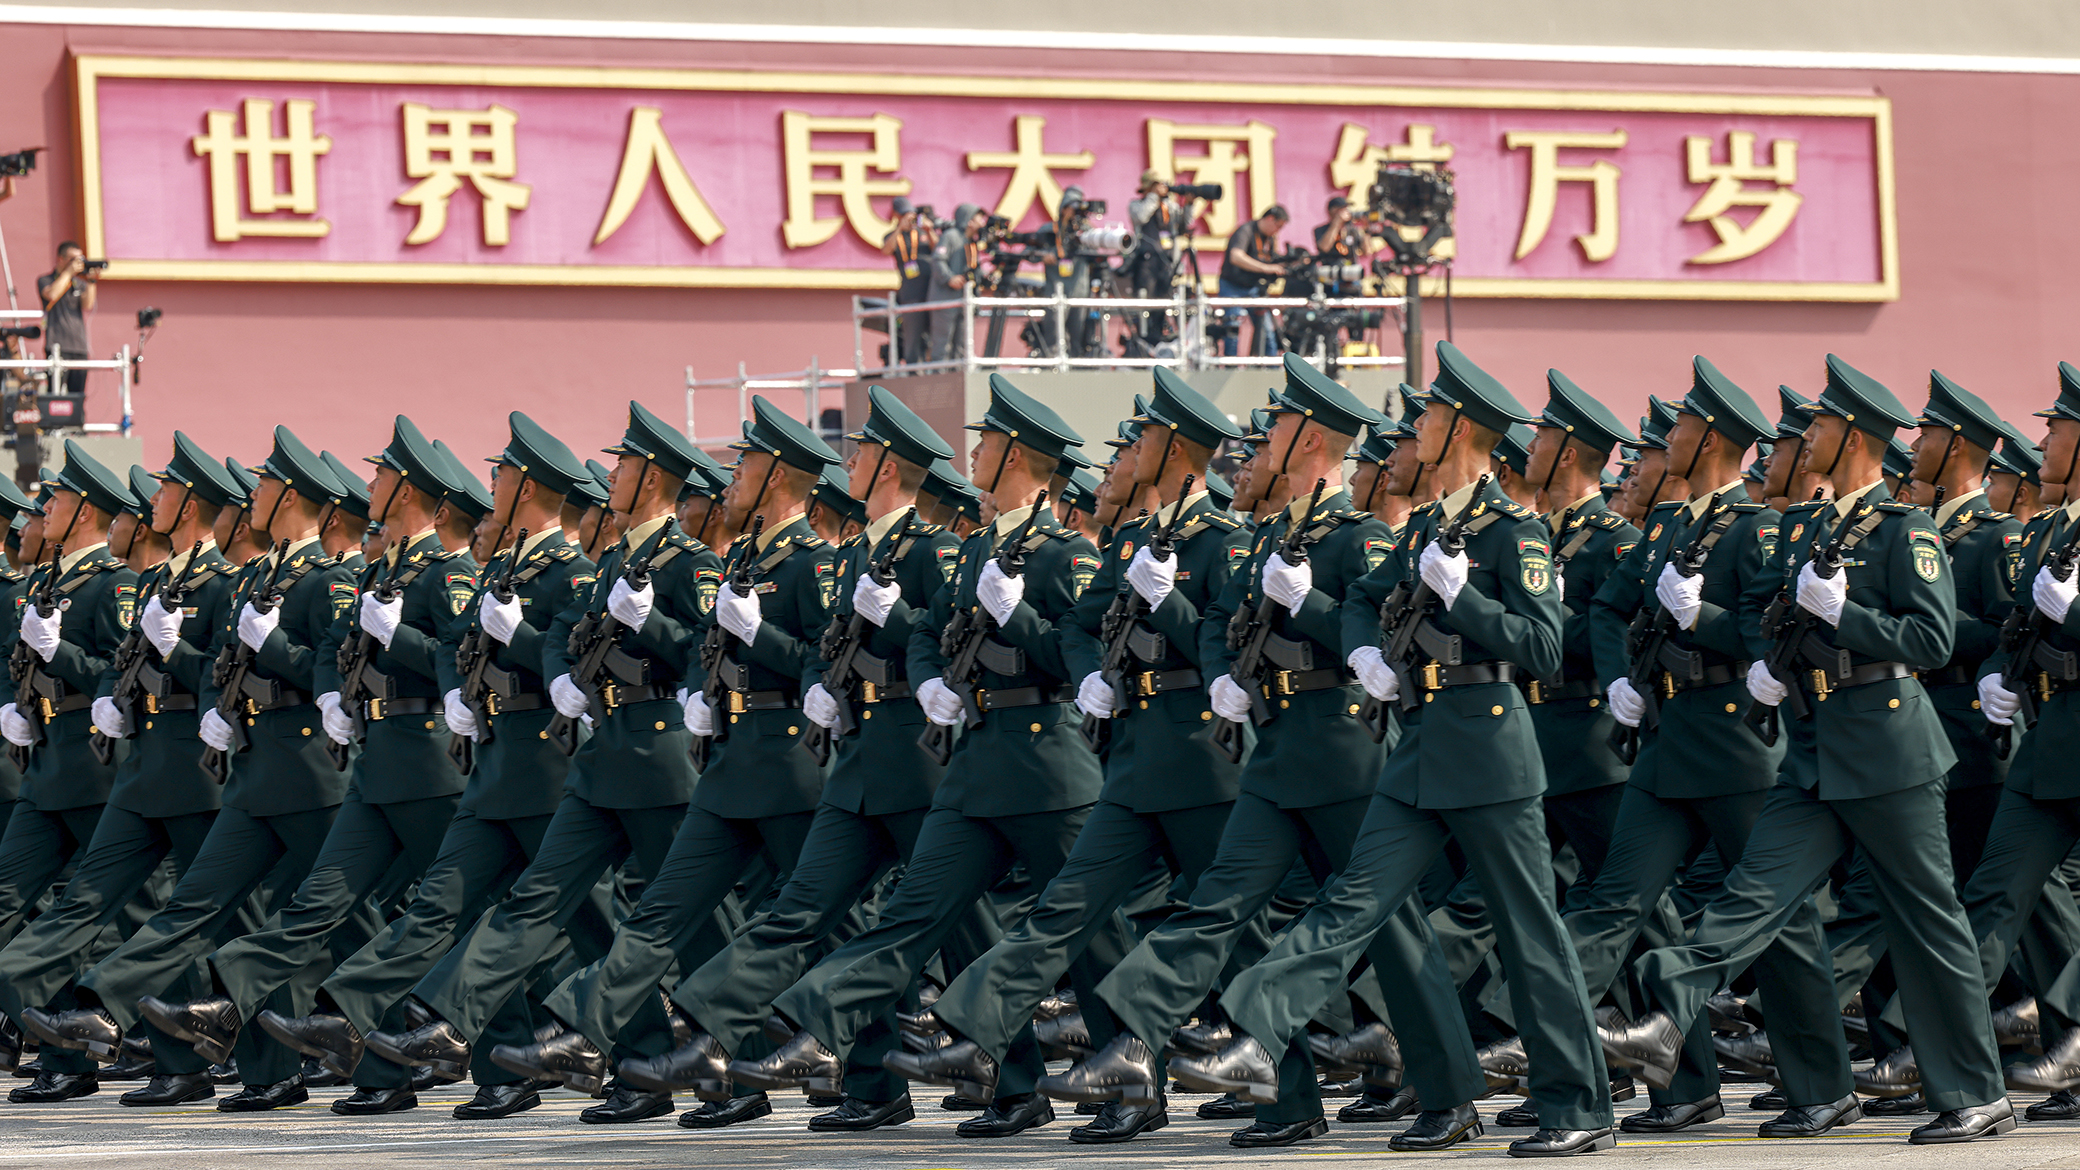
The United States is intensifying its hybrid warfare strategy against China, exploiting the vulnerabilities of the Chinese Communist Party (CCP) as outlined in a recent CSIS article. The CCP's weaknesses include endemic corruption, a focus on narratives over facts, and a lack of international allies. The U.S. aims to embarrass the CCP through various operations, including exposing hypocrisy and conducting aggressive intelligence activities. Concurrently, an opinion piece from the New York Times highlights Xi Jinping's strategic approach, referencing Mao Zedong's theory of protracted war, suggesting that China is transitioning from a defensive to a more offensive posture against the U.S. This dual narrative underscores the escalating tensions between the two nations, with both sides preparing for a long-term geopolitical contest. The U.S. is increasing military presence in East Asia, while China seeks to strengthen its position through strategic patience and resilience.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…