 Ukrinform
Ukraine and FBI Arrest Members of $40M Ransomware Gang
Article Content

- •Four members of a ransomware gang arrested for extorting over $40 million.
- •The group targeted various sectors, including oil, healthcare, and finance.
- •Attackers used social engineering tactics, posing as IT support to gain access.
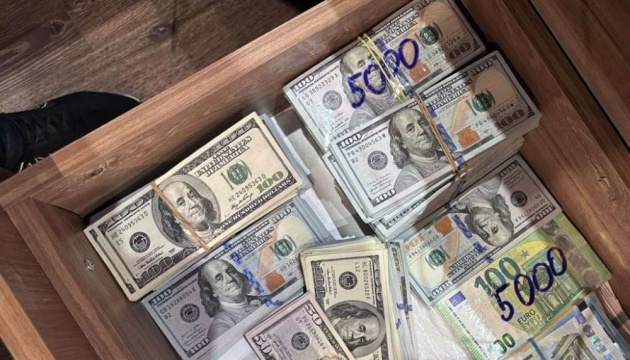
Ukrainian authorities, in collaboration with the FBI, arrested four members of a ransomware gang linked to over $40.5 million in extorted ransoms from at least 28 companies globally. The organization, comprising at least 27 individuals from Ukraine, Kazakhstan, and Russia, targeted sectors including oil and gas, pharmaceuticals, and critical infrastructure. The attackers employed social engineering tactics, posing as IT support staff to gain access to corporate networks. Investigators conducted 66 searches across Ukraine, seizing computers, cash, and other assets. The group is associated with former members of the Conti ransomware gang, which ceased operations in 2022. The total financial impact is still being assessed, with some companies reportedly paying millions in ransom to regain access to their data.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Following this threat?
Track Conti, Scattered Spider and Maxxis International-USA in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What companies were affected?
What methods did the attackers use?
What is the current status of the investigation?
Continue Reading
 Ransomware Groups Exploit PAN-OS Flaw, Target Critical Infrastructure Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. Since its disclosure…
 Cyber Attacks Disrupt European Supermarkets and Airlines A series of cyber-attacks have caused significant disruptions across Europe, targeting supermarket freezers and diverting passenger flights. Supermarkets in countries including Belgium, Sweden, and the UK experienced freezer malfunctions, with temperatures rising to 50°C, resulting in millions of euros in food waste.…