 Pakistantoday.Pk
US Congress Proposes Military Integration with Israel in 2027 NDAA
Article Content

- •The US Congress is proposing unprecedented military integration with Israel via the 2027 NDAA.
- •Section 224 of the NDAA focuses on extensive military collaboration, including AI and cyber technologies.
- •Critics warn of reduced transparency and increased Israeli influence in US defense policy.
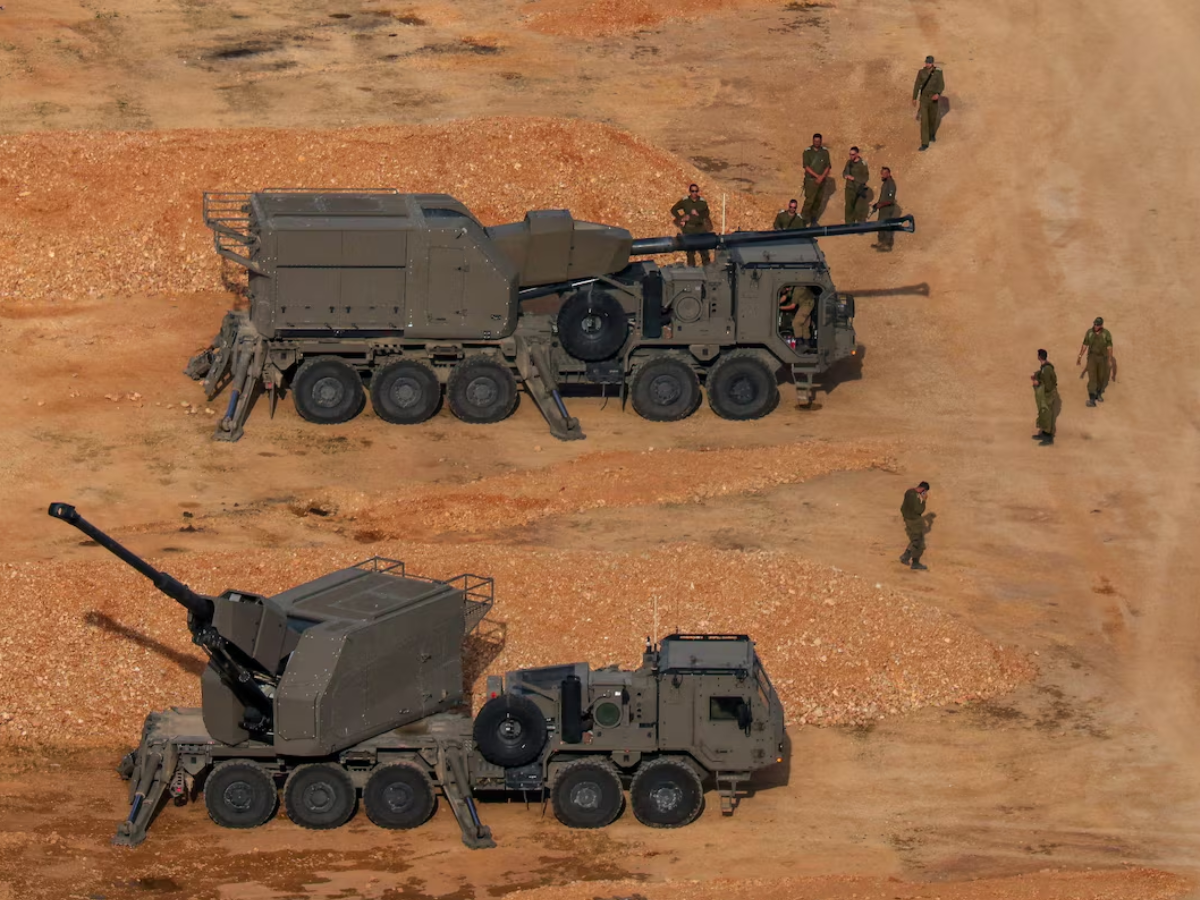
The US Congress is advancing a proposal to integrate American and Israeli military forces through Section 224 of the 2027 National Defence Authorisation Act (NDAA). This initiative, named the United States-Israel Defence Technology Cooperation Initiative, aims to enhance military cooperation significantly. The proposal includes joint research, weapons co-production, and collaboration in advanced technologies such as AI, quantum systems, and cyber capabilities. Critics express concerns about the implications for transparency and the potential for increased Israeli influence in US politics. If enacted, this integration could create a level of military collaboration unmatched by any other US ally. The US has provided Israel with approximately $200 billion in military assistance since 1948, and this new measure could further deepen that relationship. The legislation is currently under consideration in the House of Representatives.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (12)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…