 English.Elpais
U.S. Indicts Raúl Castro Over 1996 Aircraft Shootdown
Article Content

- •The U.S. plans to indict Raúl Castro for the 1996 shootdown of two civilian aircraft.
- •Four American pilots were killed in the incident, escalating U.S.-Cuba tensions.
- •The indictment reflects a potential shift towards accountability for state-sponsored violence.
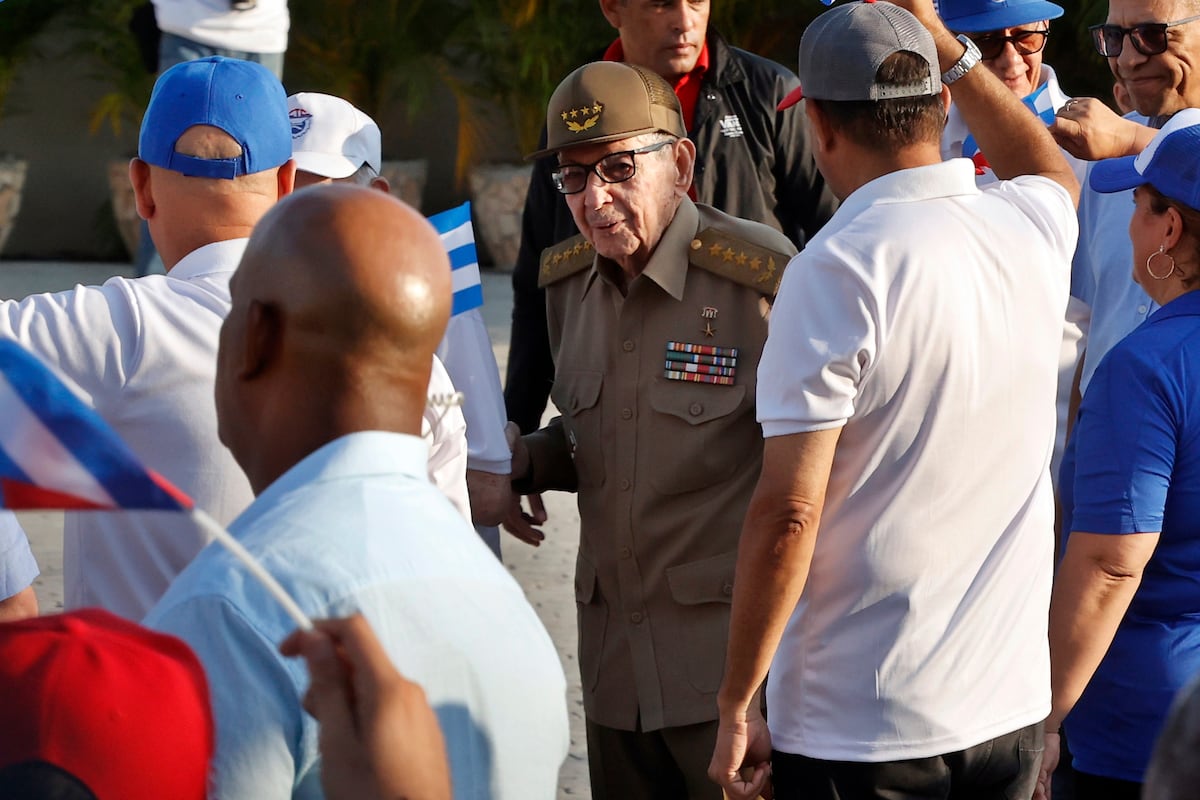
The U.S. government is preparing to indict former Cuban leader Raúl Castro for the 1996 shootdown of two civilian aircraft operated by Brothers to the Rescue, resulting in the deaths of four American pilots. This incident, which occurred on February 24, 1996, involved Cuban MiG fighter jets firing on unarmed Cessna aircraft, leading to international condemnation and heightened tensions between the U.S. and Cuba. The indictment is expected to be formally announced soon, pending grand jury approval. This legal action represents a significant move towards holding former state leaders accountable for actions taken during their tenure, particularly in cases involving civilian casualties. Castro, now 94, remains influential within Cuba's political landscape despite stepping down from leadership roles in recent years. The implications of this indictment could reshape U.S.-Cuba relations and set a precedent for international accountability.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…