 www.defenseone.com
US Military Simulates Ukraine-Style Drone Swarm Attack in Florida
Article Content

- •The US military simulated a Ukraine-style drone swarm attack during Operation Clear Horizon.
- •The exercise revealed critical gaps in US counter-drone capabilities and data integration.
- •Operators were able to control drones from Colorado targeting objectives in Florida.
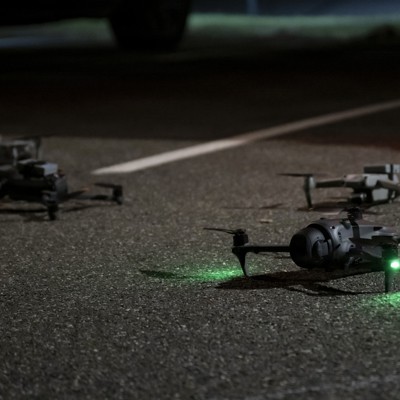
On April 25, 2026, the US military conducted a large-scale simulation of a drone swarm attack at Eglin Air Force Base in Florida, mirroring Ukraine's 2025 'Spiderweb' operation against Russian forces. The exercise, named Operation Clear Horizon, involved US Special Forces executing simulated drone strikes while counter-drone units defended against them. Brig. Gen. Matt Ross highlighted that the drills were informed by recent engagements with Ukrainian forces, focusing on effective unmanned systems. The exercise utilized a variety of drones, including commercial quadcopters and advanced platforms resistant to electronic warfare. Notably, operators in Colorado controlled drones targeting objectives in Florida, marking a first for US military operations. The findings revealed significant gaps in US defenses, emphasizing the need for a unified data integration system and low-cost interceptor drones. The Pentagon has allocated over $600 million to enhance counter-drone technologies following the exercise.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…