 www.nbcnews.com
Trump Administration Suspends Microsoft from Green Card Program for Fraud Allegations
Article Content

- •Microsoft and other tech companies are suspended from a green card program due to fraud allegations.
- •The Trump administration claims Microsoft has abused the permanent labor certification program.
- •Microsoft asserts that most of its H-1B applications were for existing employees, not new hires.
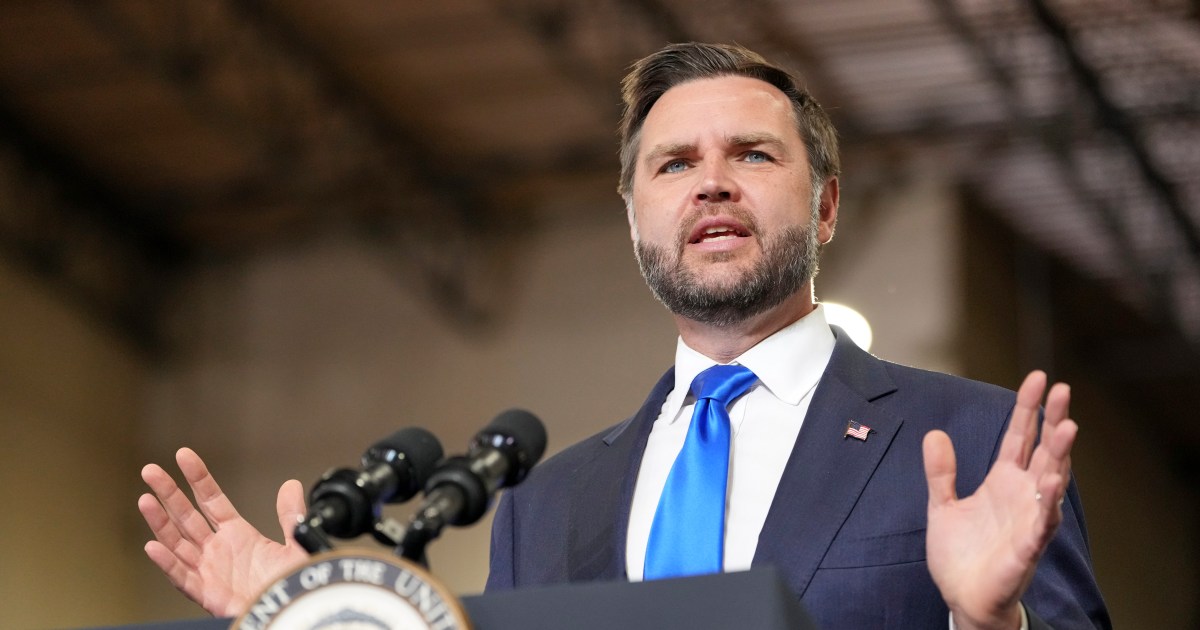
The Trump administration has suspended Microsoft, Adobe, and other tech companies from a program that allows skilled foreign workers to obtain permanent residency in the U.S., citing allegations of fraud. Vice President JD Vance claimed that Microsoft has abused the permanent labor certification program, which is intended for situations where there are insufficient U.S. workers available. The suspension affects several major firms, including Cognizant and Infosys, and prohibits them from submitting new applications for permanent labor certification. Labor Secretary Keith Sonderling indicated that Microsoft and Adobe requested nearly 3 million foreign workers and received over 230,000 H-1B visa approvals. Microsoft responded by stating that most of its H-1B applications were to extend the status of existing employees, not to hire new foreign workers. The administration is also investigating universities for alleged misuse of visa programs. This announcement coincided with a scheduled event where President Trump was to award Microsoft CEO Satya Nadella the National Medal of Technology and Innovation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Adobe in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What companies are affected by the suspension?
What are the allegations against Microsoft?
How did Microsoft respond to the allegations?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…