 Bitcoinmagazine
U.S. to Seize $1 Billion in Iranian Crypto Amid Sanctions
Article Content

- •U.S. plans to seize $1 billion in Iranian cryptocurrency as part of sanctions enforcement.
- •The specific cryptocurrencies targeted in the seizure have not been disclosed.
- •Iran has been using crypto to evade U.S. sanctions, complicating enforcement efforts.
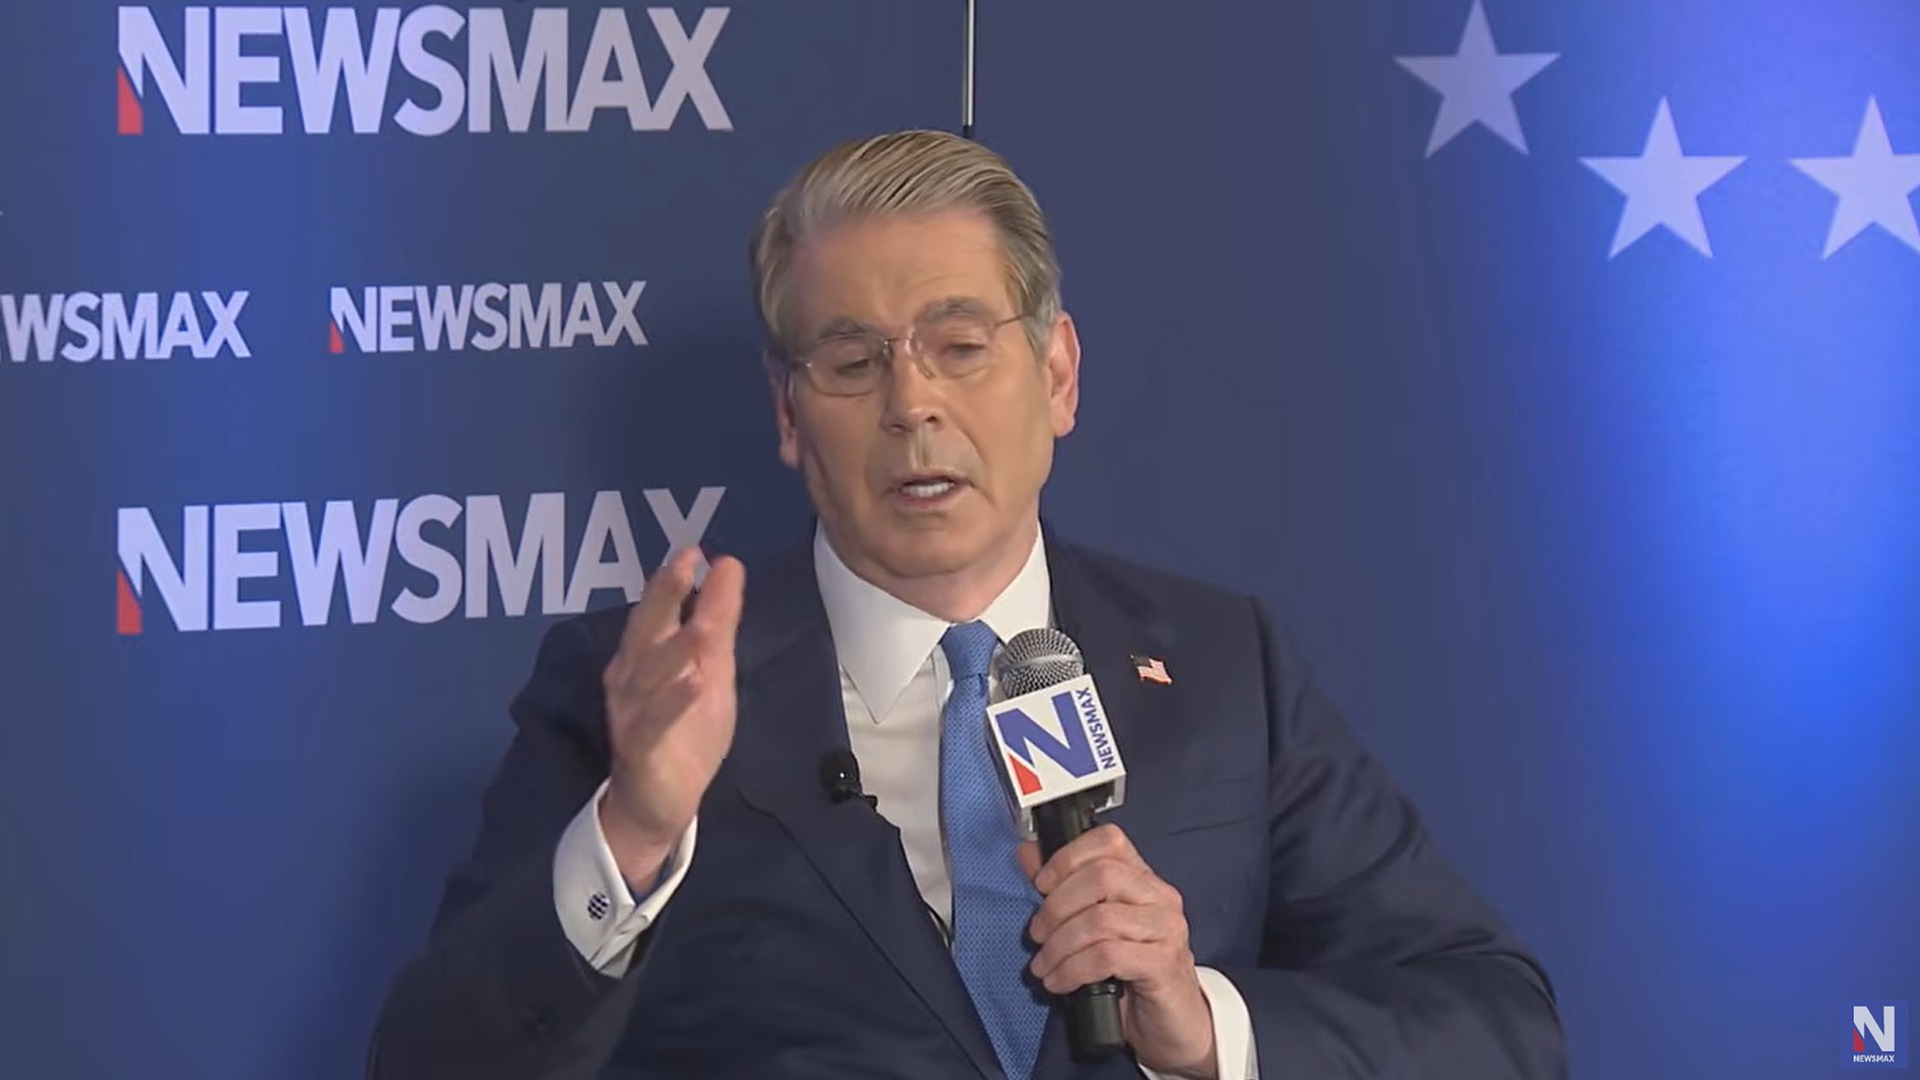
The U.S. Treasury Secretary Scott Bessent announced plans to seize $1 billion in cryptocurrency from Iran, targeting assets used to evade sanctions. This action is part of a broader strategy to isolate Iran economically, which includes previous efforts to target crypto wallets linked to the Iranian regime. The specific cryptocurrencies involved in the seizure have not been disclosed, but Bessent noted that the U.S. is aware of the locations of these assets. The announcement follows a recent pledge from former President Trump to maintain pressure on Iran, which has reportedly been using cryptocurrencies like bitcoin to circumvent U.S. sanctions. The implications of this seizure could affect the broader cryptocurrency market, particularly if it involves widely-used stablecoins. The situation remains fluid as the U.S. government continues its campaign against Iran's financial networks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What cryptocurrencies are being seized?
How does this affect the crypto market?
What is Iran's strategy with crypto?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…