 claroty.com
Vulnerabilities Found in Danfoss Refrigeration Controllers
Article Content

- •Multiple vulnerabilities found in Danfoss AK-SM 800A controllers.
- •Vulnerabilities include remote code execution and command injection flaws.
- •Danfoss has released a firmware update to address these issues.
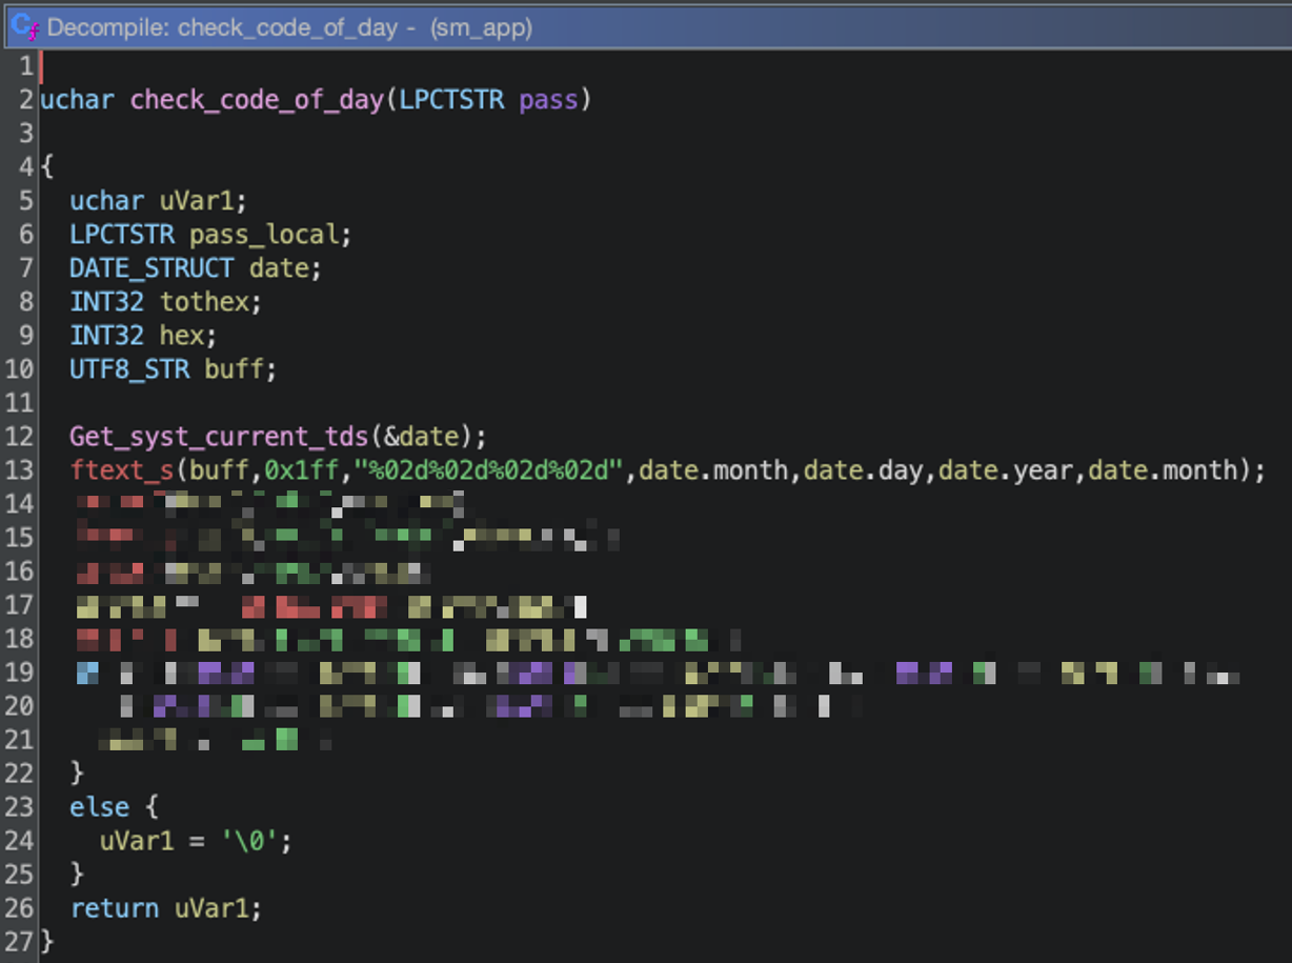
Team82 identified multiple vulnerabilities in the Danfoss AK-SM 800A refrigeration controllers, which are widely used in supermarkets and cold-storage facilities. The vulnerabilities include a hidden 'code-of-the-day' authentication mechanism, a command-injection flaw leading to remote code execution, and an issue allowing arbitrary Nginx configuration directive injection. Thousands of these devices were found to have publicly accessible management interfaces. Danfoss has since addressed these vulnerabilities in a new firmware version. The vulnerabilities were disclosed on October 12, 2026, and are significant due to the potential operational impact on refrigeration management systems. The research highlights the risks associated with undocumented functionalities and insecure command constructions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Danfoss and CVE-2025-41450 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What vulnerabilities were found?
How many devices are affected?
What should be done now?
Continue Reading
 Cyber-Attack Spoils Food in Major French Supermarkets On October 12, 2026, a cyber-attack targeted refrigeration systems in several French supermarkets, including Coopérative U and Intermarché. The attack exploited outdated software from Danish provider Danfoss, allowing hackers to remotely trigger defrost cycles, raising temperatures to 50°C. Initial reports indicate…
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…