 wabetainfo.com
WhatsApp Blocks Logins on Outdated Android and iOS Devices
Article Content

- •WhatsApp blocks logins for users on outdated Android and iOS versions.
- •The update is applied server-side and does not require a new app version.
- •Users must update their operating system to regain access to WhatsApp.
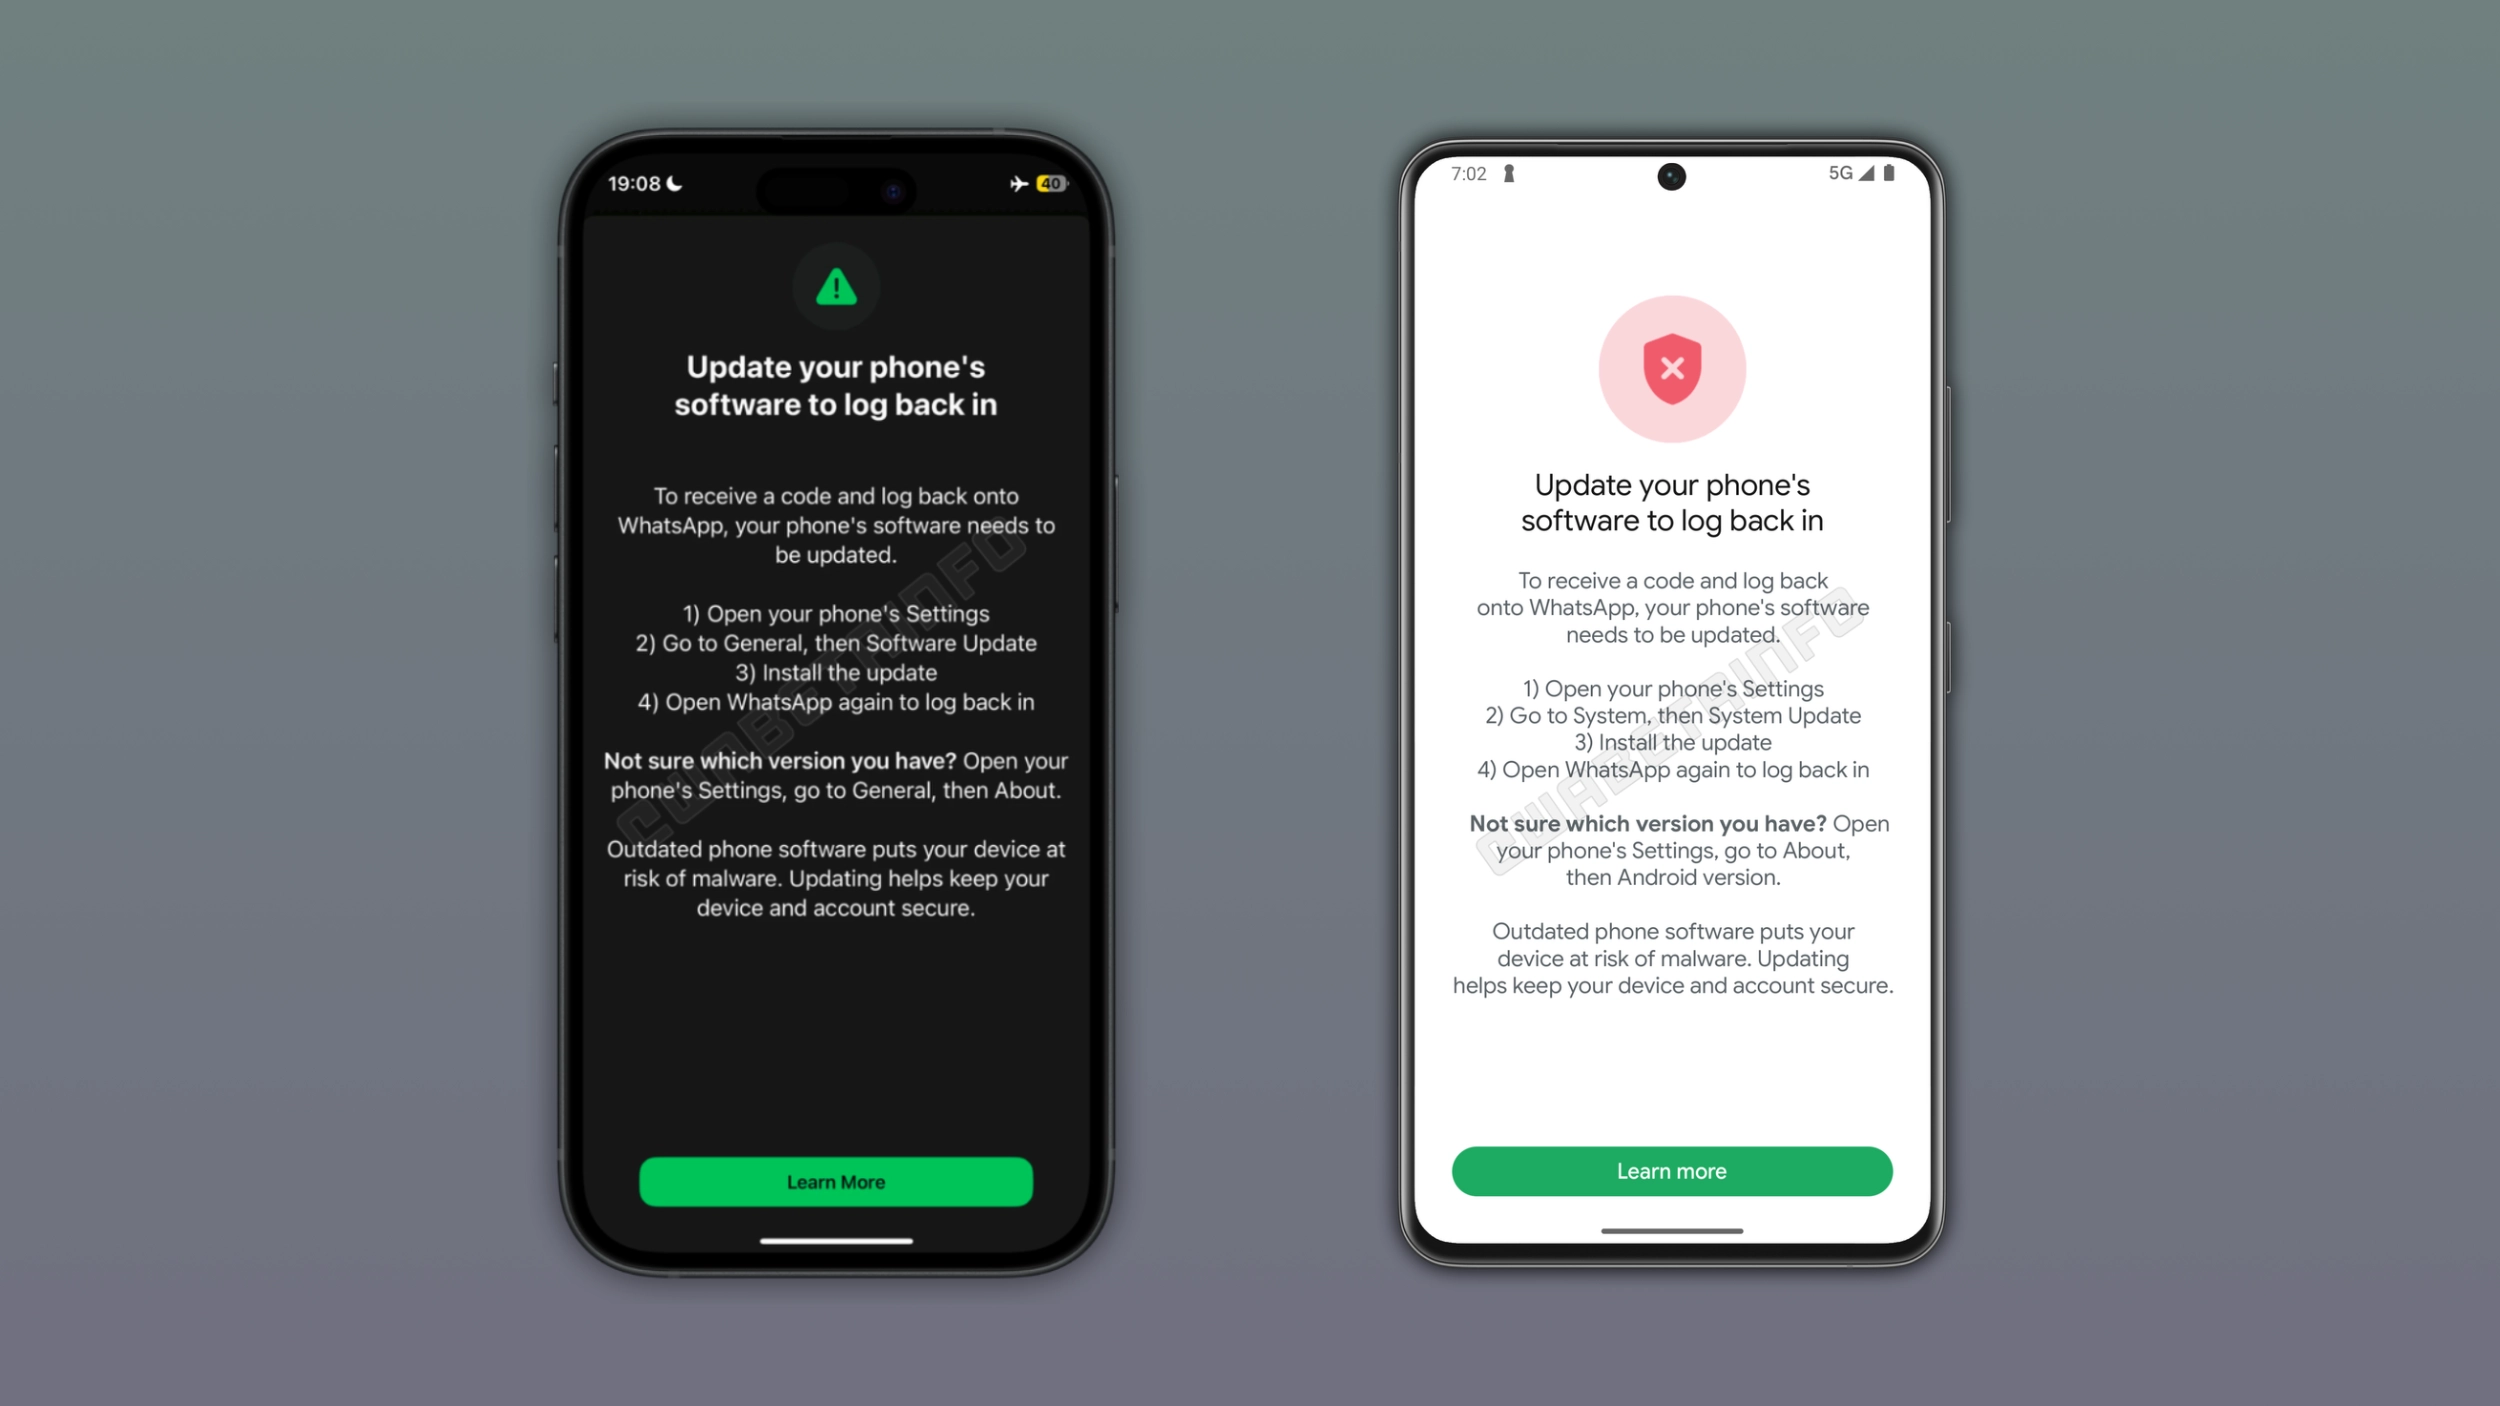
WhatsApp has implemented a new security measure that blocks users from logging in if their devices run outdated versions of Android or iOS. This server-side update requires users to update their operating system to regain access. The change is aimed at enhancing security by ensuring that users operate on platforms that receive important security updates. Affected users will see a dedicated screen during login instructing them to update their OS. The specific versions of Android and iOS that trigger this restriction have not been disclosed. This measure is part of WhatsApp's broader strategy to protect user accounts from potential vulnerabilities associated with outdated software. The update does not require users to download a new version of WhatsApp to experience the login block. There is currently no workaround for affected users; updating the OS is mandatory to access the app again.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
Which operating systems are affected?
Is there a workaround for affected users?
What is the purpose of this update?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…