 Modernghana
Russian Nationals Convicted in Angola for Espionage and Terrorism
Article Content

- •Two Russian nationals sentenced for espionage and terrorism in Angola.
- •Charges included criminal association and illegal currency retention, linked to election meddling.
- •Prosecutors allege over $24,000 was paid to local journalists for disinformation campaigns.
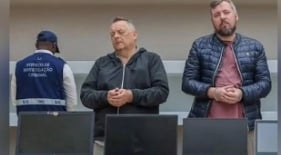
In Angola, two Russian nationals, Igor Ratchin and Lev Lakshtanov, were sentenced to 11 and 8 years in prison for charges including espionage and terrorism. They were arrested in August 2025 following protests that escalated into riots, resulting in at least 22 deaths. The court found them guilty of criminal association and illegal currency retention, among other charges. Prosecutors linked them to a broader Russian strategy to influence Angolan politics ahead of the 2027 elections, alleging they paid over $24,000 to local journalists for disinformation. The trial also included two Angolan co-defendants, with one receiving a suspended sentence and the other acquitted. Both Russian defendants denied the charges, claiming their activities were cultural and commercial. Appeals have been filed by both the prosecution and the defense, and the defendants remain in detention pending the outcome.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Wagner in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…