 links.erelease.com.au
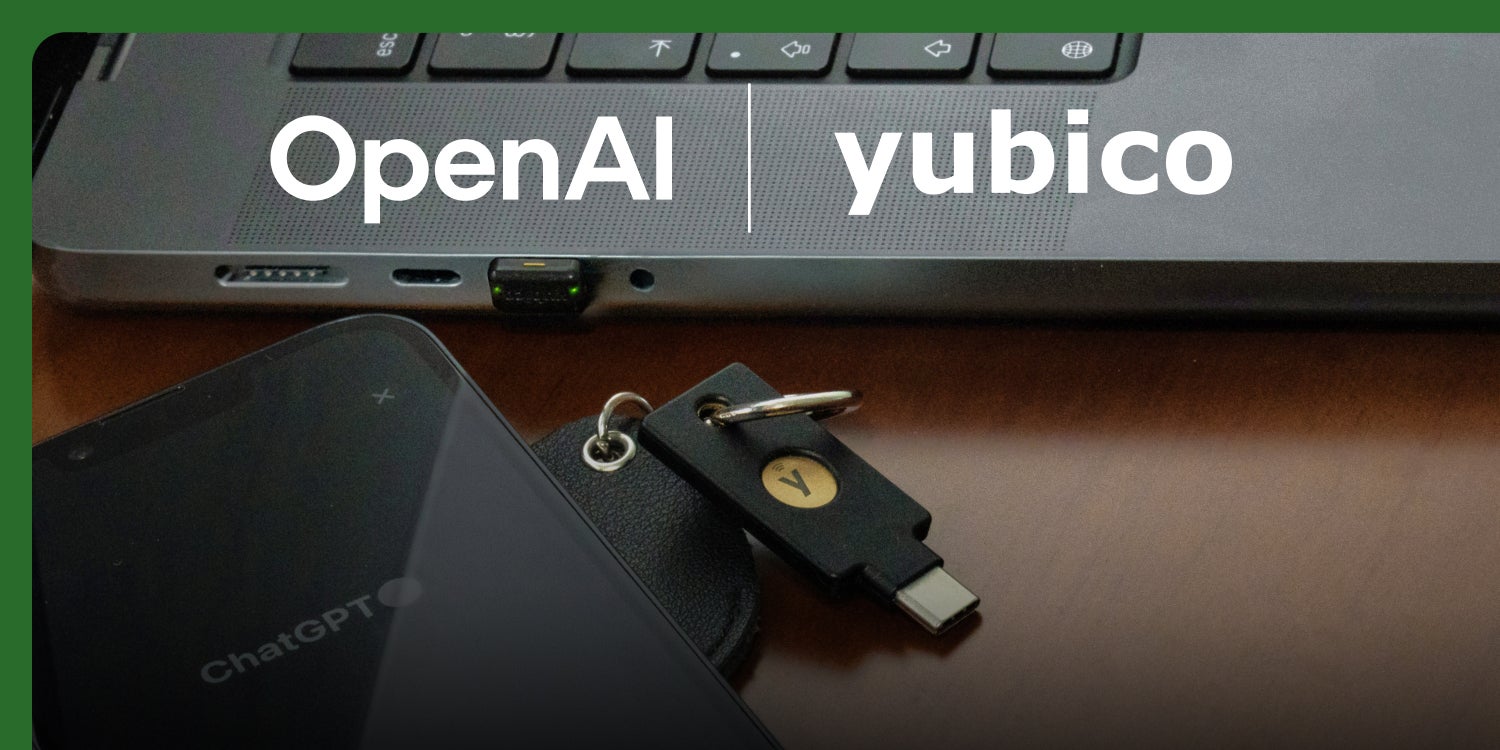
Yubico and OpenAI Enhance Cybersecurity with Hardware-Backed Passkeys
Article Content

- •Yubico's partnership with OpenAI expands to Australia and nine other countries.
- •OpenAI's Advanced Account Security program requires hardware-backed passkeys for TAC members.
- •The initiative aims to reduce phishing risks and enhance account security for AI users.
Yubico has expanded its partnership with OpenAI to include Australia and nine other countries, launching a custom two-pack YubiKey bundle as part of OpenAI's Advanced Account Security program. This program, which went live on September 1, 2026, mandates the use of hardware-backed passkeys for members of OpenAI's Trusted Access for Cyber (TAC) program to enhance account security and reduce phishing risks. The YubiKey bundle includes the YubiKey C NFC for mobile authentication and the YubiKey C Nano for laptop use. By requiring hardware-backed passkeys, OpenAI aims to mitigate credential theft and account takeover risks associated with traditional authentication methods. The initiative reflects a broader industry shift towards stronger authentication mechanisms as AI technologies become more prevalent in sensitive applications. The partnership is expected to significantly bolster security for OpenAI users, including those using ChatGPT and Codex.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track OpenAI in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…