Summary
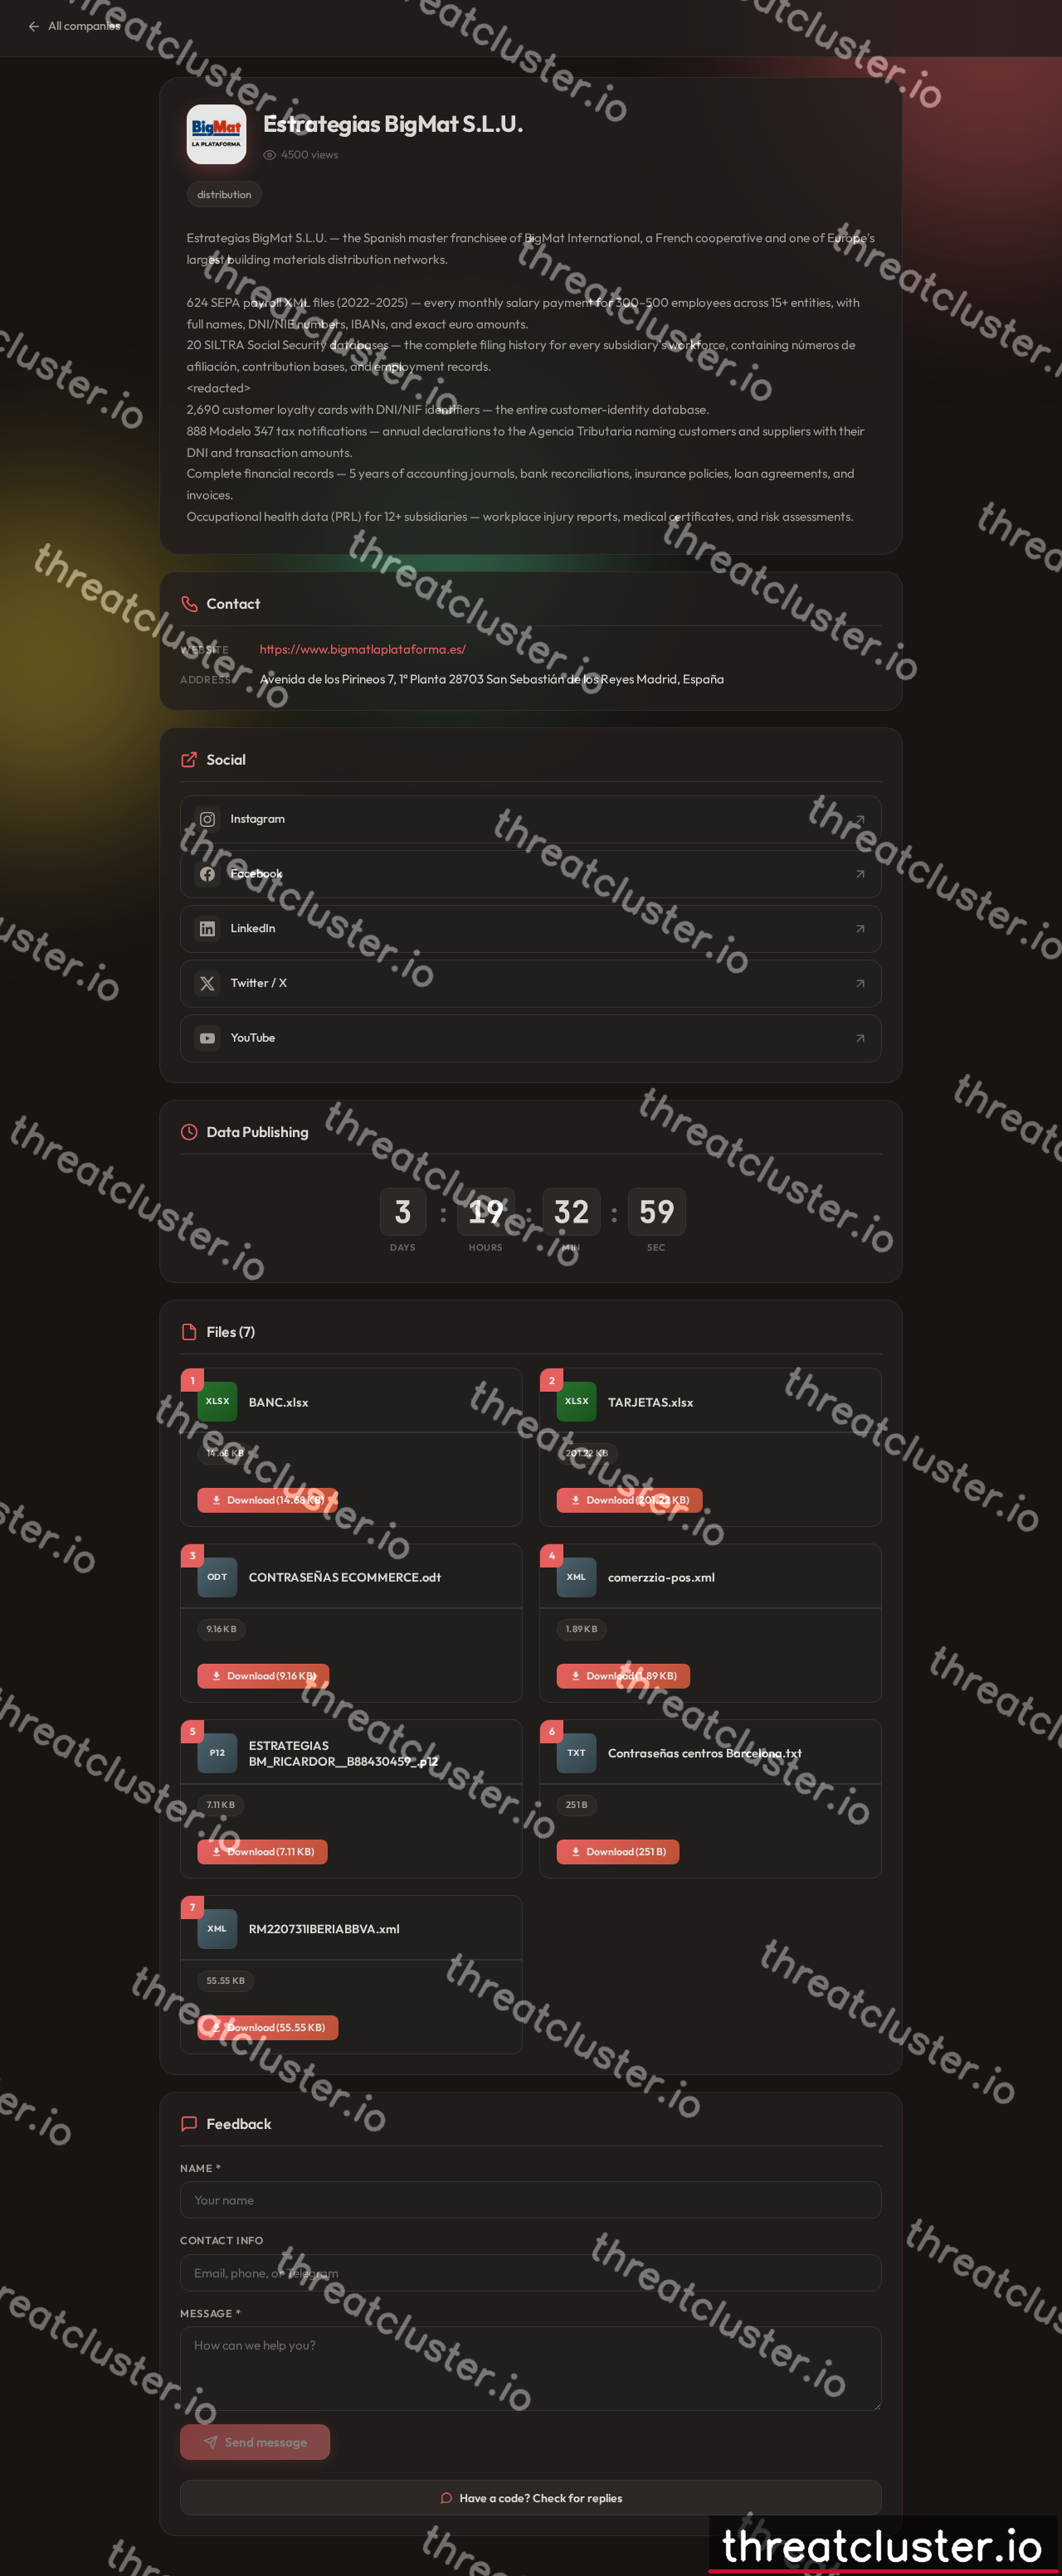
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshotAurora claims Estrategias BigMat S.L.U. exposed 624 SEPA payroll XML files (2022–2025) covering 300–500 employees across 15+ entities, plus 2,690 customer loyalty cards with DNI/NIF identifiers and 888 Modelo 347 tax notifications. They also claim complete financial records for five years and occupational health data for 12+ subsidiaries. The leak post is listed on the group’s site and shows a data-publishing countdown of 6 days remaining.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Employees
- 0
- Domains
- https://www.bigmatlaplataforma.es/
What was taken
Estrategias BigMat S.L.U. — the Spanish master franchisee of BigMat International, a French cooperative and one of Europe's largest building materials distribution networks.
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- redacted
- <redacted>
- Data Publishing
- 6 days : 23 hours : 33 min : 34 sec
Leak-site images (2)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.