Summary
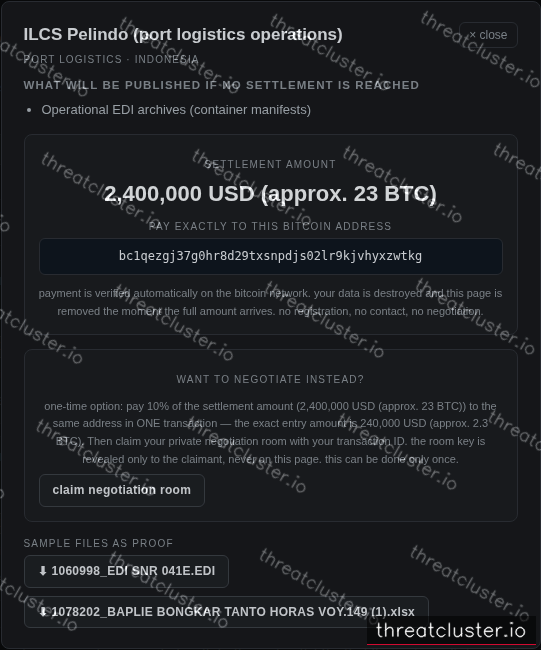
Written by ThreatClusterfrom victim profile, leak postn0n claims to hold a complete port logistics archive belonging to ILCS Pelindo (port logistics operations) in Indonesia, amounting to 2.4 GB across 108 records and files, including EDI container manifest archives and operational records. The leak page shows a countdown publication status, with the full archive set to become downloadable by anyone on the publication date. It states that if a settlement arrives before publication, every copy is destroyed and nothing becomes public.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Domains
- ilcs.co.id
What was taken
What we hold and what will be published: We hold a complete port logistics archive belonging to this organization: 2.4 GB of data covering 108 individual records and files. This includes EDI container manifest archives, together with operational records. The material spans the organization's recent operating history and contains commercially sensitive information whose publication would expose ongoing business relationships, customer flows and internal processes to competitors, customers and regulators alike. On the publication date shown on this page, the full archive becomes downloadable by anyone: customers, partners, press and competitors. Shipping and port operations run on trust and confidentiality; a public archive of this scale does not go unnoticed. If the settlement arrives before publication, every copy is destroyed and nothing ever becomes public.
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.