Summary
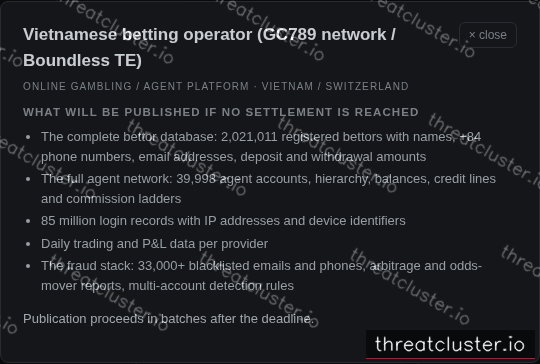
Written by ThreatClusterfrom victim profile, leak postThe leak post from the group n0n claims to expose data from a Vietnamese online gambling/agent platform operator, including a bettor database of 2,021,011 registered bettors with names, +84 phone numbers, email addresses and deposit/withdrawal amounts. It also claims to include the full agent network (39,998 agent accounts) with hierarchy, balances, credit lines and commission ladders, 85 million login records with IP addresses and device identifiers, daily trading and P&L data per provider, and a fraud stack including 33,000+ blacklisted emails and phones, arbitrage and odds-mover reports, and multi-account detection rules. Publication is described as proceeding in batches after the deadline, and the leak post is published. Victim profile on the leak page lists the sector as online gambling/agent platform and the country as Vietnam.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
What was taken
What will be published if no settlement is reached The complete bettor database: 2,021,011 registered bettors with names, +84 phone numbers, email addresses, deposit and withdrawal amounts The full agent network: 39,998 agent accounts, hierarchy, balances, credit lines and commission ladders 85 million login records with IP addresses and device identifiers Daily trading and P&L data per provider The fraud stack: 33,000+ blacklisted emails and phones, arbitrage and odds-mover reports, multi-account detection rules Publication proceeds in batches after the deadline.
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.