Frequency
3
occurrences
First Seen
September 27, 2026
Last Seen
September 27, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
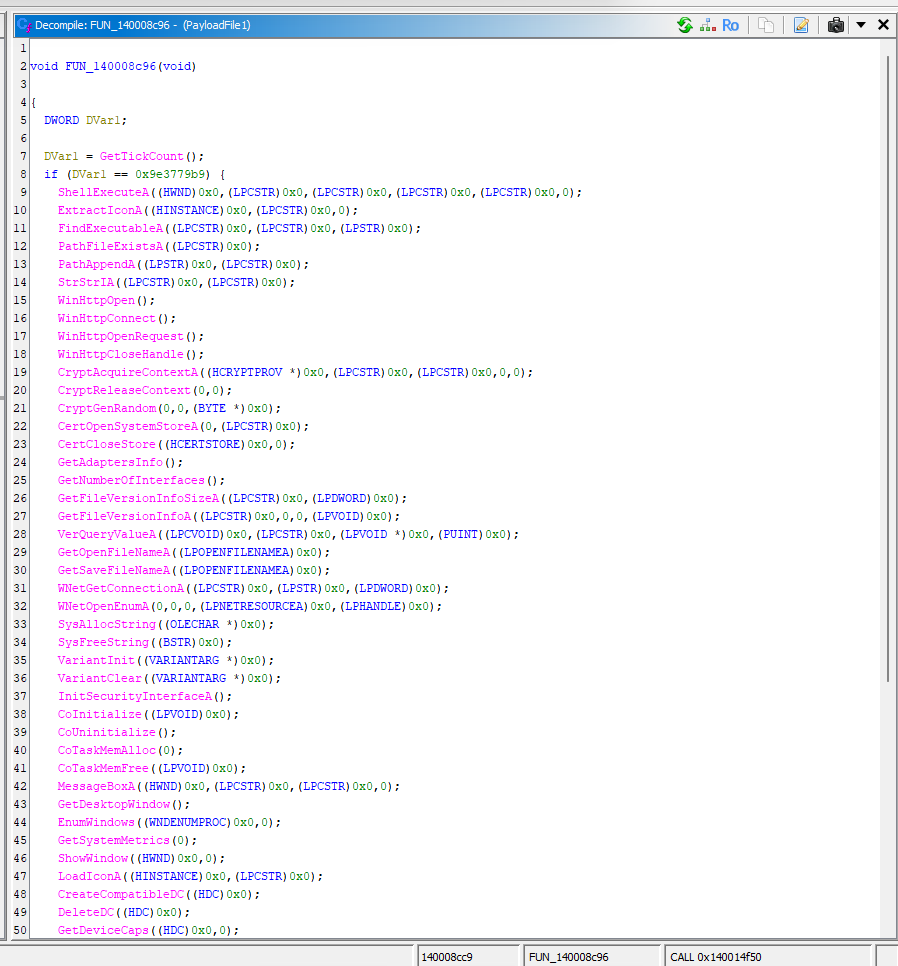
The Lunex Malware-as-a-Service platform has been identified as targeting Ukrainian-speaking users through a sophisticated four-stage attack chain. The attack begins with a fake CAPTCHA page and employs a Bring Your Own Vulnerable Driver (BYOVD) technique to disable security monitoring before deployi...
Public Exploits
Checking GitHub for proof-of-concept code…