Frequency
2
occurrences
First Seen
September 24, 2026
Last Seen
September 25, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
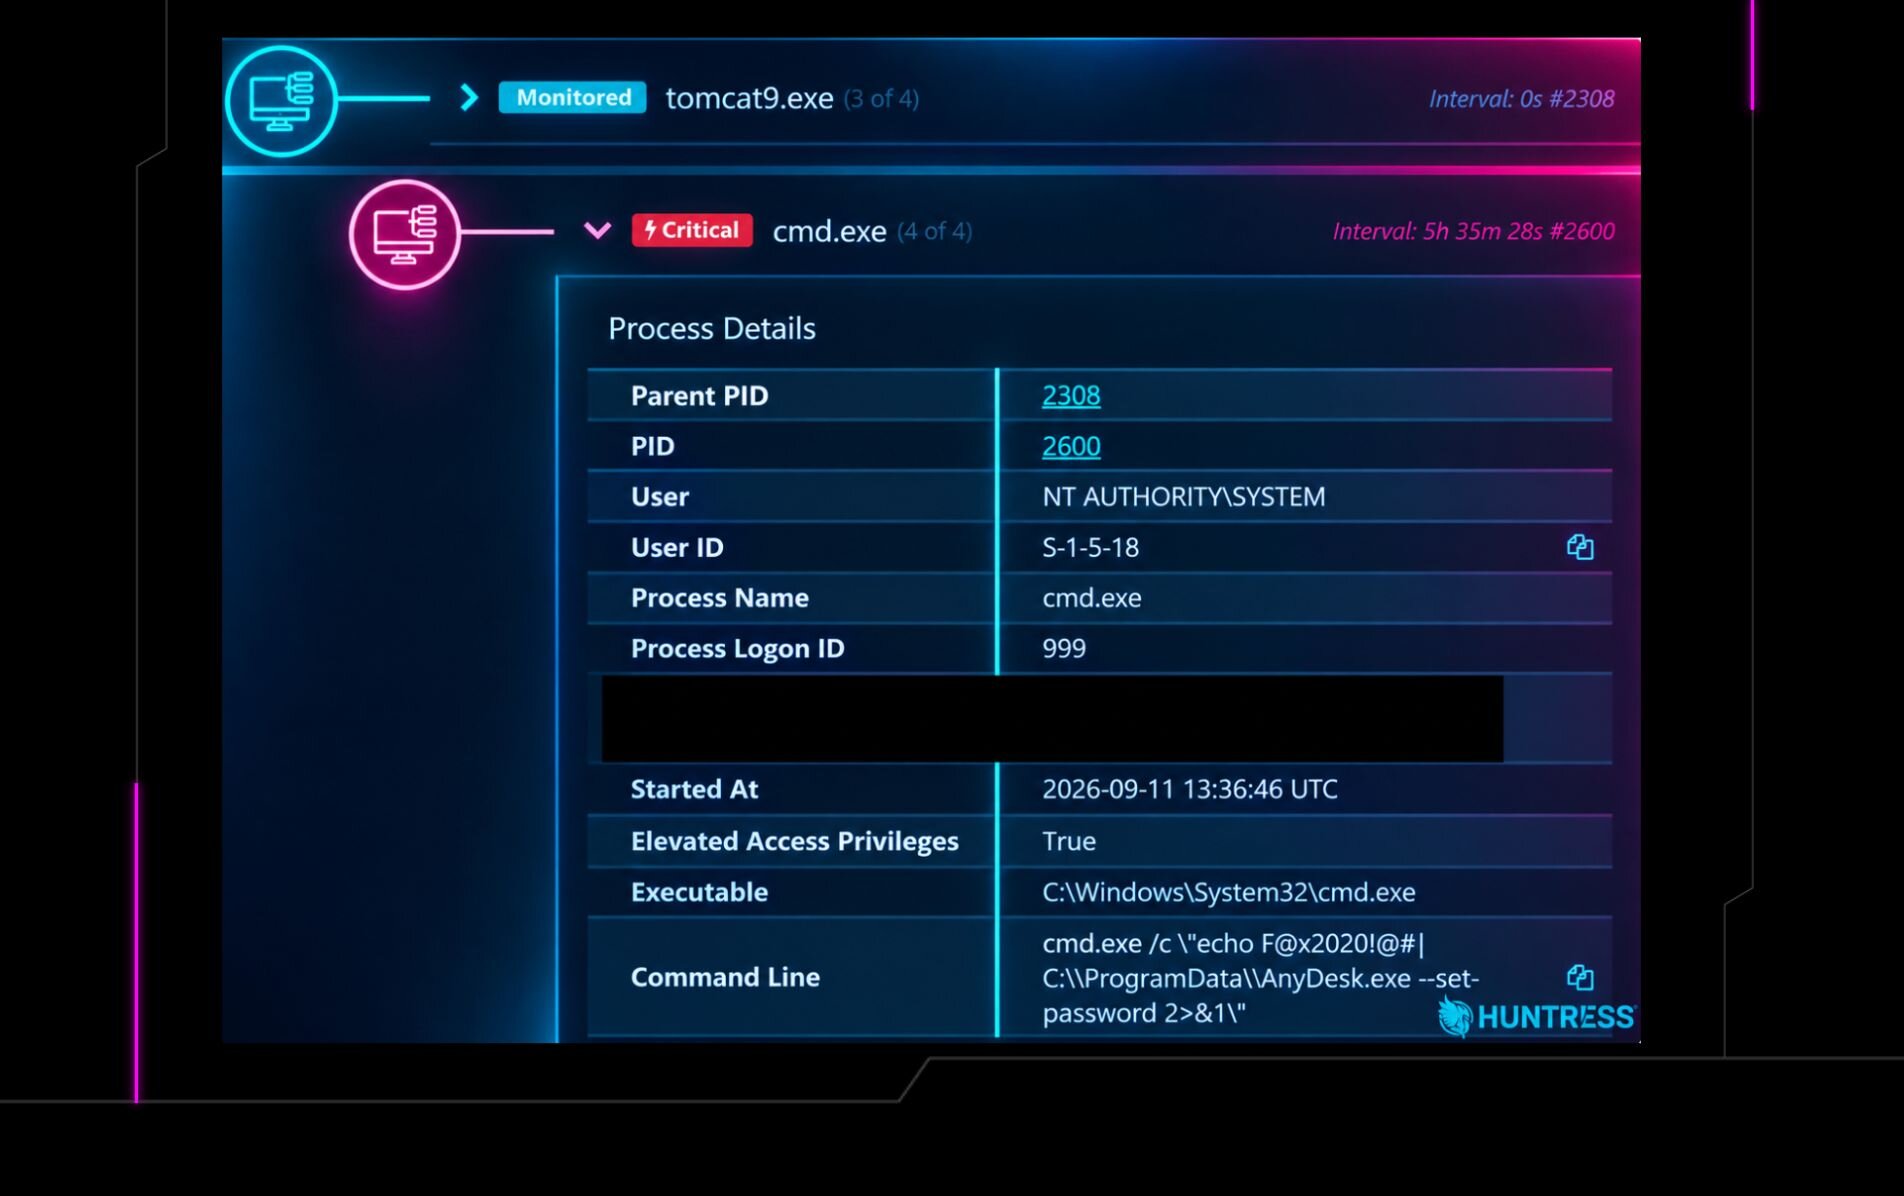
In early September 2026, a threat actor exploited CVE-2025-4632, a vulnerability in Samsung MagicINFO, to compile a cryptominer directly on a victim's endpoint. The attack began with the installation of a rogue AnyDesk instance after multiple failed attempts, followed by creating a new local admin a...
Public Exploits
Checking GitHub for proof-of-concept code…