Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
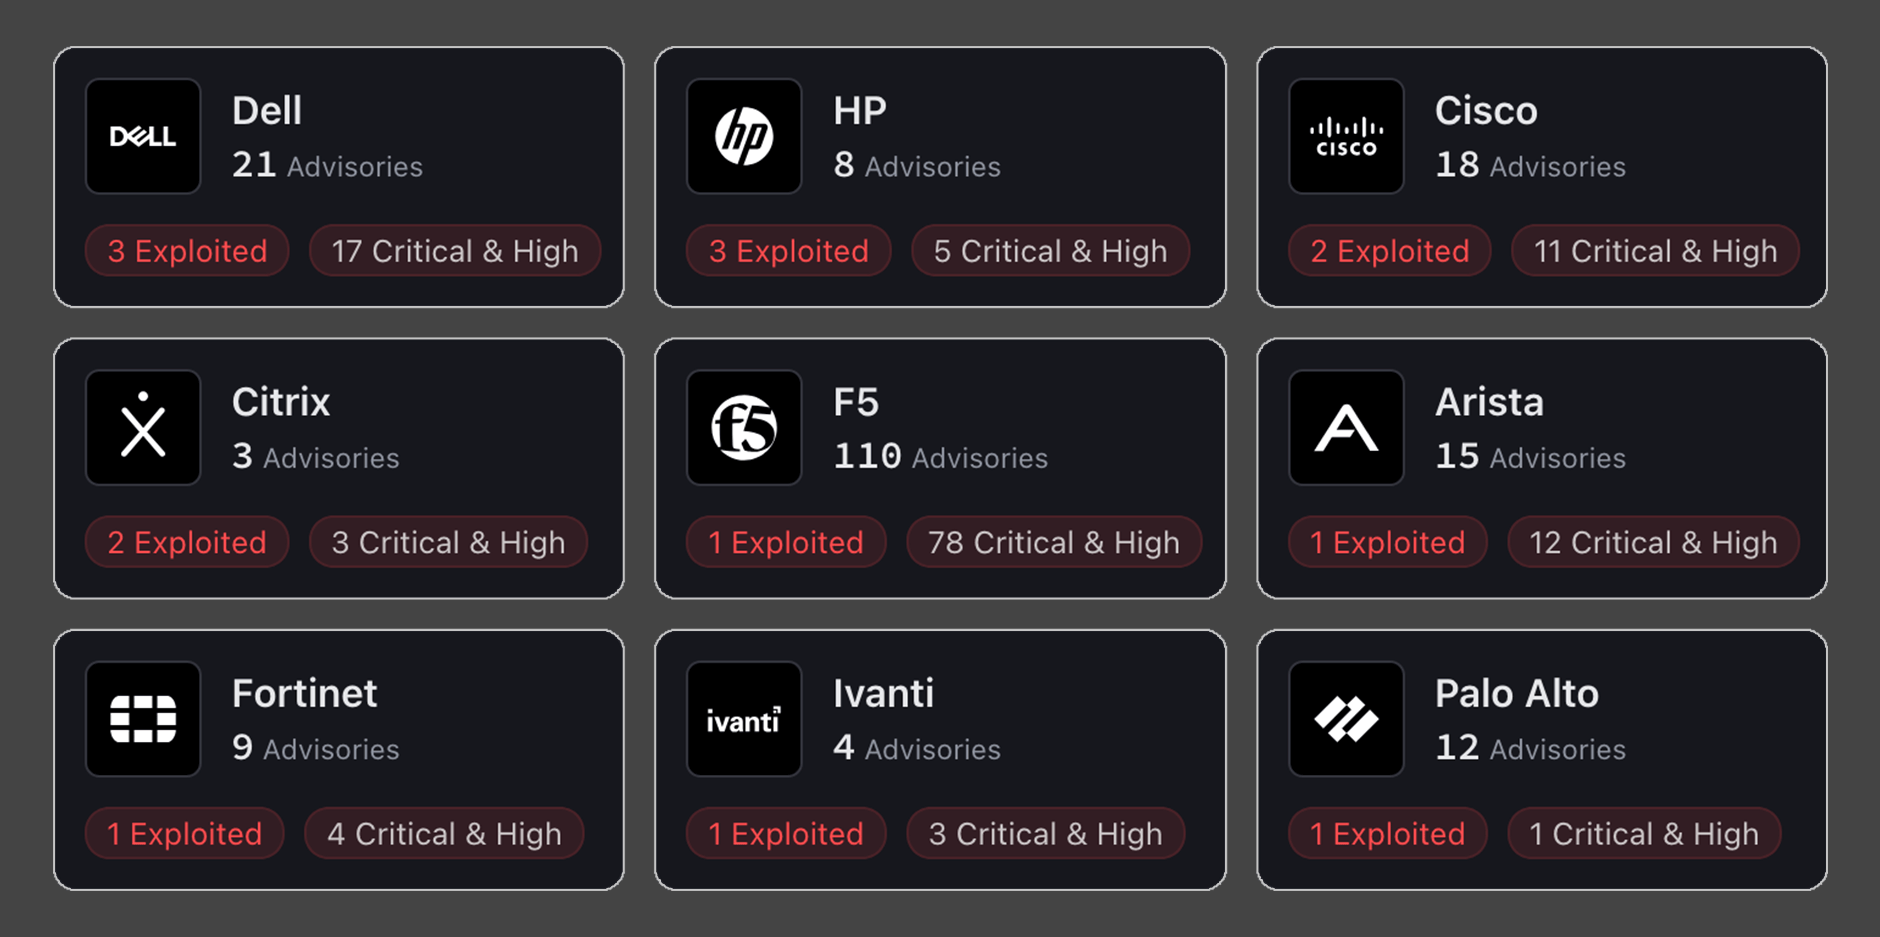
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, with a CVSS score of 9.8. This path traversal vulnerability allows unauthenticated attackers to write arbitrary files on affected systems via crafted HTTP or HTTPS requests. The flaw has been confirmed to be ac...
A critical vulnerability, CVE-2026-61500, in Rejetto HTTP File Server (HFS) allows unauthenticated remote code execution (RCE) due to a weak pseudo-random number generator (PRNG) used for session keys. Discovered by Anthropic's Mythos AI, the flaw affects HFS versions 3.0.0 to 3.2.0, with a CVSS sco...
Arista Networks has patched a critical SQL injection vulnerability, CVE-2026-114625, in its VeloCloud Orchestrator (VCO) that allows authenticated users to escalate privileges to superuser status. The flaw, rated 9.9 on the CVSS scale, has been actively exploited in the wild, affecting on-premises d...
CVE-2026-0768, an unauthenticated remote code execution vulnerability in Langflow, is being, allowing attackers to execute arbitrary code with root privileges. As of October 6, 2026, VulnCheck reported over 360 exploitation attempts, primarily targeting environment variables such as AWS secrets and...