Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Chinese-nexus threat actors utilized ARTEX, an open-source penetration-testing framework, to exploit stolen large language model API keys for credential theft. Amazon Threat Intelligence reported that these operations were detected between October 3 and November 5, 2026, through their MadPot decoy n...
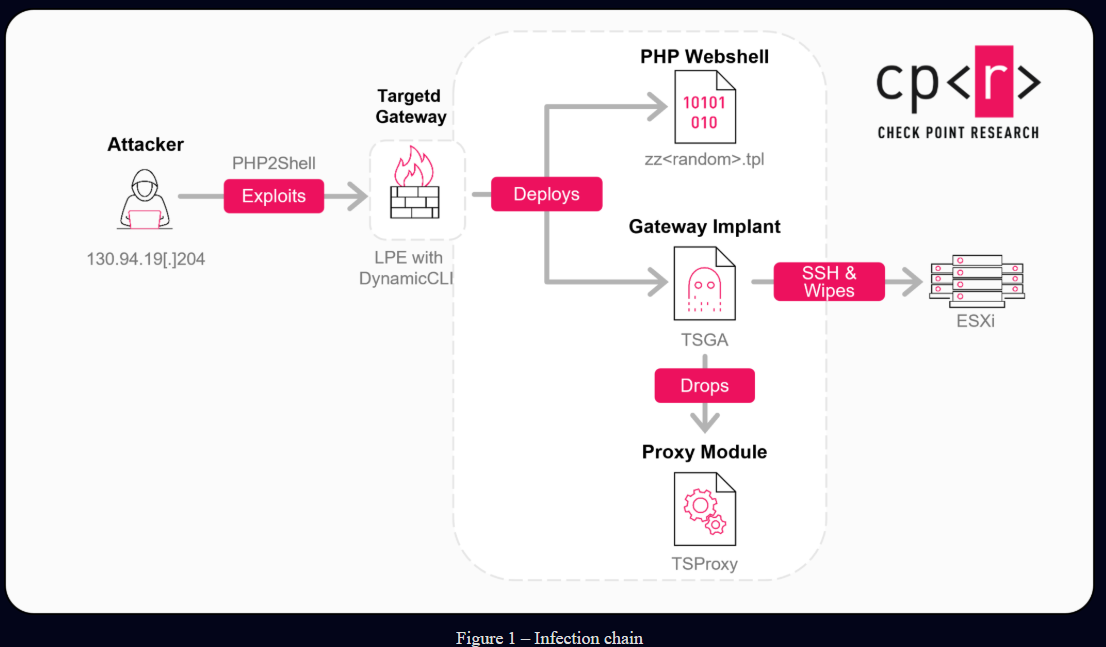
Beginning on October 30, 2026, attackers exploited unpatched vulnerabilities in Check Point Security Gateways, specifically the PHP2Shell flaws (CVE-2026-109618 and CVE-2026-109619) and a local privilege escalation vulnerability (CVE-2026-123039). The initial wave targeted Israeli organizations, lea...
Check Point Software has issued emergency hotfixes for CVE-2026-123039, a high-severity local privilege escalation vulnerability affecting Gaia OS. The flaw allows authenticated local users to execute arbitrary commands as root via a world-writable socket (/tmp/dynamic_socket) used by the DynamicCLI...