Frequency
9
occurrences
First Seen
November 9, 2026
Last Seen
November 10, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
CISA has warned of active exploitation of a critical vulnerability in IBM Aspera Faspex, tracked as CVE-2026-123218, which allows authenticated users to bypass authorization and gain full administrative privileges. This flaw, rated CVSS 9.8, affects all Faspex 5 versions from 5.0.0 to 5.0.19. IBM re...
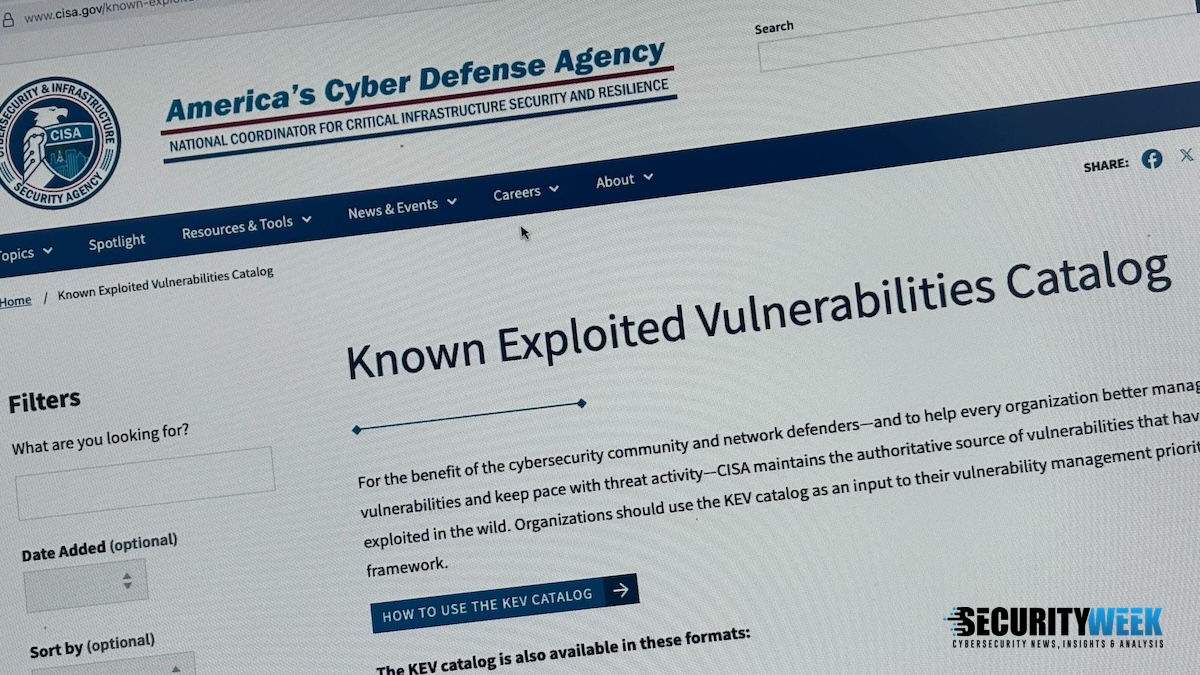
On November 9, 2026, CISA added four actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, giving federal agencies until November 12 to remediate. The vulnerabilities include CVE-2026-102895 in GPUStack, CVE-2026-116779 in FreeSWITCH, CVE-2026-123158 in OpenSSH, an...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (2)

Related Articles (9)


1 / 2