Frequency
3
occurrences
First Seen
November 12, 2026
Last Seen
November 12, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
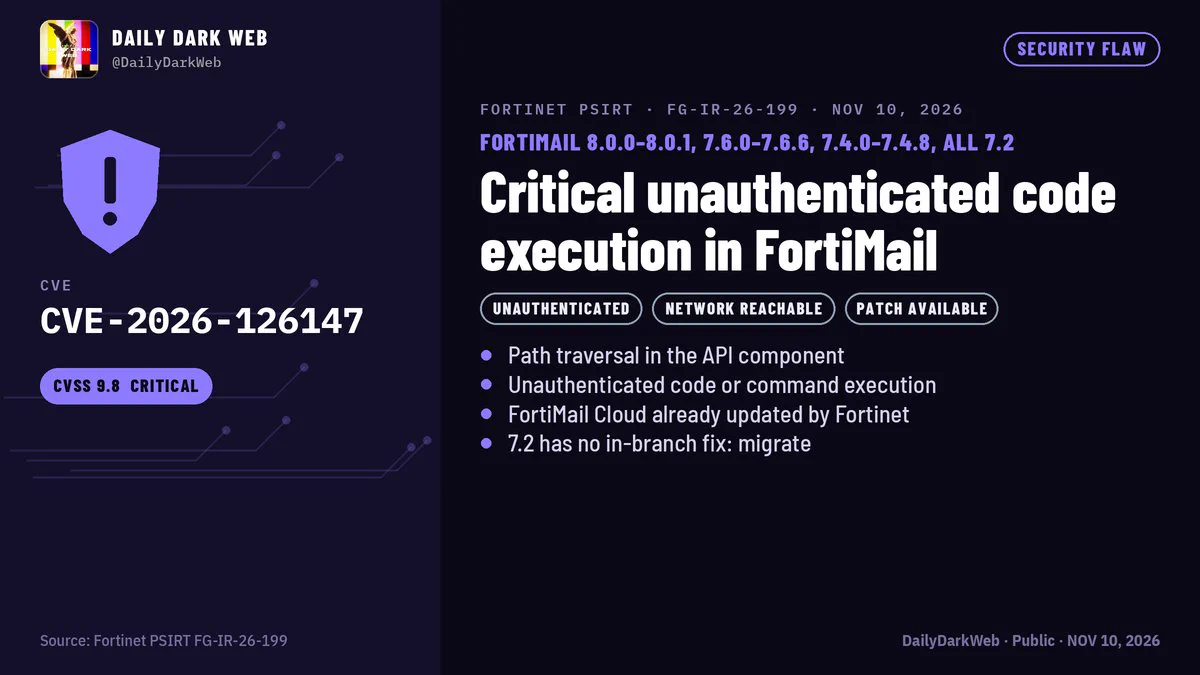
Fortinet disclosed a vulnerability, CVE-2026-126147, affecting FortiMail's management interface, which allows unauthenticated attackers to execute arbitrary code. The flaw, rated CVSS 9.8, is present in FortiMail versions 8.0.0 to 8.0.1, 7.6.0 to 7.6.6, 7.4.0 to 7.4.8, and all versions of 7.2. Forti...
On November 10, 2026, Fortinet disclosed 89 new security advisories addressing nearly 100 vulnerabilities across its product line, including FortiOS, FortiManager, and FortiAnalyzer. Among these, 17 vulnerabilities are classified as critical, with several allowing for arbitrary code execution. The v...
Public Exploits
Checking GitHub for proof-of-concept code…