Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
On March 10, 2026, Microsoft published details about an elevation of privilege vulnerability in Microsoft SQL Server, tracked as CVE-2026-21262. This vulnerability allows attackers to gain higher privileges within the system, potentially leading to unauthorized access and control. The vulnerability...
CVE-2026-20841, a critical vulnerability with a CVSS score of 9.8, affects Windows Remote Procedure Call (RPC) and allows unauthenticated remote code execution. Additionally, a related issue in Windows Notepad, with a CVSS score of 8.8, enables remote code execution via malicious Markdown files. Bot...
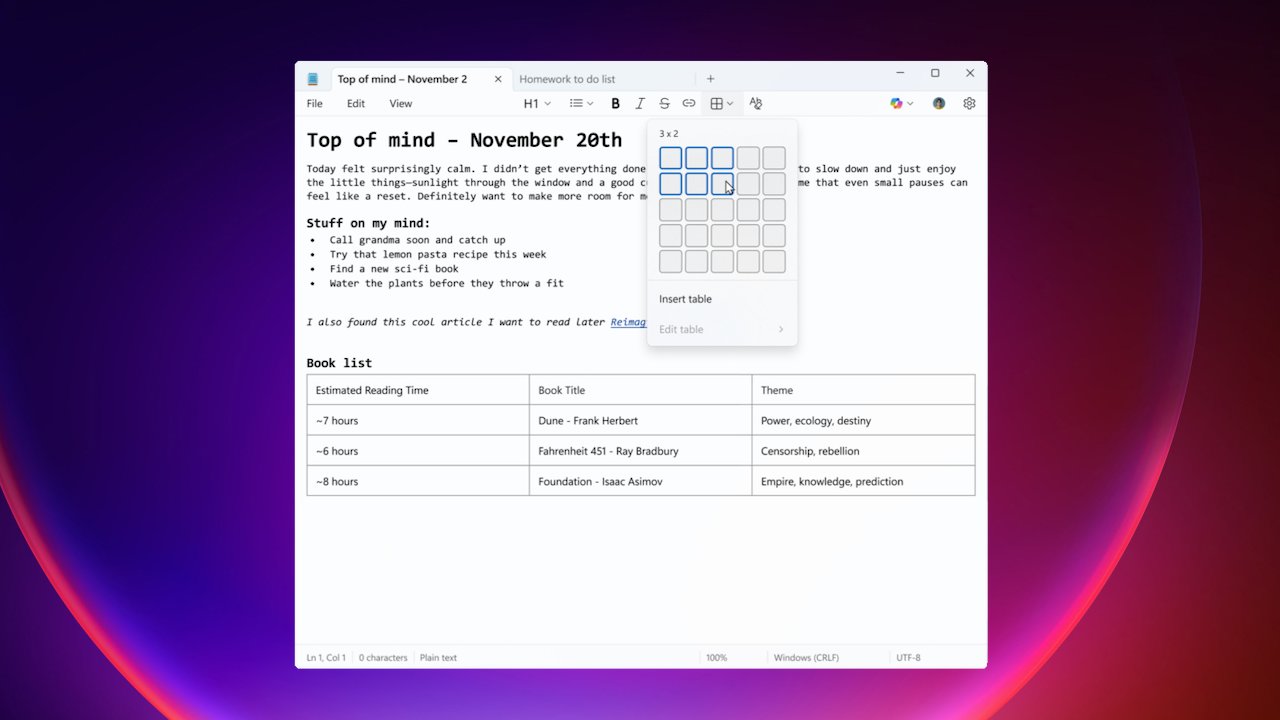
Researchers have discovered a vulnerability in Notepad's newly added Markdown support that can be exploited for remote code execution (RCE). This flaw, tracked as CVE-2026-20841 with a severity score of 8.8, was addressed in Microsoft's latest Patch Tuesday updates. The exploitation requires social...
On February 10, 2026, Adobe and Microsoft released security patches addressing numerous vulnerabilities, including 36 CVEs published on the same day. Notably, three CVEs (CVE-2026-21510, CVE-2026-21514, and CVE-2026-21519) were added to the CISA Known Exploited Vulnerabilities (KEV) list due to acti...