Frequency
5
occurrences
First Seen
June 8, 2026
Last Seen
September 7, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
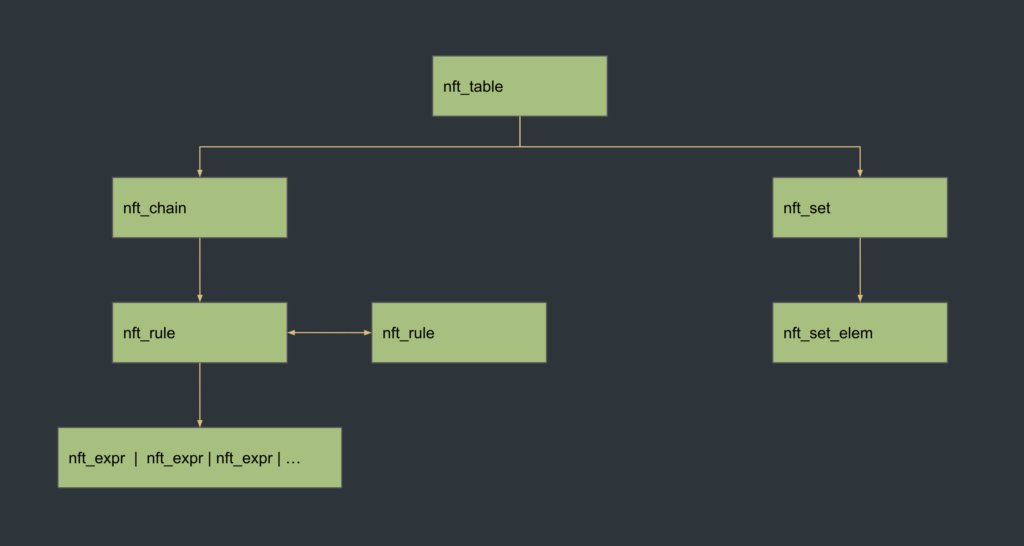
A use-after-free vulnerability in the Linux kernel's nftables subsystem, tracked as CVE-2026-23111, allows local attackers to escalate privileges to root. Discovered in early 2025, the flaw was patched on February 5, 2026. It affects widely used distributions including Debian Bookworm, Debian Trixie...
Two critical vulnerabilities have been reported on September 7, 2026. CVE-2026-15409 is a critical Server-Side Request Forgery (SSRF) vulnerability in SonicWall SMA1000 series devices, allowing remote attackers to execute unintended HTTP requests. This vulnerability has been actively exploited since...
Public Exploits
Checking GitHub for proof-of-concept code…