Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A critical vulnerability (CVE-2026-65105) in NVIDIA's NemoClaw tool enables attackers to gain unauthenticated access to the local Ollama model server through a single visit to a malicious webpage. Discovered by Cyera's Oasis Security, the flaw stems from a network misconfiguration that exposes the O...
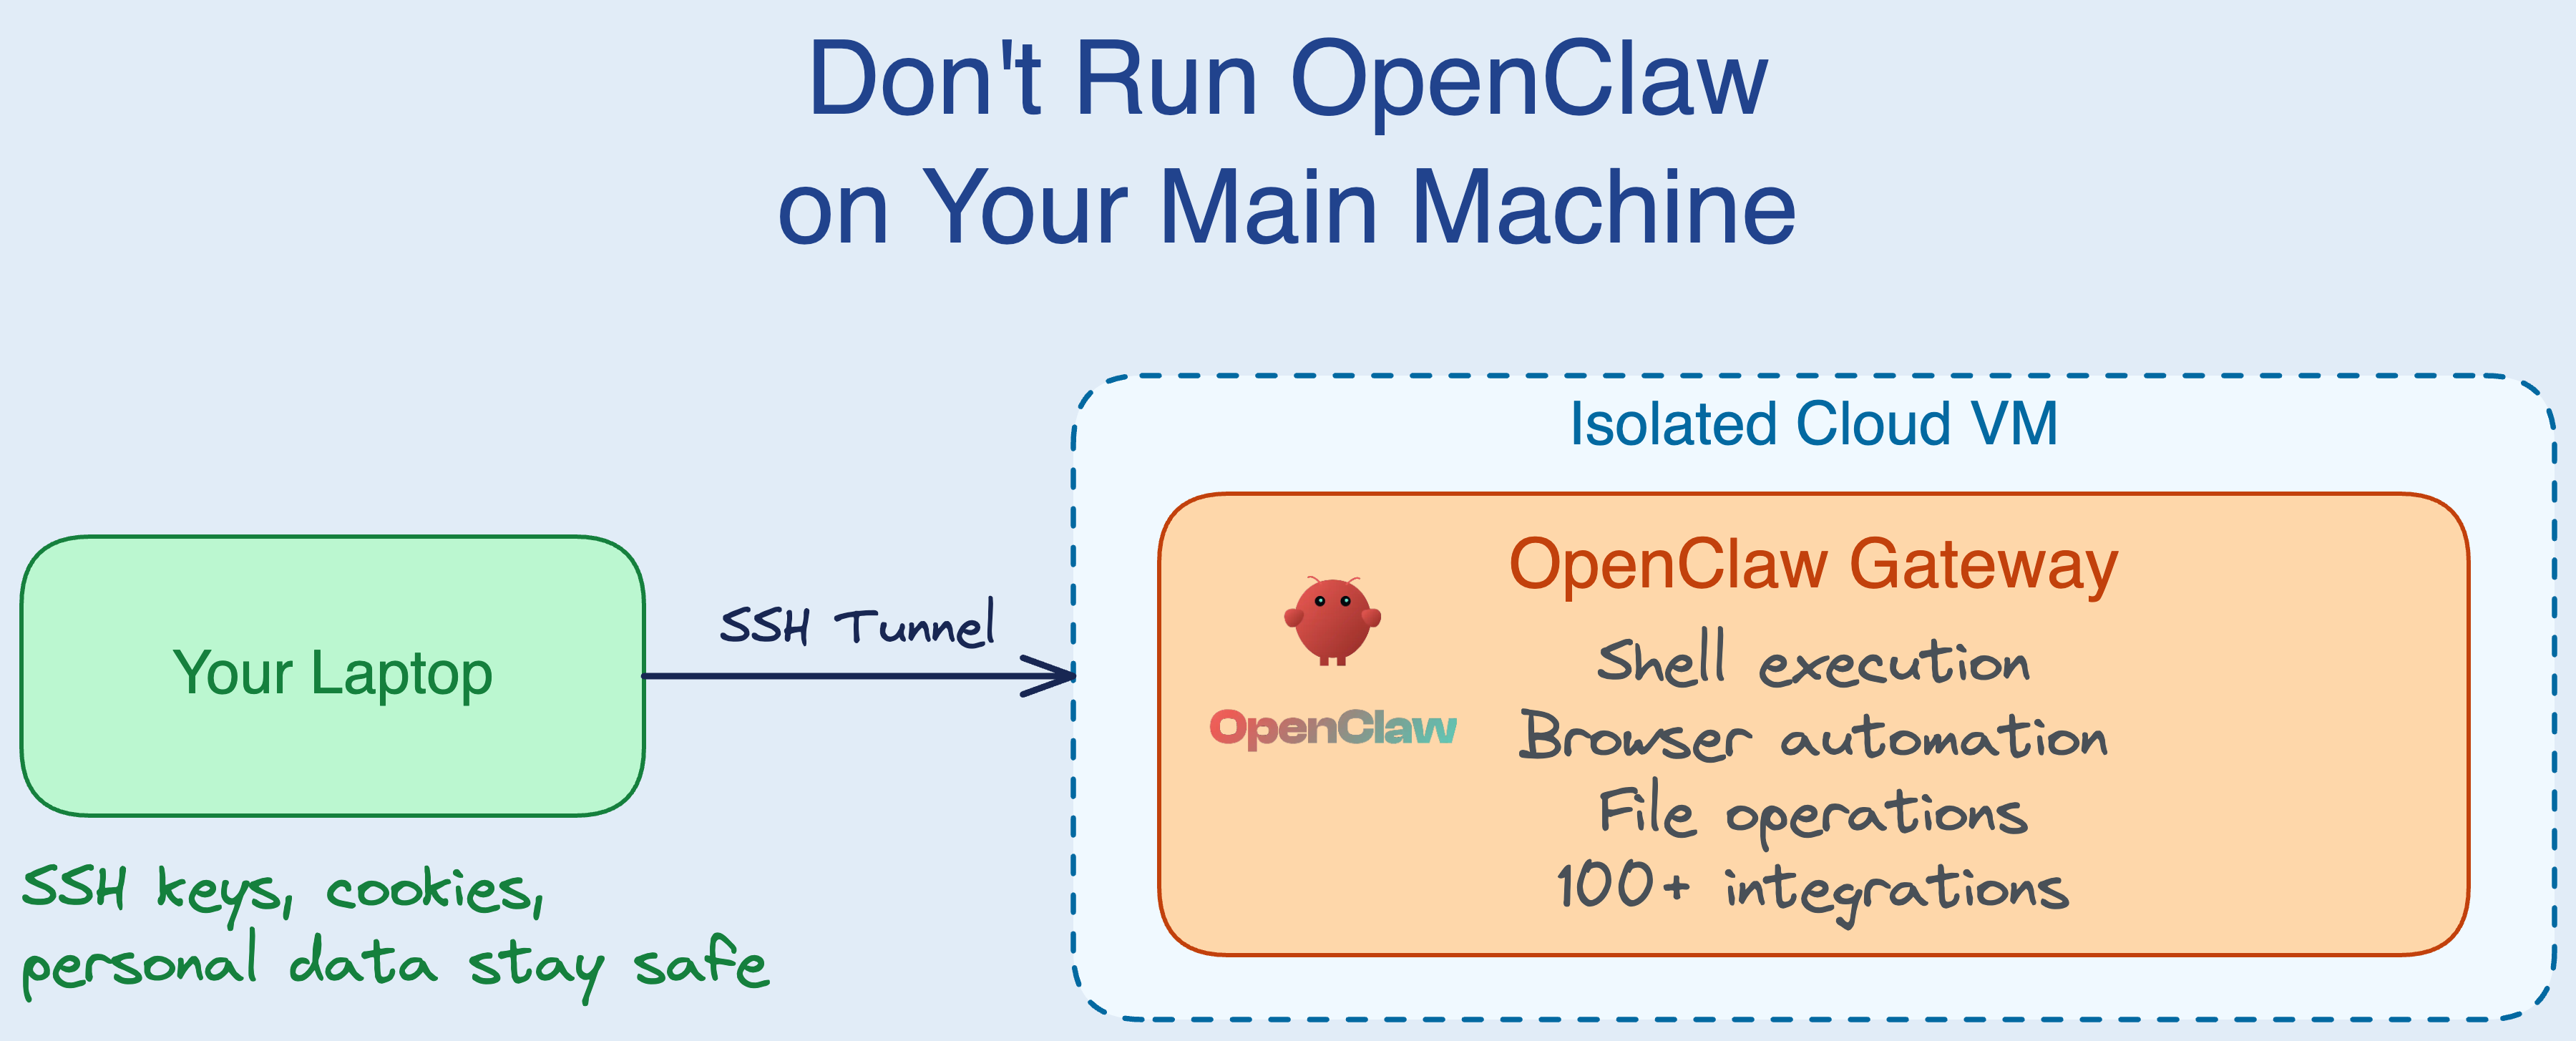
OpenClaw, a crayfish-themed AI platform, has disclosed high-risk vulnerabilities, including CVE-2026-25253, which allows remote code execution via malicious links. The vulnerabilities pose significant risks to users, particularly developers and companies utilizing the platform. Tencent Cloud enginee...
OpenAI has integrated its ChatGPT subscriptions as the authentication layer for OpenClaw, an open-source AI agent framework with 3.2 million users. This move follows Anthropic's decision to block access to its Claude subscriptions on the same platform. OpenClaw, created by Peter Steinberger, has rap...
On February 25, 2026, Nous Research launched Hermes Agent v0.1.0, which rapidly evolved to v0.8.0 by April 8, 2026. Concurrently, OpenClaw, a leading open-source AI Agent project, gained 346,000 stars on GitHub but faced significant security challenges, including 138 disclosed vulnerabilities within...