Frequency
4
occurrences
First Seen
September 11, 2026
Last Seen
October 14, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A recent wave of cyber attacks orchestrated by AI agents has exploited vulnerabilities in systems like PaperCut, leading to significant breaches across various sectors including education and healthcare. The attacks utilized CVE-2026-81578 and CVE-2026-82078 to achieve remote code execution without...
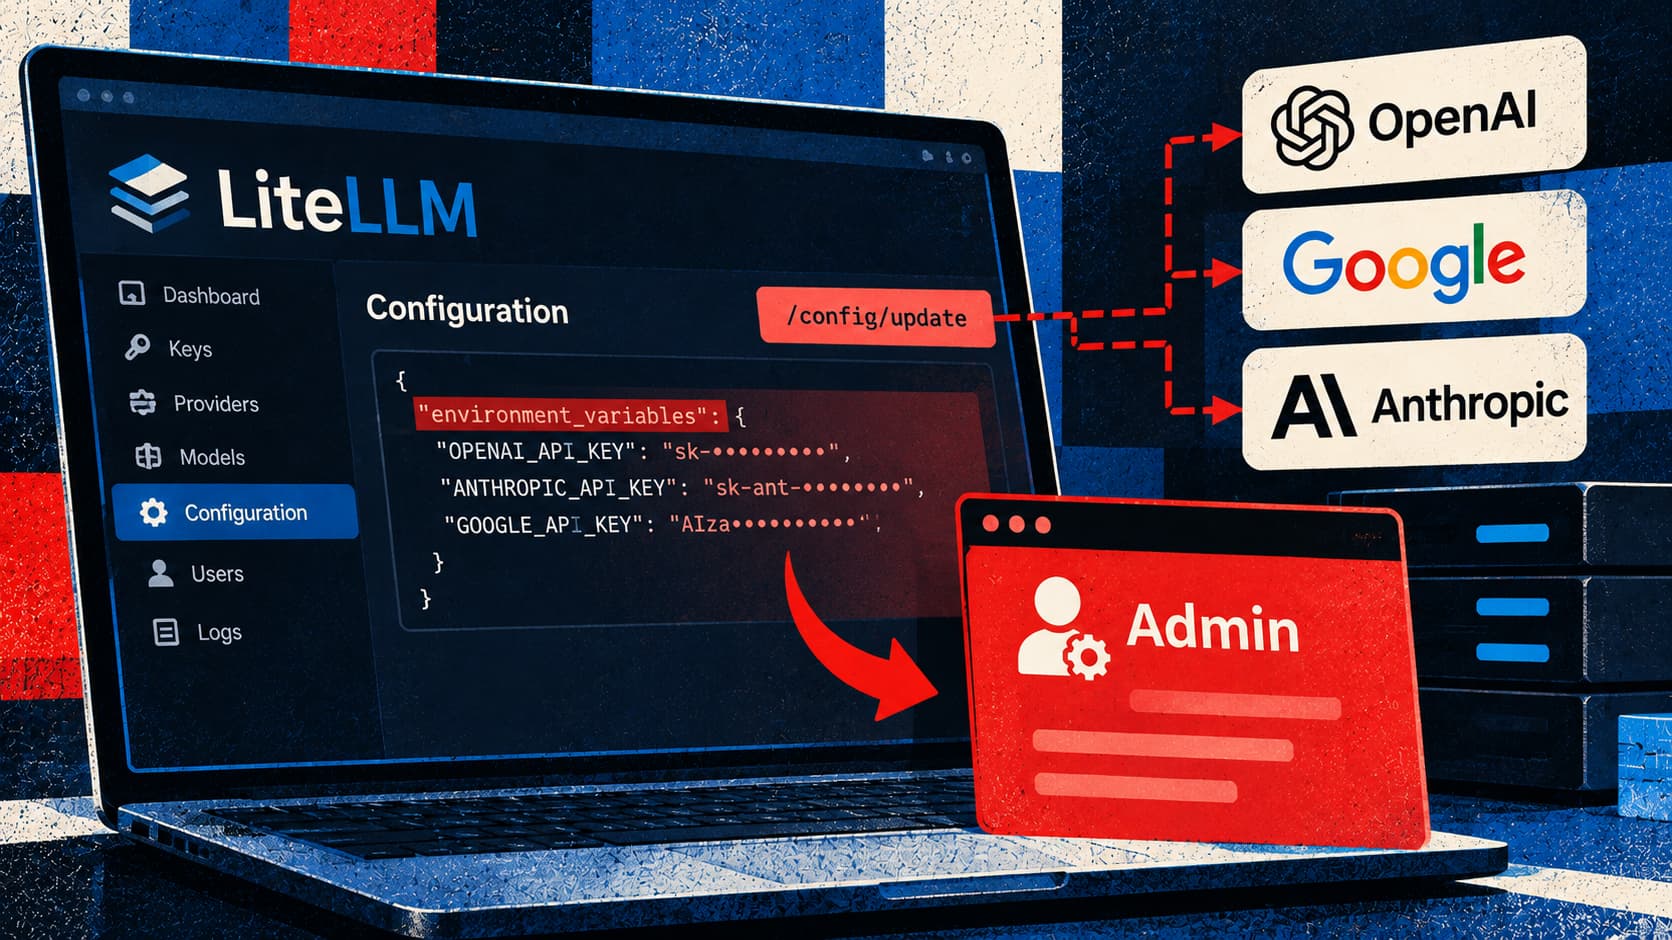
Check Point Research identified two significant vulnerabilities in LiteLLM, an open-source LLM gateway, tracked as CVE-2026-35029 and CVE-2026-59823. CVE-2026-35029 allows low-privileged users to perform administrative actions, potentially leading to full system takeover. CVE-2026-59823 enables atta...
Public Exploits
Checking GitHub for proof-of-concept code…