Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
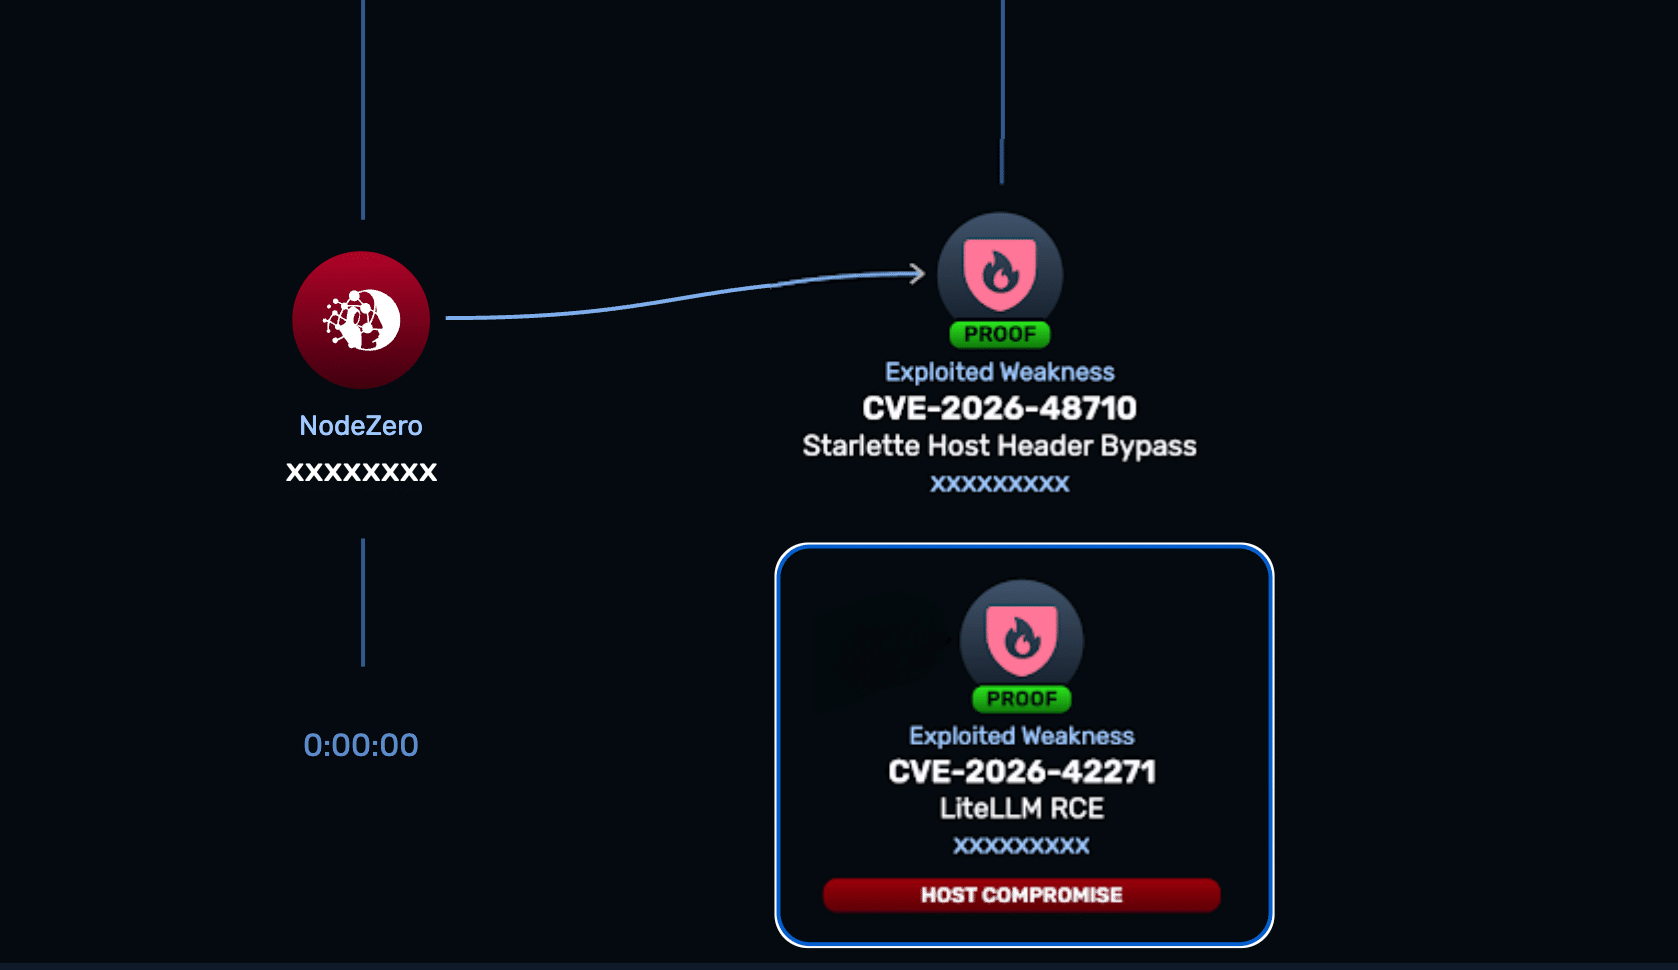
A critical command injection vulnerability, CVE-2026-42271, in LiteLLM, an open-source AI gateway, allows unauthenticated remote code execution (RCE) when chained with CVE-2026-48710, a Host header validation bypass in Starlette. This exploit affects LiteLLM versions 1.74.2 to 1.83.6, with the U.S....
CISA has mandated federal agencies to patch a critical vulnerability in Check Point VPN products within 72 hours due to active exploitation by the Qilin ransomware group. The vulnerability, tracked as CVE-2026-42271, was first disclosed on May 8, 2026, and has been exploited since May 7, affecting n...
The PoeLLM malware campaign, tracked by Lumen Technologies' Black Lotus Labs, has infected over 3,400 servers since April 2026, primarily targeting exposed AI services like LiteLLM and Ollama. The malware cleverly hides its command-and-control (C2) server addresses within a poem posted on GitHub, al...
Google's Threat Intelligence Group (GTIG) reports that software vulnerability disclosures doubled from 5,045 in January 2026 to 10,740 in August 2026, largely influenced by AI-assisted discovery. Notably, 50% of AI-discovered vulnerabilities enable remote code execution (RCE), compared to 26% of non...