Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
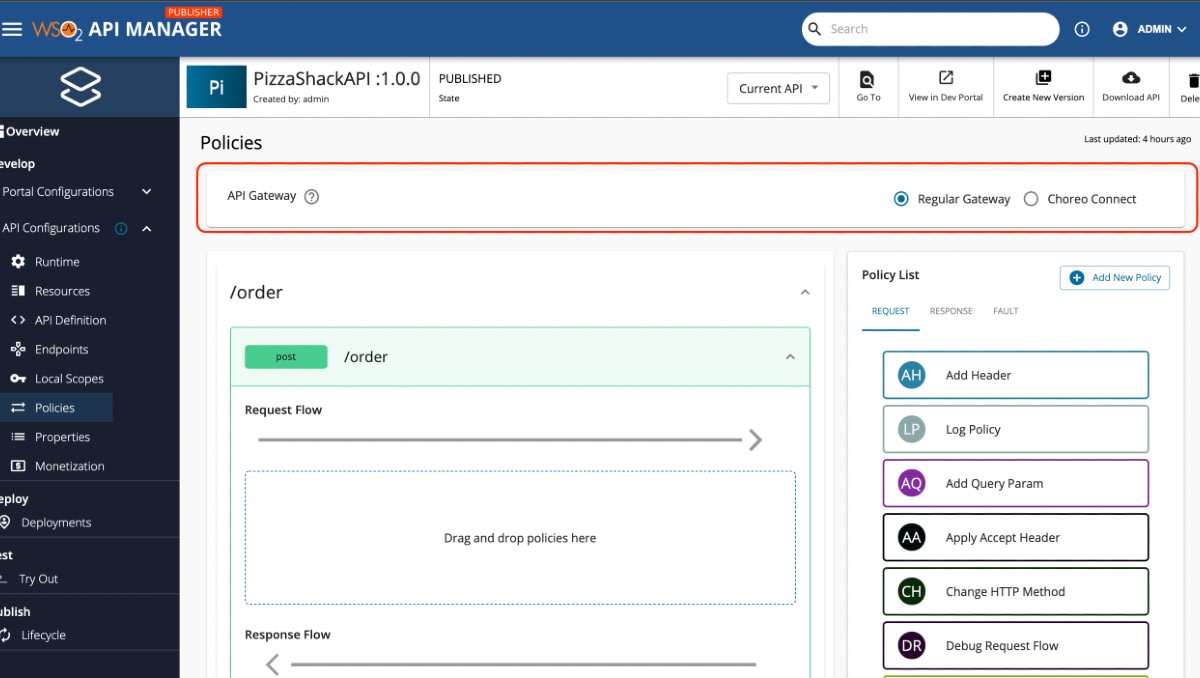
A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffi...
On August 11, 2026, Adobe released a security update addressing CVE-2026-71362, a critical Incorrect Authorization vulnerability in Adobe Commerce, Adobe Commerce B2B, and Magento Open Source. This flaw allows unauthenticated account takeover, enabling attackers to switch customer sessions without a...
WSO2 has disclosed CVE-2025-11969, a critical access control vulnerability in the System REST APIs of WSO2 API Manager and related products. This flaw allows users with low privileges to perform unauthorized actions, including executing administrative tasks. The vulnerability has a CVSS score of 9.4...