Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Dell has disclosed a critical vulnerability (CVE-2026-86360) in its System Update (DSU) tool, affecting versions prior to 2.3.0.0. This path traversal flaw allows unauthenticated remote attackers to execute arbitrary code with root privileges on vulnerable PowerEdge servers. The vulnerability has a...
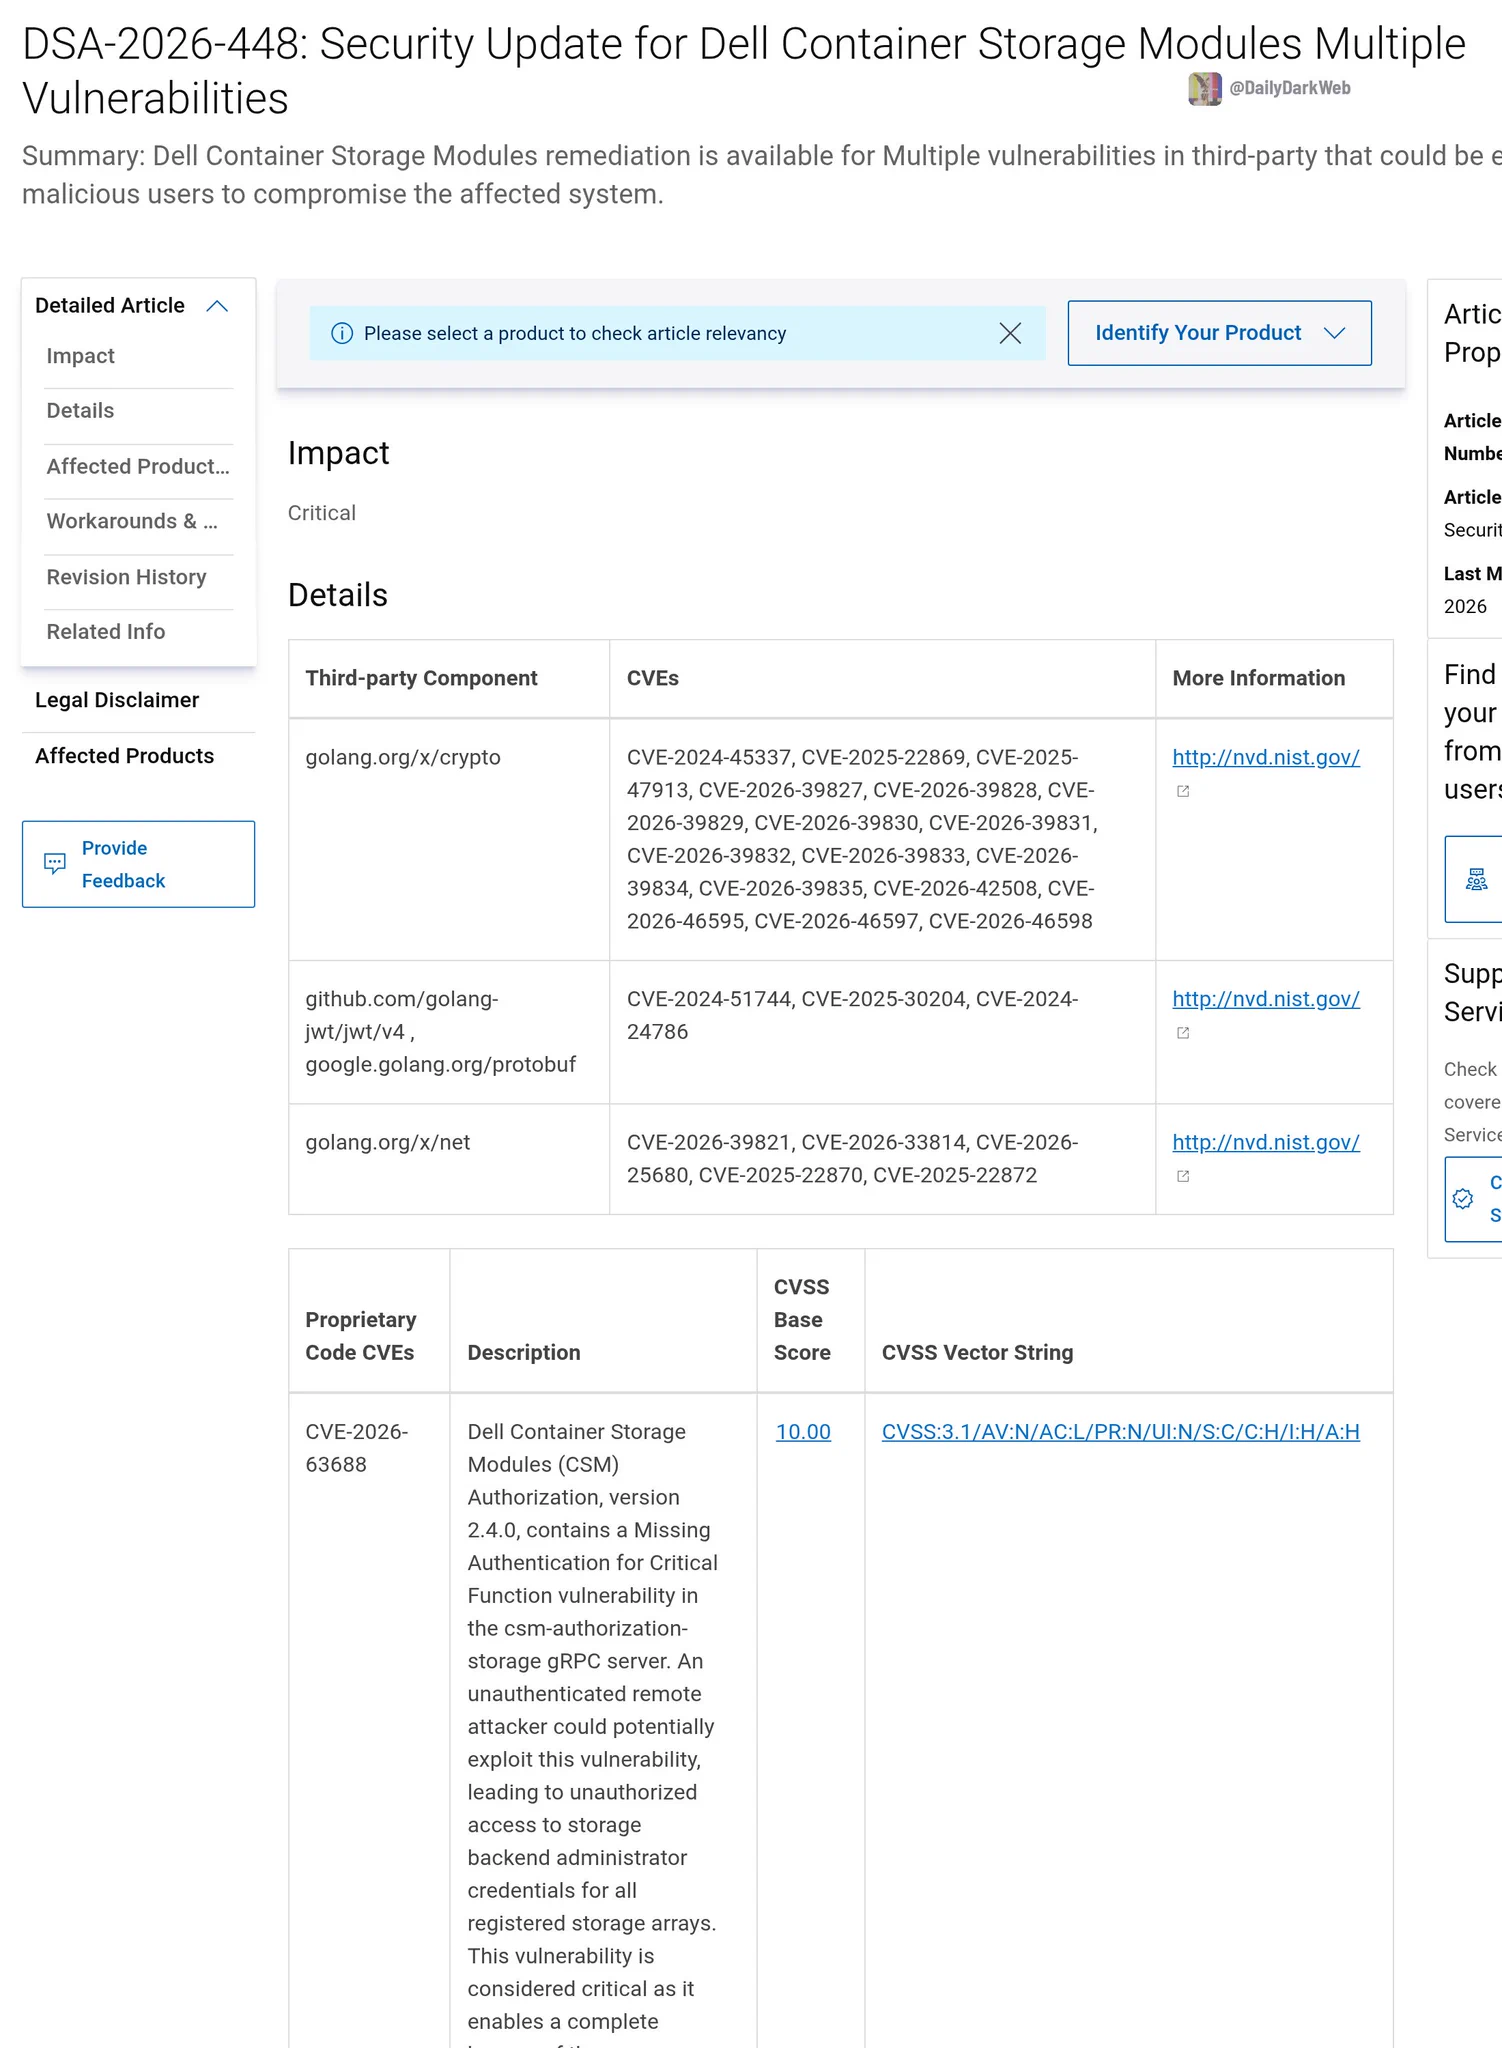
Dell has disclosed multiple vulnerabilities in its Container Storage Modules (CSM) affecting Kubernetes environments. The most severe flaws, with a CVSS score of 10.0, enable unauthenticated remote attackers to gain full administrative control over storage infrastructure. These vulnerabilities inclu...
Dell has issued security updates for six critical vulnerabilities in its Container Storage Modules (CSM) that could enable unauthenticated attackers to gain administrative access to storage backends and root control over Kubernetes clusters. The vulnerabilities, tracked as CVE-2026-63688 and CVE-202...