Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
SonicWall disclosed two critical vulnerabilities in its SMA1000 series appliances, CVE-2026-83548 and CVE-2026-83549, which are being actively exploited. CVE-2026-83548 is a pre-authentication server-side request forgery (SSRF) vulnerability rated 10.0 on the CVSS scale, allowing unauthenticated att...
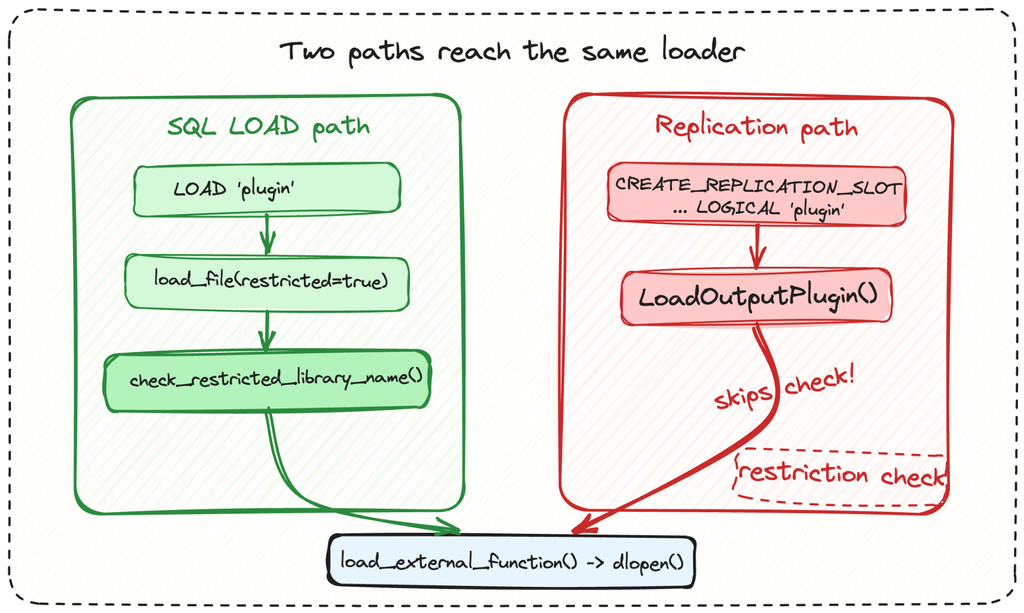
A critical vulnerability, tracked as CVE-2026-6471 and dubbed PostGREShell, has been discovered in PostgreSQL, affecting versions since 2014. This flaw allows attackers with low-privilege replication accounts to execute arbitrary code on the database server, leading to full database and server compr...
Multiple vulnerabilities were discovered in PostgreSQL, including issues with COPY FROM STDIN, extended statistics ownership, and USAGE privilege checks. These vulnerabilities, identified as CVE-2026-6464, CVE-2026-6469, and CVE-2026-6470, could allow authenticated users to execute arbitrary SQL com...
On September 3, 2026, multiple security updates were released for PostgreSQL versions 14, 15, 16, and 18, addressing a total of 24 vulnerabilities. Key vulnerabilities include CVE-2026-6464, which allows early failure processing of data lines as commands, and CVE-2026-14664, which involves a heap bu...