Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
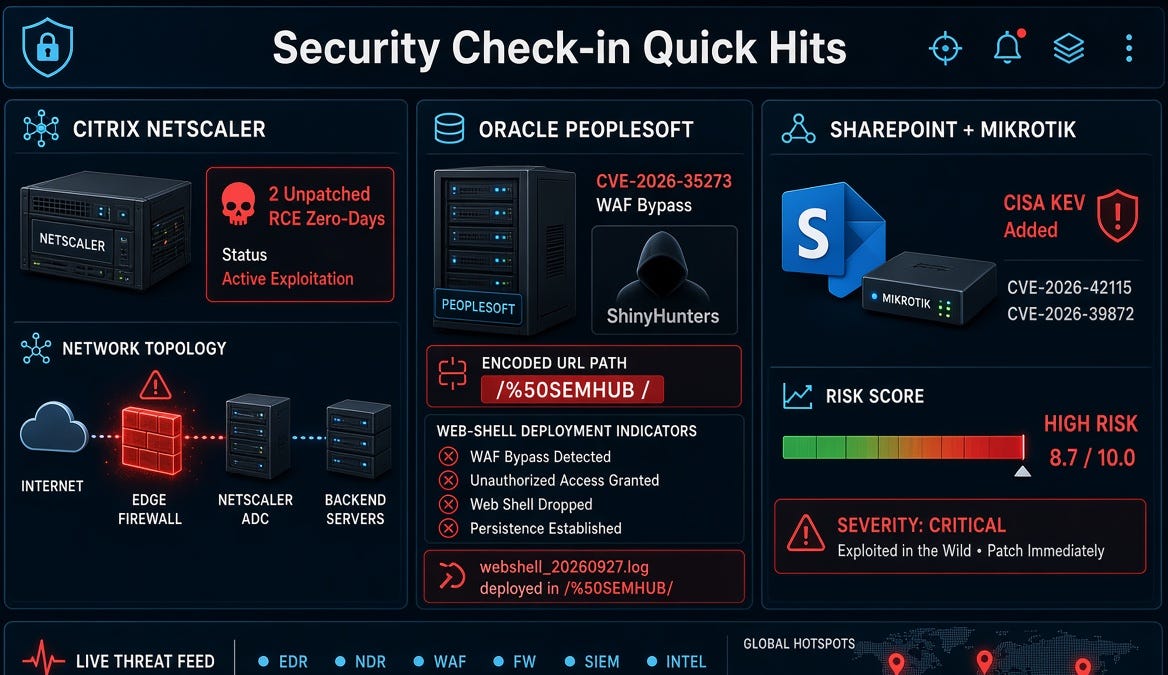
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
Recent reports indicate multiple critical vulnerabilities are being actively exploited, including zero-day exploits for Citrix NetScaler ADC and Gateway (CVE-2026-88771, CVE-2026-88772) and PaperCut NG/MF. The vulnerabilities allow unauthenticated remote code execution, posing significant risks to a...
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, with a CVSS score of 9.8. This path traversal vulnerability allows unauthenticated attackers to write arbitrary files on affected systems via crafted HTTP or HTTPS requests. The flaw has been confirmed to be ac...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two vulnerabilities to its Known Exploited Vulnerabilities catalog, confirming active exploitation. The vulnerabilities include CVE-2026-65660, a code injection flaw in Microsoft SharePoint Server, which allows authenticated...