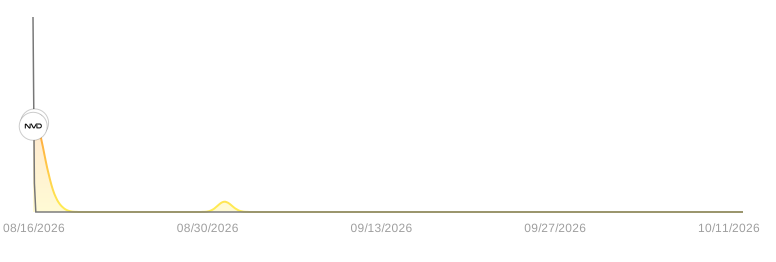
Frequency
4
occurrences
First Seen
August 16, 2026
Last Seen
August 17, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A critical vulnerability (CVE-2026-73046) has been identified in SiYuan versions prior to 3.7.4, allowing unauthenticated remote attackers to exploit improper authentication restrictions in the CheckAuth() middleware. The flaw enables brute-force attacks on the admin access code via HTTP Basic Authe...
Public Exploits
Checking GitHub for proof-of-concept code…