Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
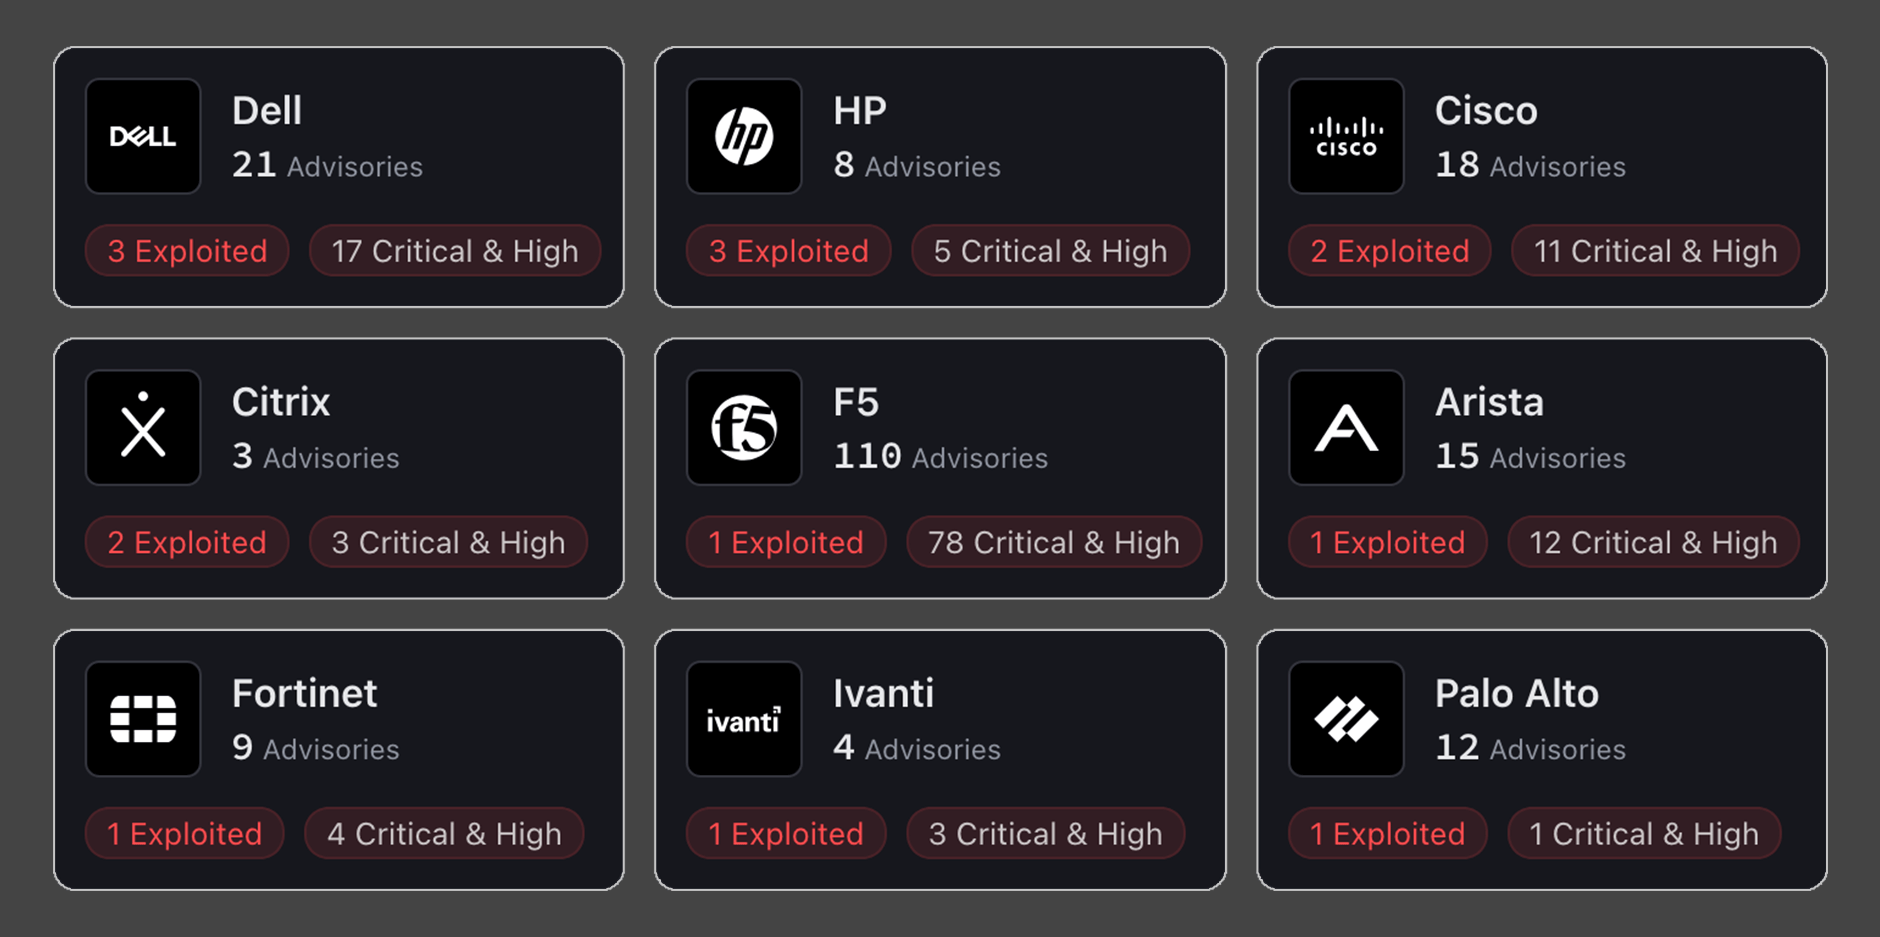
Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass a...
On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, en...
Recent reports indicate multiple critical vulnerabilities are being actively exploited, including zero-day exploits for Citrix NetScaler ADC and Gateway (CVE-2026-88771, CVE-2026-88772) and PaperCut NG/MF. The vulnerabilities allow unauthenticated remote code execution, posing significant risks to a...
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, with a CVSS score of 9.8. This path traversal vulnerability allows unauthenticated attackers to write arbitrary files on affected systems via crafted HTTP or HTTPS requests. The flaw has been confirmed to be ac...