Frequency
3
occurrences
First Seen
November 16, 2026
Last Seen
November 16, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
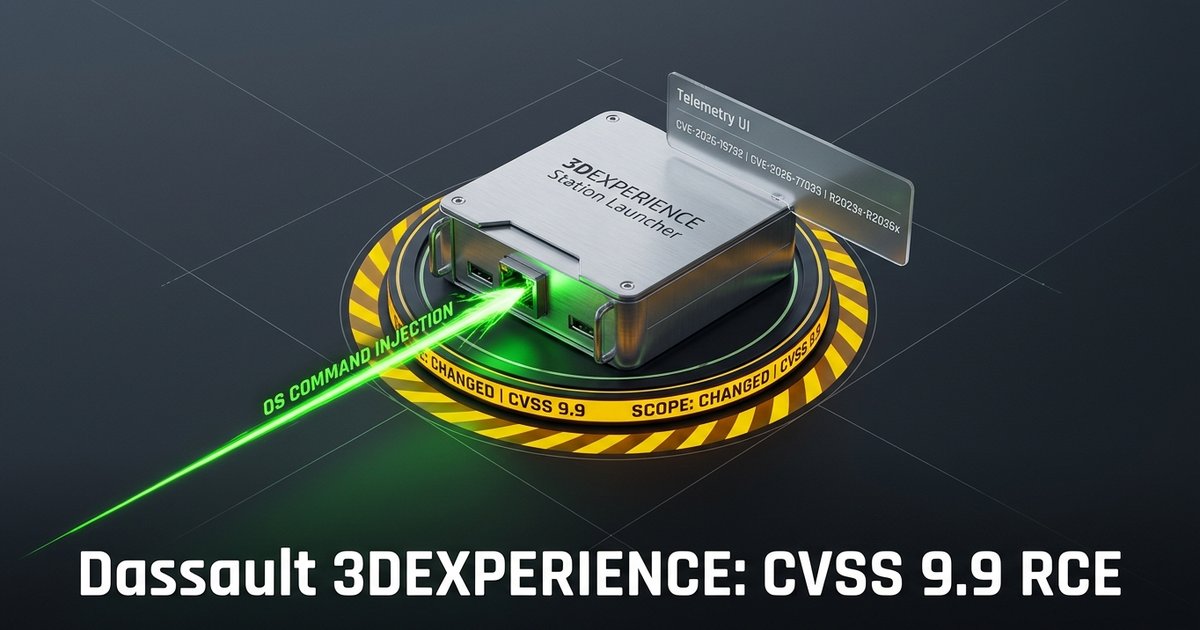
On November 16, 2026, Dassault Systèmes disclosed two critical OS command injection vulnerabilities in the Station Launcher App of the 3DEXPERIENCE platform, identified as CVE-2026-19732 and CVE-2026-77033. These vulnerabilities affect releases R2023x through R2026x, allowing low-privileged authenti...
Public Exploits
Checking GitHub for proof-of-concept code…